
Evidentiary Architecture™ Series | Article 5 of 20
Building the Defensible Enterprise through Governance Evidence
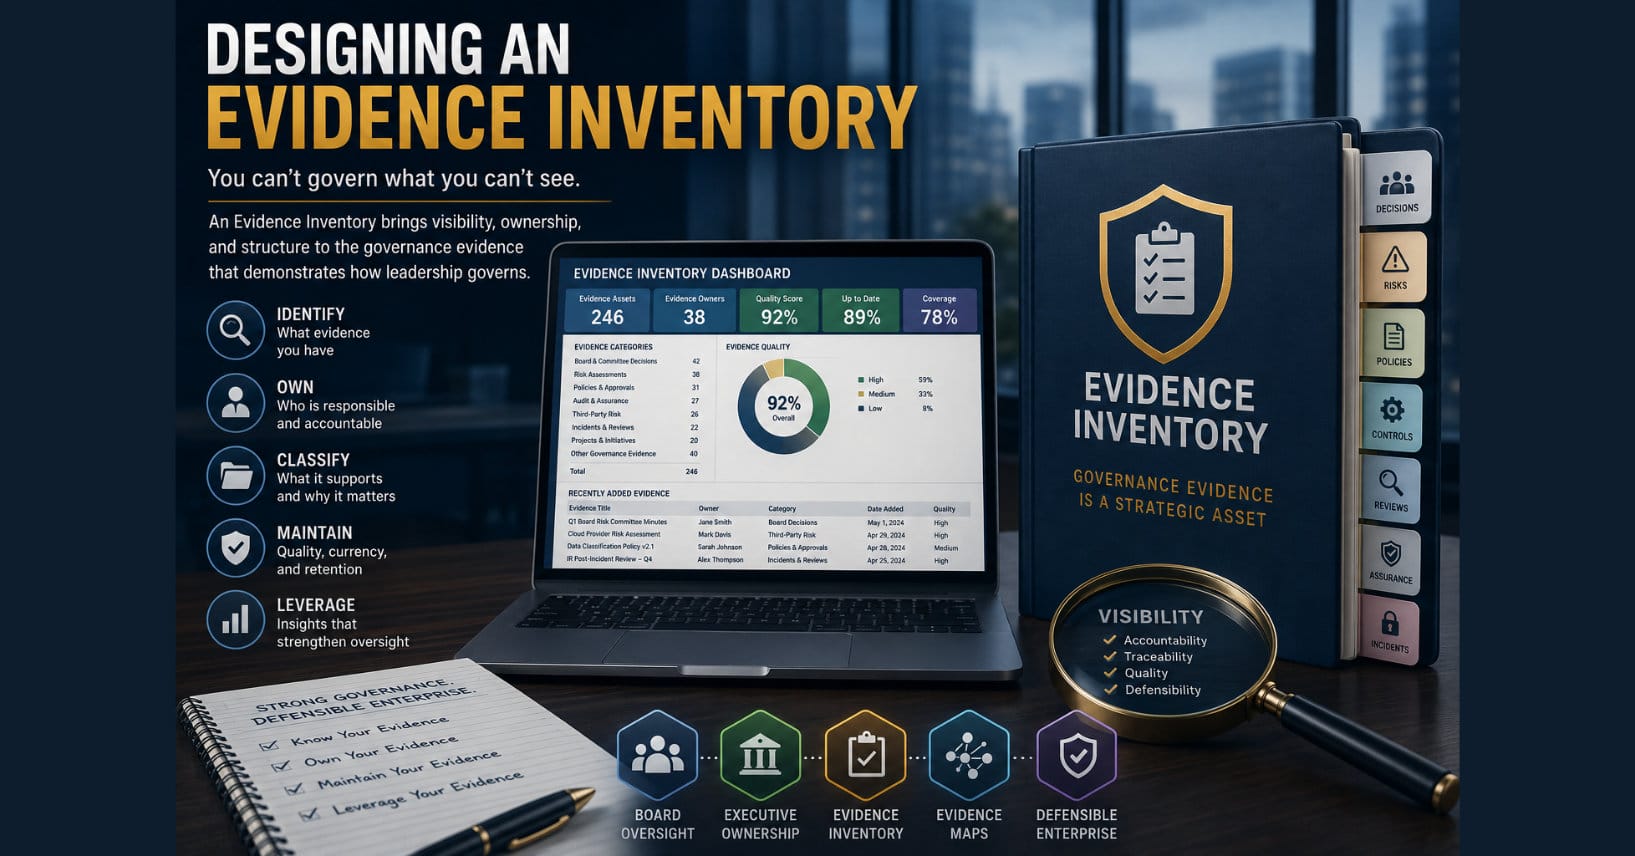
What is Evidentiary Architecture™? It is the intentional design of governance processes that naturally produce trustworthy, traceable, and defensible evidence as decisions are made. Rather than relying on disconnected documentation or reconstructing governance after a cyber incident, organizations can design evidence into every governance activity. This article formally introduces Evidentiary Architecture™ as a new architectural discipline that strengthens board oversight, demonstrates reasonable cybersecurity governance, and builds the foundation of a defensible enterprise.
Throughout this series, we’ve identified a recurring problem.
Organizations produce enormous amounts of documentation.
They retain countless records.
Their security tools generate millions of technical artifacts.
Yet when leadership is asked to demonstrate reasonable cybersecurity governance, the evidence is often fragmented, incomplete, or reconstructed long after the fact.
The issue is not a lack of information.
It is a lack of design.
That missing design discipline is Evidentiary Architecture™.
A Working Definition
Evidentiary Architecture™ is the intentional design of governance processes that naturally produce trustworthy, traceable, and defensible evidence as decisions are made.
Notice what this definition does not say.
It is not a document management system.
It is not a records retention program.
It is not another compliance framework.
It is not a governance, risk, and compliance (GRC) platform.
Technology may support Evidentiary Architecture™, but technology is not the architecture.
The architecture is the intentional design that ensures governance continuously produces evidence worthy of trust.
Beyond Documentation
Earlier in this series, we distinguished four different forms of organizational information.
Those distinctions become even more important here.
Documentation communicates organizational intent.
Policies explain expectations.
Standards establish requirements.
Procedures define how work should be performed.
Documentation answers:
“What should happen?”
Records preserve events that occurred.
Board minutes.
Training logs.
Risk acceptance forms.
Vendor agreements.
Incident reports.
Records answer:
“What happened?”
Artifacts demonstrate operational activity.
Security dashboards.
Audit reports.
Vulnerability scans.
Threat intelligence.
SIEM alerts.
Artifacts answer:
“What did the organization do?”
Governance evidence connects all of these into an explainable chain of leadership oversight.
It answers:
“How did leadership exercise informed, accountable governance?”
Evidentiary Architecture™ exists to intentionally create that final layer.
Governance Is a System
Many organizations think of governance as a series of meetings.
Quarterly board meetings.
Monthly risk committee meetings.
Annual policy reviews.
Periodic audits.
These are governance activities.
They are not governance architecture.
Architecture asks a different question.
How should these activities connect so that every important governance decision leaves behind a complete, trustworthy evidence trail?
That requires intentional design.
Evidence Should Flow
Imagine a manufacturing plant.
Raw materials enter one side.
Finished products leave the other.
The process is engineered.
The same principle applies to governance.
Information enters the governance process.
Risk assessments identify concerns.
Management develops recommendations.
Leadership evaluates alternatives.
Boards allocate resources.
Responsibilities are assigned.
Implementation occurs.
Performance is monitored.
Independent validation follows.
Each stage should naturally produce evidence that feeds the next.
Evidence should flow through governance rather than appearing as isolated documents scattered across the enterprise.
Designed, Not Discovered
Today, many organizations discover governance evidence only after an incident.
Someone searches email archives.
Meeting minutes are reviewed.
PowerPoint presentations are collected.
Risk registers are exported.
Investigators begin connecting isolated pieces into a timeline.
That process is reactive.
Evidentiary Architecture™ reverses the model.
Instead of asking:
“What evidence can we find?”
Organizations ask:
“What evidence should this governance activity produce?”
That simple shift transforms governance.
Evidence becomes an intentional output rather than an accidental byproduct.
Every Governance Decision Creates Evidence
Consider a board approving a significant cybersecurity investment.
The decision itself is only one part of the governance story.
A complete evidence trail should naturally include:
- The risk that prompted discussion.
- The information reviewed by leadership.
- Alternatives that were considered.
- The rationale supporting the decision.
- The authority responsible for approval.
- Resources committed.
- Accountability assigned.
- Expected outcomes.
- Review milestones.
- Validation that implementation occurred.
None of these elements require additional meetings.
None require new committees.
They simply require governance to be intentionally designed so these evidence elements are captured as decisions occur.
A Strategic Enterprise Capability
Organizations often treat evidence as something required for audits.
That perspective is too narrow.
Governance evidence supports far more than regulatory compliance.
It strengthens board oversight.
It improves executive decision-making.
It accelerates incident response.
It supports cyber insurance claims.
It reduces litigation risk.
It improves organizational memory.
Most importantly, it demonstrates that leadership fulfilled its governance responsibilities with discipline and accountability.
Evidence is not merely a legal asset.
It is a strategic enterprise asset.
The Foundation of a Defensible Enterprise
Every mature enterprise architecture exists for a reason.
Security architecture protects systems.
Data architecture protects information.
Application architecture enables business capability.
Evidentiary Architecture™ protects something equally valuable:
The organization’s ability to demonstrate that governance functioned as intended.
That capability is becoming increasingly important.
Boards are no longer judged solely by whether cyber incidents occur.
They are increasingly judged by whether they can demonstrate reasonable oversight before those incidents occurred.
That is why Evidentiary Architecture™ is not simply another governance framework.
It is a new architectural discipline—one designed to ensure that governance continuously produces trustworthy, traceable, and defensible evidence.
Because in the end, organizations are not remembered for the documents they collected.
They are judged by the evidence they can produce.
Governance Takeaway
Evidentiary Architecture™ is the intentional design of governance processes that produce trustworthy, traceable, and defensible evidence as decisions are made. It transforms governance evidence from an accidental byproduct into a strategic enterprise capability that demonstrates informed leadership and reasonable oversight.
Coming Next
Governance Produces Decisions. Decisions Produce Evidence.
Every governance activity ultimately produces a decision—or confirms an existing one. Those decisions should naturally generate evidence that explains what was decided, why it was decided, who approved it, and how accountability was assigned. In the next article, we’ll explore why decisions are the fundamental building blocks of governance evidence and how organizations can begin designing evidence flows around them.