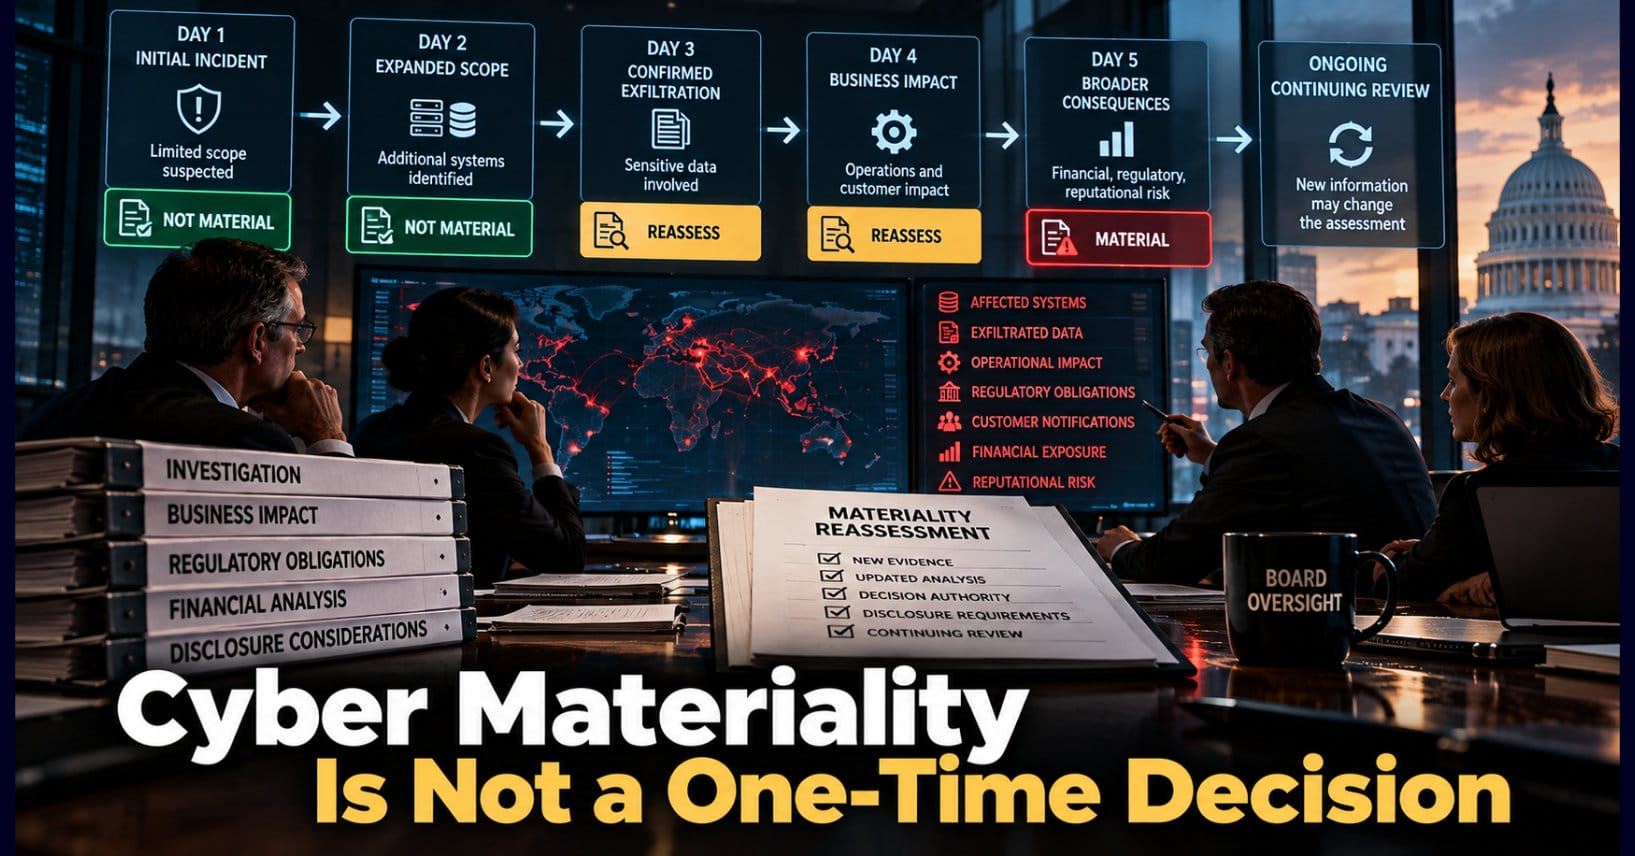
Summary
Cybersecurity incidents rarely reveal their full consequences when first discovered. An incident initially considered immaterial may become material as investigators uncover additional data exposure, operational disruption, financial consequences, or regulatory obligations.
Under the SEC’s cybersecurity disclosure framework, public companies must make materiality determinations without unreasonable delay and generally disclose material incidents within four business days of that determination. But effective governance extends beyond the initial assessment and regulatory filing.
This article examines why cybersecurity materiality requires continuing evaluation, clearly assigned decision authority, defined reassessment triggers, and defensible documentation. It distinguishes technical incident severity from securities-law materiality and explains why changing an assessment does not necessarily indicate that the original decision was improper.
The article also introduces the Control Bill of Materials (CBOM) as a potential architectural mechanism for connecting failed controls to affected business processes, obligations, and risk assumptions.
Through the Cyber Governance Center’s Defensible Evidence Framework™ and Evidentiary Architecture™, the article establishes a governance progression:
Initial Assessment → New Evidence → Reassessment → Decision Authority → Disclosure → Continuing Review
The central message: organizations must be able to demonstrate not only what they determined about an incident’s materiality, but why, when, under whose authority, and how the determination evolved as new information became available.
A cybersecurity incident occurs.
The security team investigates.
Management evaluates the potential consequences.
Legal counsel reviews the available information.
Someone determines whether the incident is material.
The decision is documented.
And the organization moves forward.
That sequence appears reasonable.
It is also incomplete.
Because cybersecurity incidents rarely reveal their full consequences at the moment they are discovered.
An intrusion initially believed to affect a single application may later involve multiple business systems.
A suspected data exposure may become a confirmed compromise of sensitive customer information.
An operational disruption expected to last several hours may continue for days.
A third-party incident may reveal dependencies that management did not previously understand.
And a financial impact initially considered manageable may expand as recovery costs, contractual consequences, regulatory obligations, and business interruption accumulate.
The facts change.
The organization’s understanding changes.
And sometimes the materiality assessment must change with them.
Cybersecurity materiality is not simply a decision made at one moment. It is a determination that must remain supportable as relevant facts emerge.
For boards and executive leadership, that creates a governance obligation extending beyond the initial disclosure decision.
The organization must be able to demonstrate not only what it concluded, but why it reached that conclusion, what information was available, who possessed decision authority, and whether subsequent developments required reconsideration.
The most consequential question may arise months later.
Can management reconstruct why its materiality assessment changed—or why it did not?
The SEC Changed the Disclosure Conversation
The Securities and Exchange Commission’s cybersecurity disclosure rules established a specific framework for public companies evaluating material cybersecurity incidents.
Under Item 1.05 of Form 8-K, covered registrants must disclose a cybersecurity incident they determine to be material.
In this context, saying that a cybersecurity incident is material means that a reasonable investor would consider information about the incident important when making an investment or voting decision, or that the information would significantly alter the “total mix” of information available to that investor. Materiality is therefore not determined simply by whether an incident is technically severe, expensive, or disruptive. The organization must evaluate the incident’s actual and reasonably likely consequences in the context of the company as a whole, including relevant quantitative and qualitative factors.
The disclosure must address the material aspects of the incident’s nature, scope, and timing, as well as its material impact or reasonably likely material impact.
The filing generally must occur within four business days after the materiality determination, subject to the rule’s limited provisions for authorized delays.
Importantly, the SEC requires companies to make their materiality determinations without unreasonable delay after discovering an incident.
The four-business-day disclosure period does not begin merely because an incident was discovered.
It begins when the company determines that the incident is material.
That distinction is essential.
It also creates a governance challenge.
Organizations must investigate sufficiently to make a reasonable materiality determination without allowing the investigation itself to become an unjustified reason for postponing the decision.
The SEC’s standard is not based solely on the technical severity of the incident.
Materiality is evaluated from the perspective of a reasonable investor, considering whether the information would significantly alter the total mix of information available for an investment decision.
That requires consideration of quantitative and qualitative factors.
A relatively small financial loss may accompany significant operational, regulatory, reputational, or strategic consequences.
Conversely, a technically serious cybersecurity incident may not necessarily be material to the registrant.
The determination depends on the relevant facts and circumstances. (SEC)
The First Assessment Is Made With Incomplete Information
Consider a hypothetical publicly traded manufacturer.
On Monday morning, its cybersecurity team detects suspicious activity affecting an internal application.
Initial investigation suggests that an unauthorized user accessed a limited number of files.
The application does not directly support production operations.
No evidence indicates that critical manufacturing systems were affected.
Management begins assessing the incident.
Based on the available information, the incident appears limited.
The organization documents an initial assessment that the incident is not material.
That conclusion may be reasonable.
But the investigation continues.
On Tuesday, forensic investigators identify additional unauthorized access involving an engineering repository.
On Wednesday, the company discovers that the repository contained proprietary manufacturing specifications.
On Thursday, investigators determine that the compromised credentials also provided access to systems supporting a major customer relationship.
By Friday, management learns that certain customer contracts contain notification and performance provisions that may be implicated.
The original incident has not necessarily changed.
The organization’s understanding of its consequences has.
The initial materiality determination may no longer be supportable.
That does not automatically mean the original assessment was improper.
A reasonable decision based on limited, reliable information can become outdated when additional evidence emerges.
The governance failure would arise if the organization continued relying on the original conclusion without evaluating the new information.
A defensible materiality decision must reflect the facts reasonably available when the decision is made—and remain subject to reconsideration when those facts materially change.
Materiality Is Not a Cybersecurity Severity Rating
One of the most persistent misunderstandings in incident governance is the assumption that cybersecurity severity and securities-law materiality are interchangeable.
They are not.
A cybersecurity team may classify an incident as critical because it involves privileged credentials, active exploitation, or a compromise of sensitive infrastructure.
That classification helps determine the urgency of technical response.
But it does not independently establish whether the incident is material to investors.
Likewise, an incident categorized as moderate by a security operations team may have consequences that make it material from an enterprise perspective.
Consider a breach affecting a relatively small number of records.
The technical scope may appear limited.
But suppose those records contain information central to a pending acquisition, a proprietary product launch, or a strategically important customer relationship.
The consequences may extend beyond the number of records involved.
Alternatively, a large-scale attack may be contained quickly, produce minimal business disruption, and have limited financial consequences.
Materiality cannot be established through incident volume alone.
The SEC has emphasized that companies should consider relevant quantitative and qualitative factors, including immediate and longer-term effects on operations, finances, reputation, and customer relationships.
Even insurance recovery does not automatically eliminate materiality.
An organization may recover certain direct financial losses while still experiencing significant operational or strategic consequences. (SEC)
The governance implication is straightforward.
Cybersecurity teams provide essential technical evidence. They should not be expected to determine enterprise materiality in isolation.
That determination requires an appropriately authorized process involving the relevant business, financial, legal, cybersecurity, and executive perspectives.
A 2026 Disclosure Illustrates the Problem
On June 10, 2026, iRhythm Holdings determined that a cybersecurity incident involving certain third-party-hosted business applications was material.
The company had identified unauthorized activity on June 8.
The following day, it received communications from a threat actor claiming to possess sensitive information and demanding payment.
The company subsequently confirmed that certain information had been exfiltrated.
Its Form 8-K stated that the materiality determination reflected the volume of potentially affected data.
At the same time, iRhythm reported that its investigation had not identified impacts on its products, clinical or medical device systems, patient safety, manufacturing and distribution operations, financial reporting systems, or ability to meet patient needs.
The company also explained that its investigation was continuing. (SEC)
This is a useful illustration of the distinction between materiality and operational disruption.
A company may determine that an incident is material even when certain critical business operations remain unaffected.
The information compromised, the potential consequences, and the circumstances surrounding the incident can independently influence the assessment.
The filing also demonstrates why the decision process must accommodate incomplete information.
A materiality determination does not require every investigative question to be resolved.
Nor does an ongoing investigation necessarily justify postponing a determination that can reasonably be made.
The challenge is to establish what is sufficiently known, what remains uncertain, and whether those uncertainties could affect the conclusion.
The Difference Between Reassessment and Amendment
There is an important legal distinction that organizations must preserve.
Reassessing an incident’s materiality is not identical to amending a previously filed disclosure.
Under the SEC’s cybersecurity disclosure framework, an Item 1.05 filing may need to be amended when required information concerning the material aspects of an incident’s nature, scope, timing, or impact was unavailable or undetermined at the time of the initial filing.
The company must provide the required additional information within the applicable regulatory timeframe after it becomes available or is determined.
However, not every new investigative fact automatically requires an amended Item 1.05 filing.
The obligation depends on the information involved and the applicable disclosure requirements.
Other securities-law disclosure obligations may also become relevant as circumstances evolve.
The distinction matters because an organization should not confuse its continuing internal responsibility to evaluate significant new information with an assumption that every reassessment produces a new public filing.
The SEC’s May 2024 staff statement also clarified that companies voluntarily reporting incidents not yet determined to be material, or determined to be immaterial, should generally use a different Form 8-K item, such as Item 8.01, rather than Item 1.05.
That guidance reinforces the importance of accurately distinguishing the organization’s current assessment from a formal determination of materiality. (SEC)
The governance objective is not to generate unnecessary disclosures.
It is to ensure that disclosure decisions remain timely, accurate, appropriately authorized, and supported by reliable evidence.
When Does Reassessment Become Necessary?
Organizations need a defined mechanism for identifying developments that warrant renewed materiality consideration.
That mechanism should not depend exclusively on someone remembering to reconvene the original decision-makers.
Reassessment triggers may include newly discovered data exposure, expansion of affected systems, unexpected operational disruption, increased recovery costs, regulatory developments, or changes in reasonably anticipated business consequences.
The relevant trigger is not necessarily the discovery of another technical indicator.
It is the emergence of information that could meaningfully affect the materiality analysis.
Consider several examples.
A company initially determines that an incident affected only nonproduction infrastructure.
Investigators later establish that the compromised credentials could access production systems.
A financial institution believes customer information remained protected.
Forensic analysis subsequently identifies confirmed exfiltration.
A manufacturer restores operations after a brief interruption.
Several days later, it discovers that compromised engineering systems require extensive validation before production can safely resume.
A service provider reports that an incident has been contained.
The customer subsequently learns that recovery will require replacing a critical integration and delaying a major commercial commitment.
Each development may warrant reassessment.
None automatically establishes materiality.
But each introduces information that could affect the original determination.
An effective governance process must recognize the distinction between receiving new information and evaluating its significance.
Reassessment should be triggered by changes in relevant facts, not merely by the passage of time.
Periodic review can supplement that process, particularly during prolonged investigations, but it should not substitute for event-driven escalation.
Decision Authority Cannot Be Ambiguous
Materiality determinations require technical evidence, but they are enterprise decisions.
The security operations center may identify unauthorized access.
The incident response team may establish the technical scope.
The chief information security officer may evaluate cybersecurity consequences.
The chief financial officer may assess financial exposure.
Legal counsel may advise on disclosure requirements.
Business executives may identify operational and strategic implications.
The board or an appropriate committee may exercise oversight.
But who possesses authority to make the materiality determination?
That question should have an established answer before an incident occurs.
An organization that relies on informal consensus may encounter serious problems when time-sensitive decisions become necessary.
Suppose the CISO considers an incident technically contained.
The CFO believes the financial consequences are manageable.
Legal counsel identifies potential contractual exposure.
The business unit responsible for the affected system anticipates a significant customer disruption.
Who resolves the disagreement?
What evidence must be considered?
Who can require further investigation?
Who has authority to determine that the available information is sufficient?
And who can reopen the assessment when new facts emerge?
These are governance design questions.
They cannot be answered by a severity matrix alone.
An effective materiality process should identify decision-makers, advisory responsibilities, escalation thresholds, documentation requirements, and reassessment authority.
It should also establish how disagreements are recorded and resolved.
The objective is not to eliminate professional judgment.
It is to ensure that judgment is exercised through an authorized and reconstructable process.
The Governance Chain Behind Materiality
A conventional incident response workflow focuses on detection, containment, eradication, recovery, and lessons learned.
Those activities remain essential.
But materiality governance requires an additional decision architecture.
The Cyber Governance Center’s Evidentiary Architecture™ provides a useful way to examine that relationship.
For materiality governance, the progression becomes:
Initial Assessment → New Evidence → Reassessment → Decision Authority → Disclosure → Continuing Review
Each stage has a distinct purpose.
Initial Assessment
The organization evaluates the incident using the information reasonably available at the time.
The assessment should distinguish established facts, reasonable estimates, unresolved questions, and assumptions.
It should identify the quantitative and qualitative factors considered.
New Evidence
Investigators, business owners, vendors, financial teams, or other responsible parties identify information that may affect the original assessment.
The information should be preserved with sufficient context to establish when it became known and how its significance was evaluated.
Reassessment
The organization determines whether the new information changes the materiality analysis.
This may result in confirmation of the existing conclusion, a revised conclusion, or a determination that further information is required without unreasonable delay.
Decision Authority
The appropriate decision-maker reviews the relevant evidence and authorizes the resulting determination.
The process should establish who participated, what information was considered, and how significant disagreements were resolved.
Disclosure
When applicable disclosure requirements are triggered, the organization prepares and submits the required information within the relevant deadlines.
The disclosure should reflect the material facts and reasonably likely consequences required by the applicable rules.
Continuing Review
The organization continues evaluating significant developments and determines whether additional disclosure, corrective action, or governance intervention is necessary.
This progression transforms materiality from an isolated conclusion into an accountable decision process.
It also establishes a basis for reconstructing how the organization’s understanding evolved.
The Role of a Control Bill of Materials
There is a related architectural concept worth introducing here.
A Control Bill of Materials, or CBOM, can be used as a structured inventory of governance and security controls, their owners, dependencies, obligations, and associated evidence.
Unlike the more established Software Bill of Materials, or SBOM, the term CBOM does not represent a universally adopted regulatory standard with one authoritative schema.
Its value here is architectural.
A well-designed CBOM can help an organization understand which controls support particular business processes and which obligations depend on those controls.
That relationship becomes important during a cybersecurity incident.
Suppose an investigation reveals that a privileged-access control protecting a critical financial application was ineffective.
The immediate technical finding concerns access control.
But the governance consequences may extend further.
Which business processes depended on that control?
Which regulatory or contractual obligations relied on it?
Which previously accepted risks assumed that the control was functioning?
Which other controls provided compensating protection?
And does the control failure change the organization’s assessment of the incident’s potential consequences?
A CBOM could help identify those relationships.
It would not independently determine materiality.
But it could provide structured evidence supporting reassessment by connecting a newly discovered control failure to the business functions, obligations, and assumptions potentially affected.
That is the distinction between maintaining a control inventory and maintaining an evidentiary architecture.
An inventory identifies what exists.
An evidentiary architecture helps establish what depends on it and why that dependency matters.
The Danger of a Materiality Decision Without an Evidence Trail
Consider a hypothetical organization that experiences a ransomware incident.
On the first day, management determines that the incident is not material.
The determination is entered into an incident management system.
The record contains a date, a status, and the name of the approving executive.
Two weeks later, the company determines that the incident is material.
The status changes.
A disclosure is prepared.
But the system does not preserve the original assessment rationale.
It does not identify which facts changed.
It does not record who received the new information.
It does not establish when the revised assessment was initiated.
And it does not explain why management changed its conclusion.
The organization may have made both decisions reasonably.
But it has limited evidence to demonstrate that fact.
That becomes consequential if regulators, auditors, insurers, shareholders, or litigants later examine the sequence.
Why was the incident initially considered immaterial?
What information supported that conclusion?
When did management first receive evidence suggesting greater consequences?
Why did the organization wait until the later date to change its assessment?
Was the decision made without unreasonable delay?
Did the appropriate decision-maker authorize the determination?
These questions cannot necessarily be answered through the final disclosure alone.
The organization needs a preserved record of the decision process.
A materiality conclusion without its supporting rationale is an incomplete governance record.
What Defensible Materiality Evidence Should Establish
The Cyber Governance Center’s Defensible Evidence Framework™ emphasizes that governance evidence must establish more than the existence of a completed process.
It must support reconstruction of consequential decisions.
For cybersecurity materiality, that means preserving several relationships.
- First, the organization should establish what information was available when each assessment occurred.
- Second, it should distinguish verified facts from assumptions, estimates, and unresolved investigative questions.
- Third, it should identify the individuals responsible for evaluating the relevant technical, financial, legal, and operational consequences.
- Fourth, it should establish who possessed authority to make or revise the materiality determination.
- Fifth, it should preserve the rationale supporting each consequential decision.
- Sixth, it should identify significant new information and establish when that information became available to responsible decision-makers.
- Seventh, it should connect reassessment decisions to applicable disclosure actions.
- Finally, it should preserve evidence of continuing review when material uncertainties remain.
These requirements do not imply that every email, meeting, or investigative note must become part of a permanent governance archive.
Evidence preservation must be proportionate, legally appropriate, and consistent with applicable retention requirements.
The objective is to preserve a reliable decision record.
That record should allow an independent reviewer to understand how the organization reached its conclusions without requiring the original decision-makers to reconstruct events entirely from memory.
A Board Cannot Oversee What Management Cannot Reconstruct
Boards are not expected to conduct forensic investigations or personally calculate the materiality of individual cybersecurity incidents.
Management is responsible for operating the relevant processes and making decisions through established authority.
But directors should expect assurance that the organization’s materiality governance is effective.
That assurance should extend beyond whether an Item 1.05 filing was submitted on time.
Boards should understand whether management can identify potentially material incidents, evaluate relevant consequences, make timely determinations, and respond when significant new information emerges.
Several questions deserve attention.
Who possesses authority to make a materiality determination?
Does the process incorporate both quantitative and qualitative factors?
How are disagreements among cybersecurity, finance, legal, and business leadership resolved?
What developments trigger reassessment?
Can management identify when significant new evidence became available?
Are prior assessments preserved when conclusions change?
Does the organization distinguish internal reassessment from external disclosure obligations?
And can management reconstruct the complete decision sequence after the incident?
These are not questions about technical incident response alone.
They concern enterprise decision authority, disclosure governance, and the reliability of management’s representations.
For audit committees, the implications are particularly important.
A timely filing is a measurable outcome.
But it does not independently demonstrate that the underlying materiality process was appropriately designed and executed.
The board needs assurance about the process that produced the filing.
The Risk of Treating Materiality as a Filing Exercise
There is a temptation to view cybersecurity materiality primarily as a regulatory reporting obligation.
An incident occurs.
The company evaluates whether an Item 1.05 filing is required.
The disclosure is prepared.
The filing is submitted.
The compliance requirement appears satisfied.
But materiality assessment is not merely a filing exercise.
It is a structured evaluation of the consequences of a cybersecurity incident for the enterprise and its investors.
The underlying information may also influence operational decisions, financial planning, customer communications, insurance notifications, contractual obligations, and board oversight.
Those activities are governed by different requirements and may involve different decision-makers.
They should not be collapsed into a single disclosure workflow.
For example, management may determine that an incident does not meet the securities-law materiality threshold while still requiring immediate operational intervention.
A cybersecurity event may be significant under a contractual notification requirement without being material to investors.
An incident may create substantial regulatory obligations even when its financial consequences remain limited.
Conversely, an incident may become material because of broader business consequences that are not captured by traditional cybersecurity severity classifications.
Effective governance recognizes these distinctions.
It does not assume that a single materiality decision resolves every organizational responsibility arising from the incident.
Materiality Decisions Have a History
One of the most important characteristics of cybersecurity materiality is that decisions occur within a sequence of developing knowledge.
At the beginning of an investigation, management may possess limited information.
As the investigation progresses, additional facts emerge.
Some initial assumptions are confirmed.
Others are disproven.
The organization may revise its understanding of the affected systems, information, operations, and financial consequences.
The decision record should preserve that history.
Not because every changed assessment indicates a failure.
But because the legitimacy of a decision often depends on what was reasonably known when it was made.
A conclusion reached on Monday should not automatically be judged as though management possessed information discovered on Friday.
Likewise, management should not continue relying on Monday’s conclusion after Friday’s evidence materially changes the circumstances.
This is the central challenge of defensible materiality governance.
The organization must demonstrate that its decisions were reasonable in context and responsive to relevant new information.
That requires a reliable chronology.
It requires documented authority.
It requires evidence connecting the information available to the decisions made.
And it requires a process capable of recognizing when an earlier conclusion needs to be reconsidered.
The Next Disclosure Failure May Be a Governance Failure
The SEC’s cybersecurity disclosure framework has made materiality a visible part of enterprise incident response.
But the more consequential governance issue lies beneath the filing requirement.
Can the organization demonstrate that materiality decisions are made through an authorized, informed, timely, and reconstructable process?
A company may submit an accurate disclosure and still discover weaknesses in its internal decision architecture.
Another company may make a reasonable initial determination but fail to recognize when subsequent developments require reassessment.
A third may reach the correct conclusion but lack evidence establishing how the decision was made.
These are different failures.
Yet each exposes a weakness in the relationship between organizational knowledge, decision authority, and accountability.
The solution is not to treat every cybersecurity incident as material.
Nor is it to require boards to approve every technical assessment.
The solution is to establish a governance process that can evaluate evolving facts, identify consequential changes, assign appropriate decision authority, and preserve the evidence supporting each determination.
The organization must be capable of explaining not only its final conclusion, but the path by which it arrived there.
Materiality is not a checkbox.
It is a consequential judgment made within an evolving body of evidence.
And when the evidence changes, the organization must be prepared to determine whether its judgment should change as well.
The Cyber Governance Center Perspective
Cybersecurity materiality governance requires more than a documented assessment and a timely regulatory filing.
Organizations must establish how significant incidents are evaluated, who possesses authority to make materiality determinations, what developments trigger reassessment, and how consequential decisions are preserved.
The Cyber Governance Center’s Defensible Evidence Framework™ and Evidentiary Architecture™ provide a structured approach to connecting incident evidence, business consequences, authorized decisions, disclosure actions, and continuing review.
The objective is not to guarantee that every initial assessment will remain unchanged.
It is to demonstrate that each determination was reasonable in light of the information available, that significant new evidence received appropriate consideration, and that resulting decisions were made through legitimate authority.
The most defensible organization is not necessarily the one whose materiality assessment never changes.
It is the one that can explain precisely why the assessment changed, when the relevant information became known, who authorized the revised conclusion, and what happened afterward.
Clarity. Accountability. Defensibility.
Sources and Further Reading
U.S. Securities and Exchange Commission — August 2023
Cybersecurity Risk Management, Strategy, Governance, and Incident Disclosure.
The SEC’s compliance guide explains Item 1.05, the traditional securities-law materiality standard, the requirement to make determinations without unreasonable delay, and the four-business-day disclosure deadline.
U.S. Securities and Exchange Commission — July 26, 2023
SEC Adopts Rules on Cybersecurity Risk Management, Strategy, Governance, and Incident Disclosure by Public Companies.
Official announcement describing the cybersecurity disclosure requirements and related governance disclosures.
SEC Division of Corporation Finance — May 21, 2024
Disclosure of Cybersecurity Incidents Determined To Be Material and Other Cybersecurity Incidents.
Staff guidance distinguishing required Item 1.05 disclosures from voluntary reporting of incidents not determined to be material.
SEC Division of Corporation Finance — June 24, 2024
Exchange Act Form 8-K: Compliance and Disclosure Interpretations.
Interpretive guidance addressing ransomware payments, insurance recovery, quantitative and qualitative materiality considerations, and related cybersecurity incidents.
iRhythm Holdings — June 15, 2026
Form 8-K, Item 1.05: Material Cybersecurity Incidents.
Primary-source example of a materiality determination involving third-party-hosted applications, confirmed data exfiltration, and an ongoing investigation.
Cybersecurity and Infrastructure Security Agency — July 29, 2026
2026 Minimum Elements for a Software Bill of Materials.
Background on structured software dependency information and its use in cybersecurity risk assessment. An SBOM is distinct from the proposed Control Bill of Materials concept discussed in this article.