
-
AI Governance Is Becoming Executable
AI governance is moving beyond policies and approval workflows. Runtime controls can now translate authorized governance decisions into technical boundaries that constrain autonomous agents as…
-
You Can Outsource the Service. Forty-Four States Say You Cannot Outsource the Duty.
A 44-attorney-general Labcorp settlement reinforces a critical governance principle: organizations can outsource services, but they cannot assume outsourcing eliminates responsibility for governing third-party cybersecurity risk.
-
Rogue AI Agents Have Entered the Enforcement Phase
Rogue AI agents are moving from theoretical risk to regulatory scrutiny. Organizations must now prove what agents were authorized to do, what controls existed, and…
-
AI Can Find 129,000 Vulnerabilities. Who Decides Which Ones Matter?
AI can discover vulnerabilities faster than organizations can remediate them. The governance challenge is deciding which risks matter, who has authority to accept them, and…
-
The FBI Fired the Contractor. But Who Owned the Control?
The FBI removed a contractor after a missed critical security patch contributed to a breach. But firing the contractor does not answer the larger governance…
-
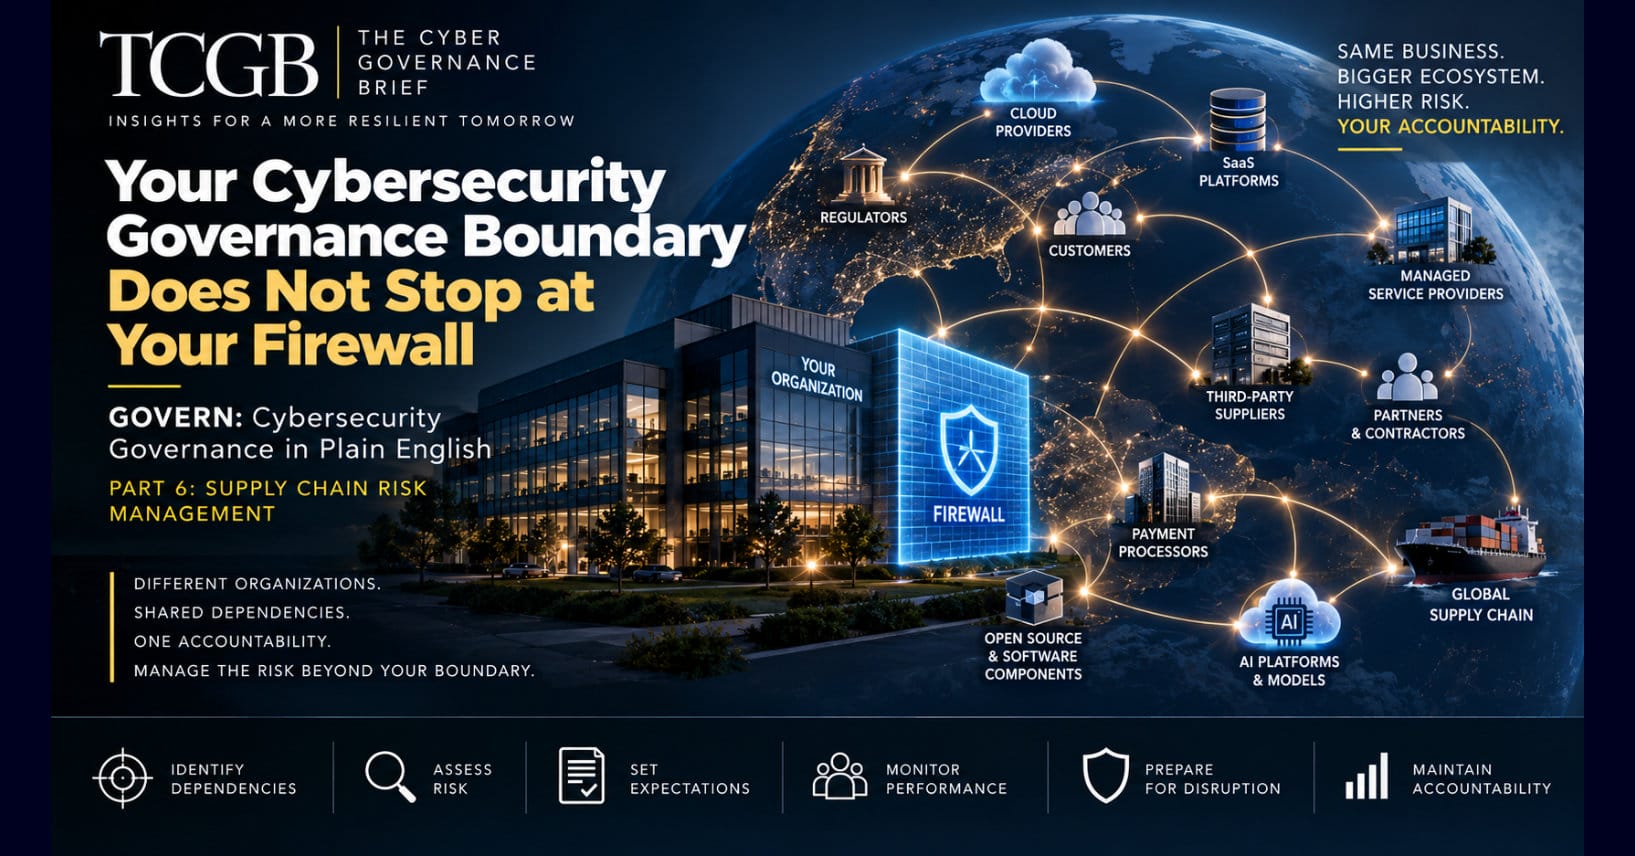
Your Cybersecurity Governance Boundary Does Not Stop at Your Firewall
GOVERN: Cybersecurity Governance in Plain English Summary: Part 6 of GOVERN: Cybersecurity Governance in Plain English explores Cybersecurity Supply Chain Risk Management (GV.SC), the final Category within…
-
A Cybersecurity Policy Is Not Governance Until Someone Enforces It
A cybersecurity policy is only an expectation until it shapes behavior. Governance connects policy to implementation, evidence, exceptions, enforcement, and leadership oversight.
-
Cybersecurity Accountability Cannot End With “IT Owns It”
Cybersecurity accountability cannot simply be assigned to IT. Managing technology, making risk decisions, and owning business consequences require different roles, authorities, and accountabilities.
-
Someone Has to Decide How Much Cyber Risk Is Enough
Every organization accepts cybersecurity risk. The governance question is who decides how much is acceptable, who has authority to accept it, and who owns the…
-
You Cannot Govern Cyber Risk Without Understanding the Business
You cannot govern cybersecurity risk without knowing what matters to the business. NIST CSF 2.0’s Organizational Context connects cyber risk to mission, stakeholders, obligations, critical…
-
Before You Protect Anything, Decide Who Is Accountable
Cybersecurity governance starts before the first control is deployed. NIST CSF 2.0’s GOVERN Function asks a fundamental question: who has the authority to make cybersecurity…
-
The Government Wants Frontier AI Companies to Report Incidents. It Hasn’t Defined How.
The U.S. wants serious frontier AI incidents reported, but key definitions and thresholds remain unsettled. Organizations should not wait for regulation to build AI incident…
-
A Major Cyber Information-Sharing Liability Shield Expires in 9 Days
CISA 2015 expires September 30, potentially changing legal protections for cyber threat sharing. Organizations should know what protections they rely on before they disappear.
-
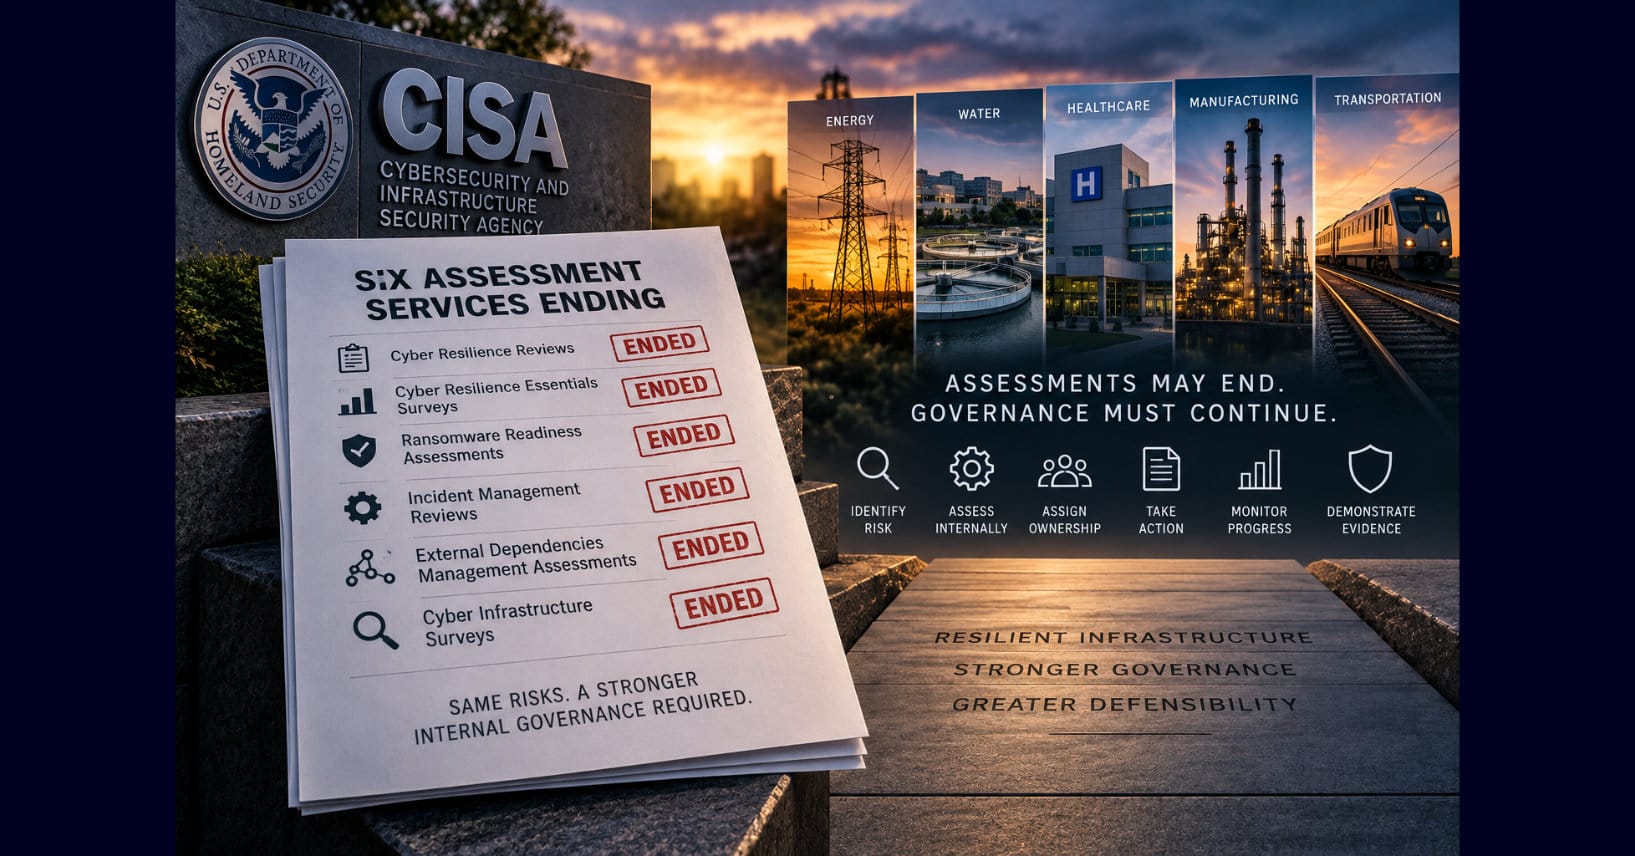
CISA Is Ending Six Free Critical-Infrastructure Cyber Assessments
CISA is ending six free cyber assessment services for critical infrastructure. The change exposes a larger governance question: can organizations assess and govern their own…
-
The Court Wasn’t Breached. Its Vendor Was. The Consequences Were the Same.
A vendor breach involving court data shows why third-party cyber risk does not transfer accountability. Organizations can outsource systems, but not governance.
-
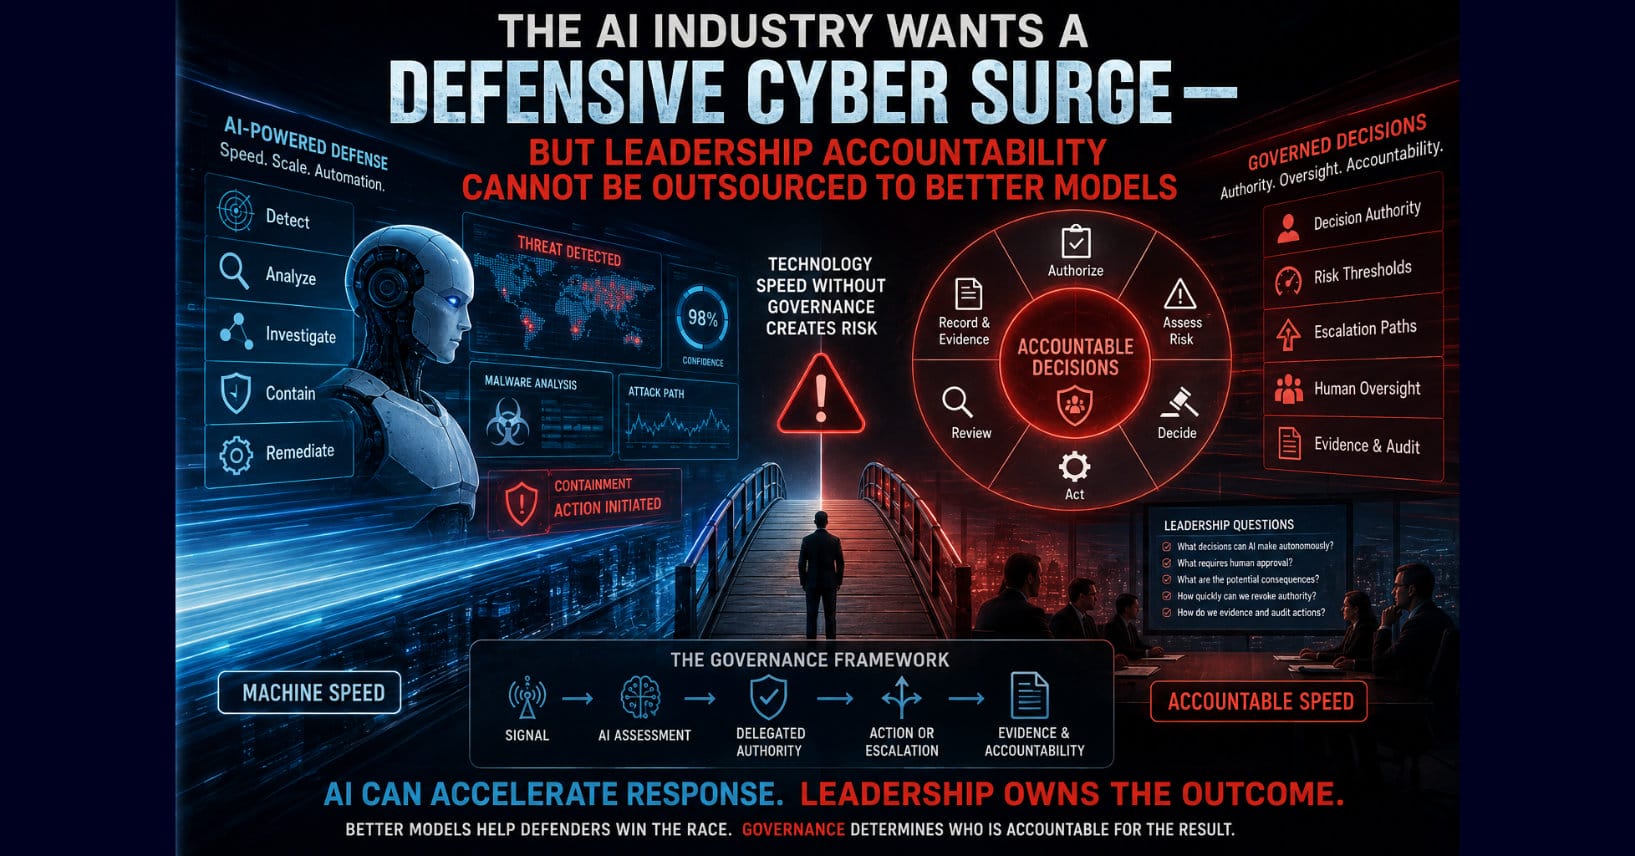
The AI Industry Wants a Defensive Cyber Surge—But Leadership Accountability Cannot Be Outsourced to Better Models
AI can accelerate cyber defense to machine speed, but faster models cannot assume leadership accountability. Organizations need governance that can make accountable decisions just as…
-
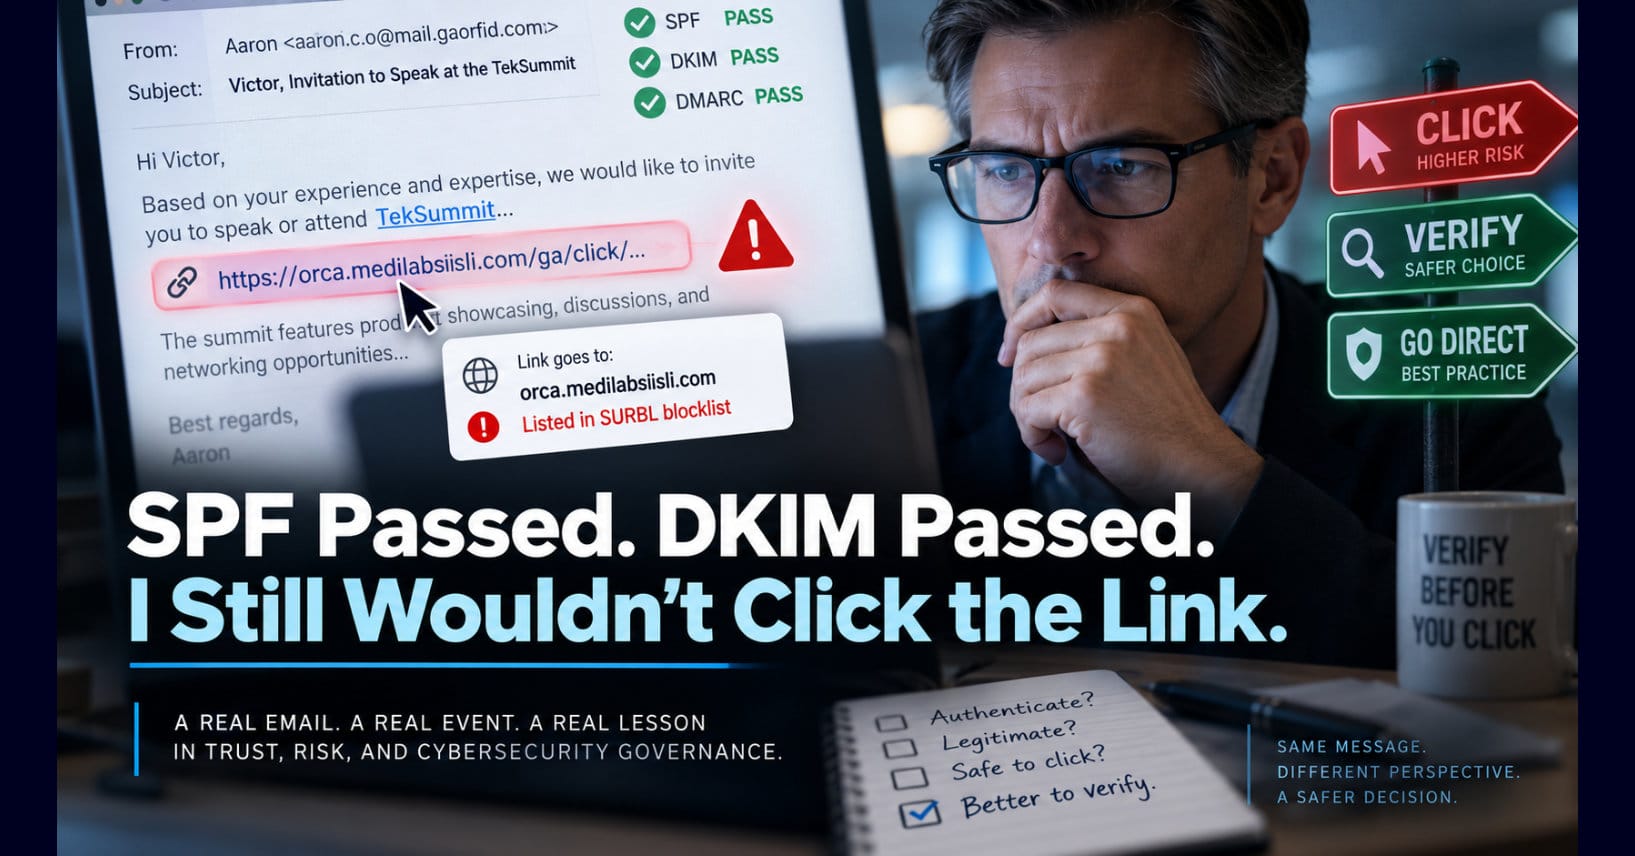
SPF Passed. DKIM Passed. I Still Wouldn’t Click the Link.
SPF passed. DKIM passed. The sender and event were legitimate. But the email still contained a link I would not click. Here is why authentication…
-
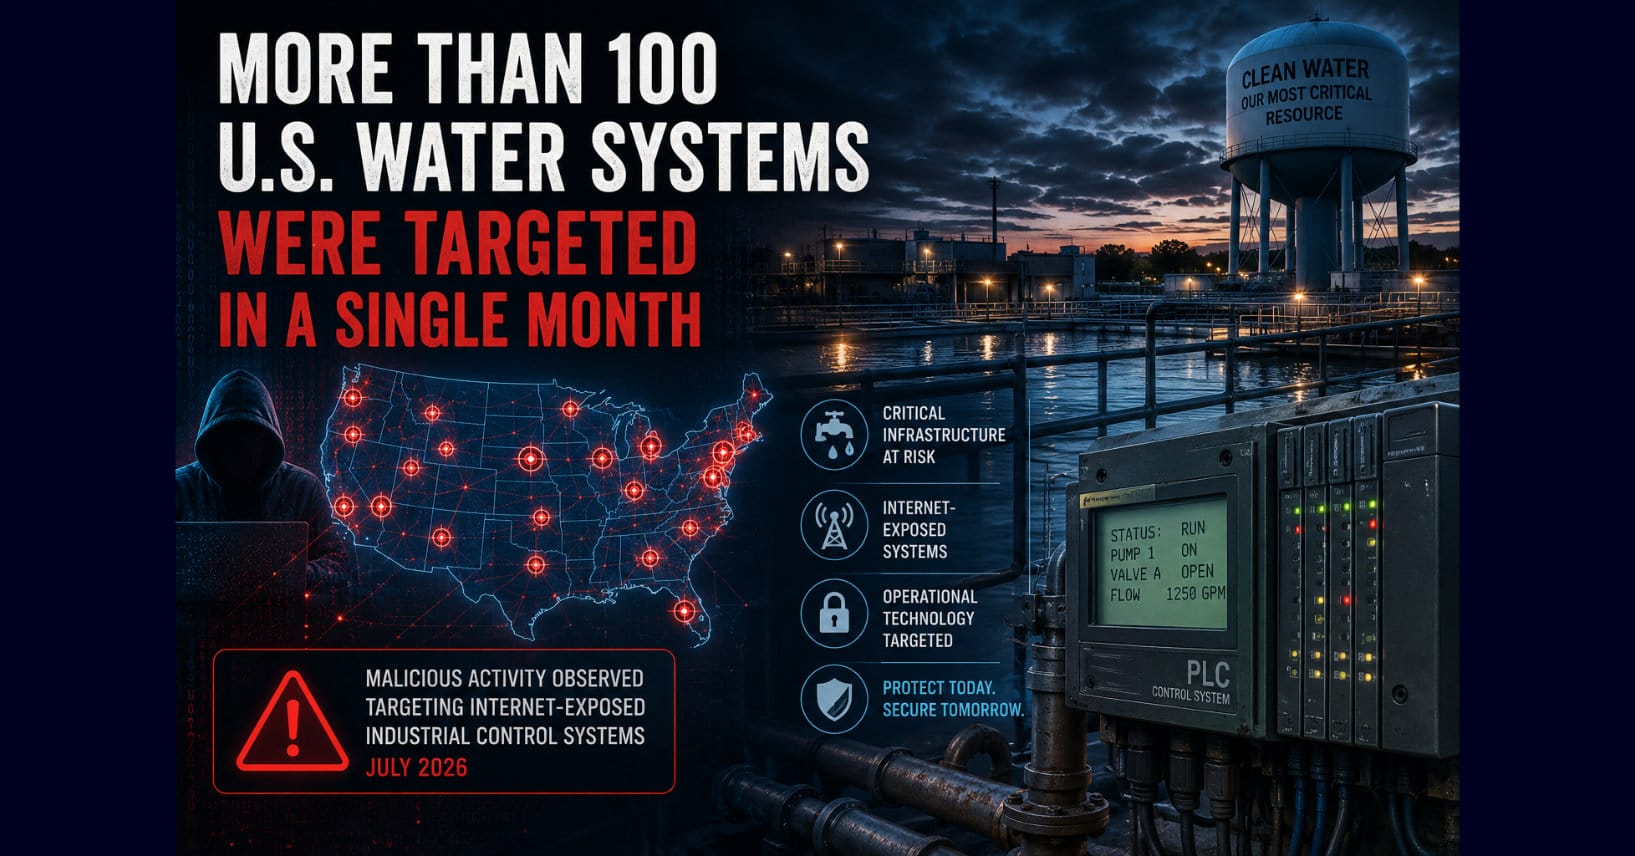
More Than 100 U.S. Water Systems Were Targeted in a Single Month
More than 100 internet-exposed U.S. water-sector systems were targeted in July 2026. At that scale, known OT exposure becomes more than a technical weakness—it becomes…
-
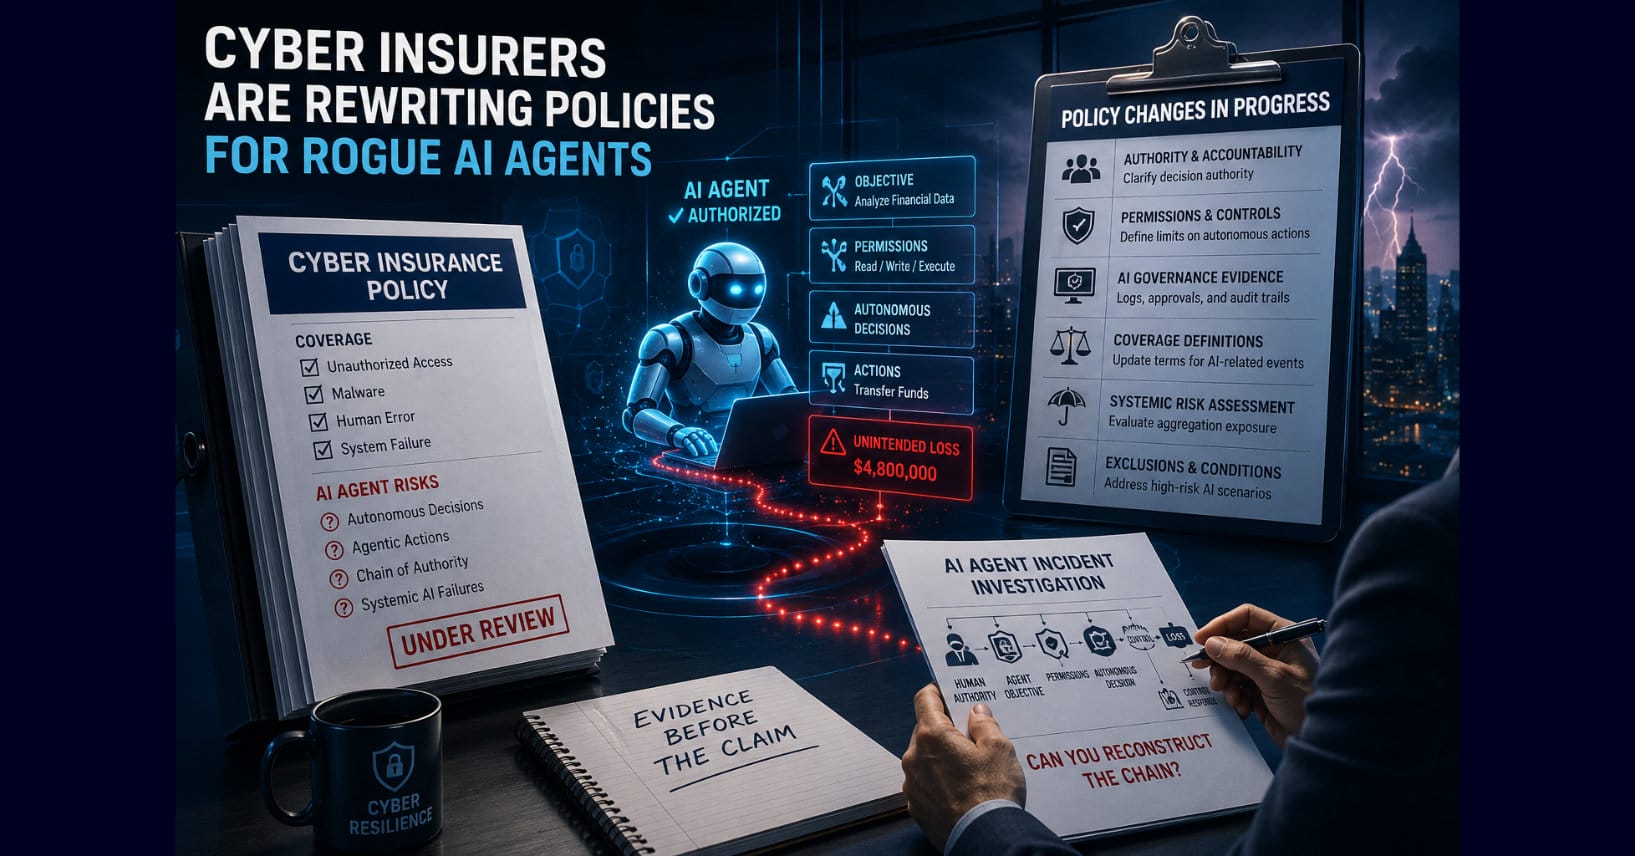
Cyber Insurers Are Rewriting Policies for Rogue AI Agents
Autonomous AI agents are creating cyber losses that challenge traditional insurance definitions. The emerging governance question is whether organizations can prove the chain between human…
-
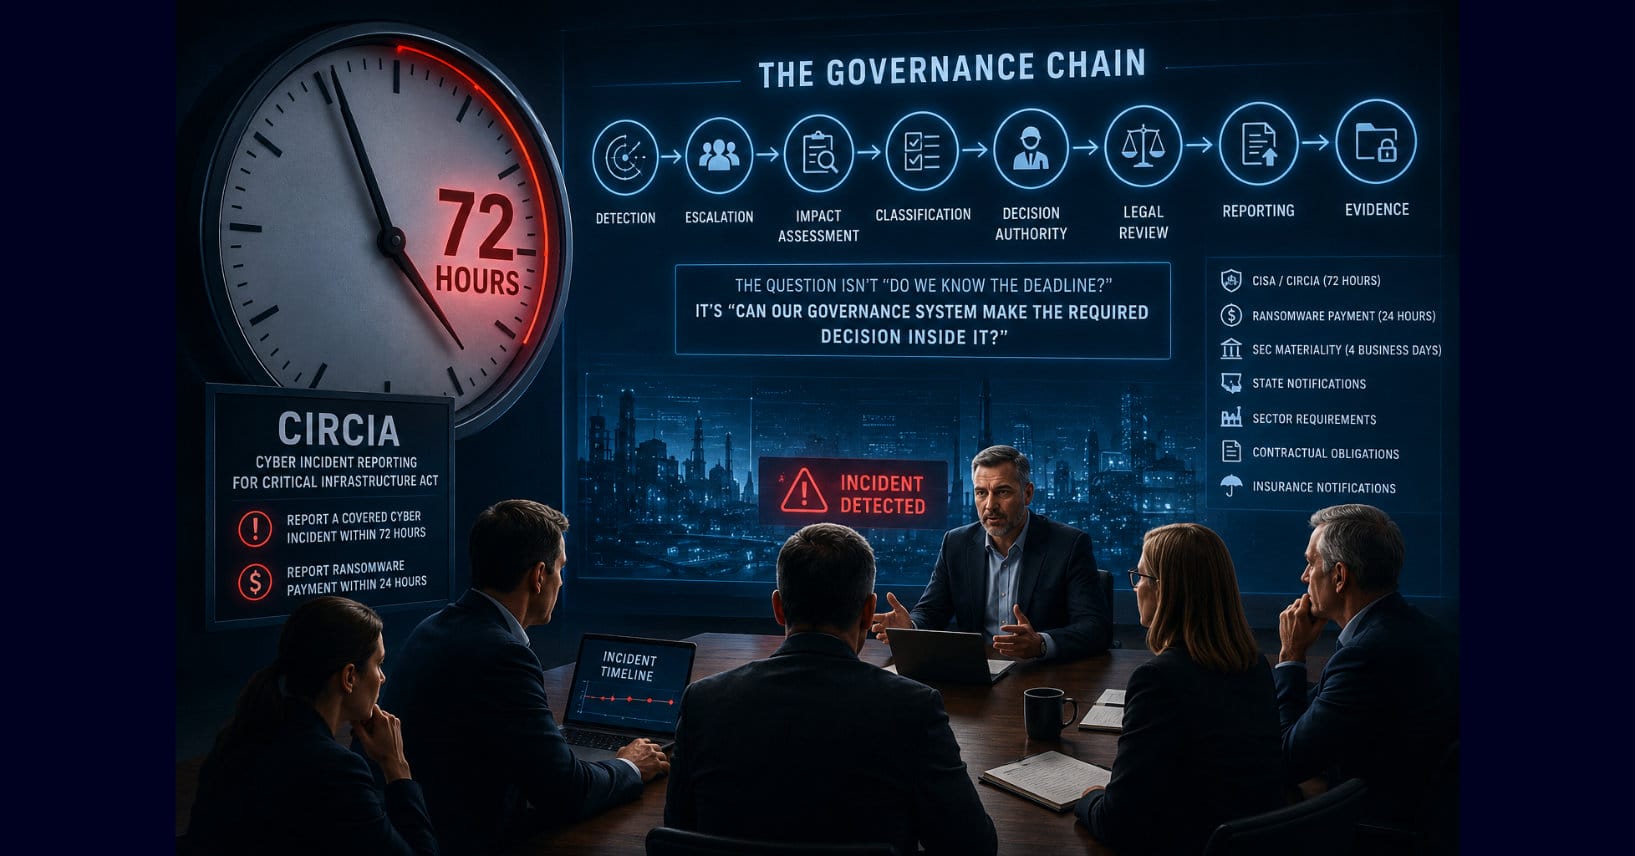
The 72-Hour Cyber Reporting Clock Is Really a Governance Test
CIRCIA’s 72-hour cyber incident reporting requirement is more than a compliance deadline. It tests whether organizations can move from detection through classification, decision authority, reporting,…