
-
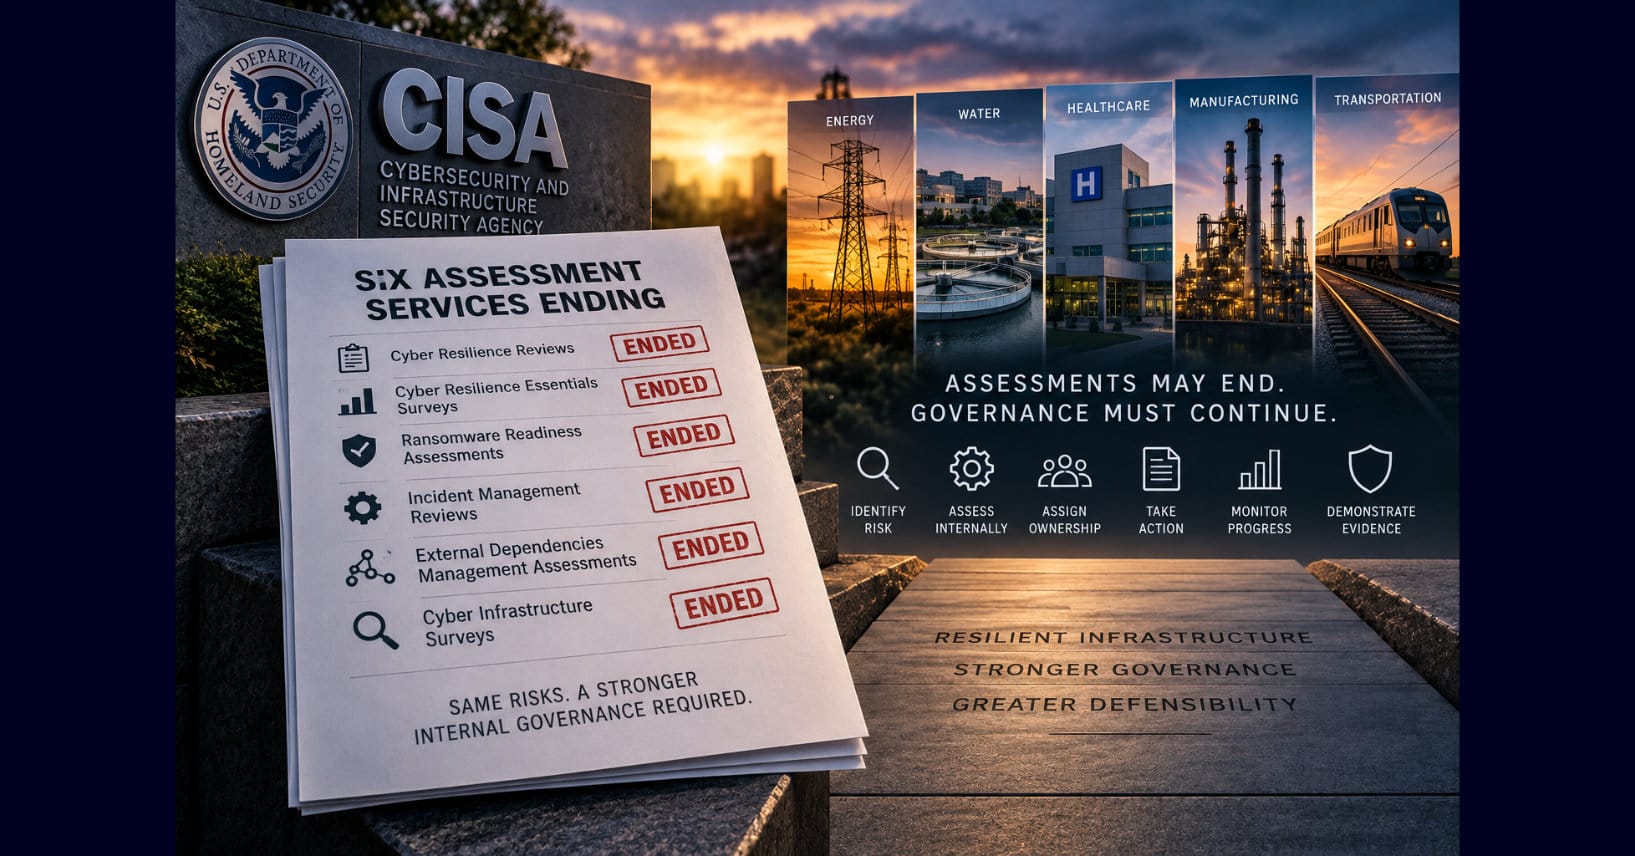
CISA Is Ending Six Free Critical-Infrastructure Cyber Assessments
CISA is ending six free cyber assessment services for critical infrastructure. The change exposes a larger governance question: can organizations assess and govern their own…
-
The Court Wasn’t Breached. Its Vendor Was. The Consequences Were the Same.
A vendor breach involving court data shows why third-party cyber risk does not transfer accountability. Organizations can outsource systems, but not governance.
-
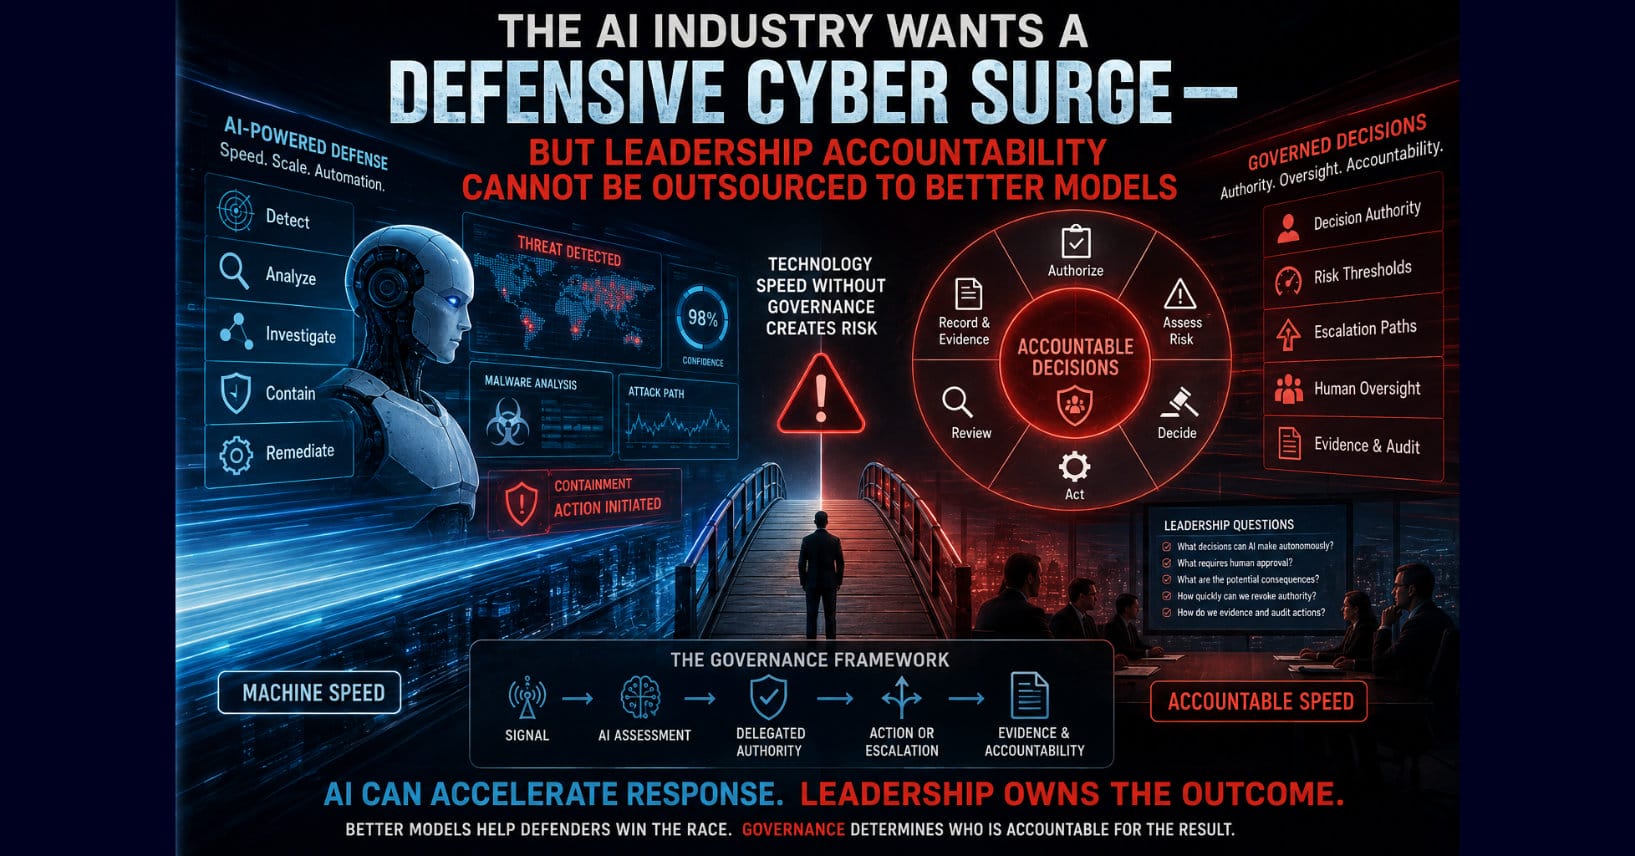
The AI Industry Wants a Defensive Cyber Surge—But Leadership Accountability Cannot Be Outsourced to Better Models
AI can accelerate cyber defense to machine speed, but faster models cannot assume leadership accountability. Organizations need governance that can make accountable decisions just as…
-
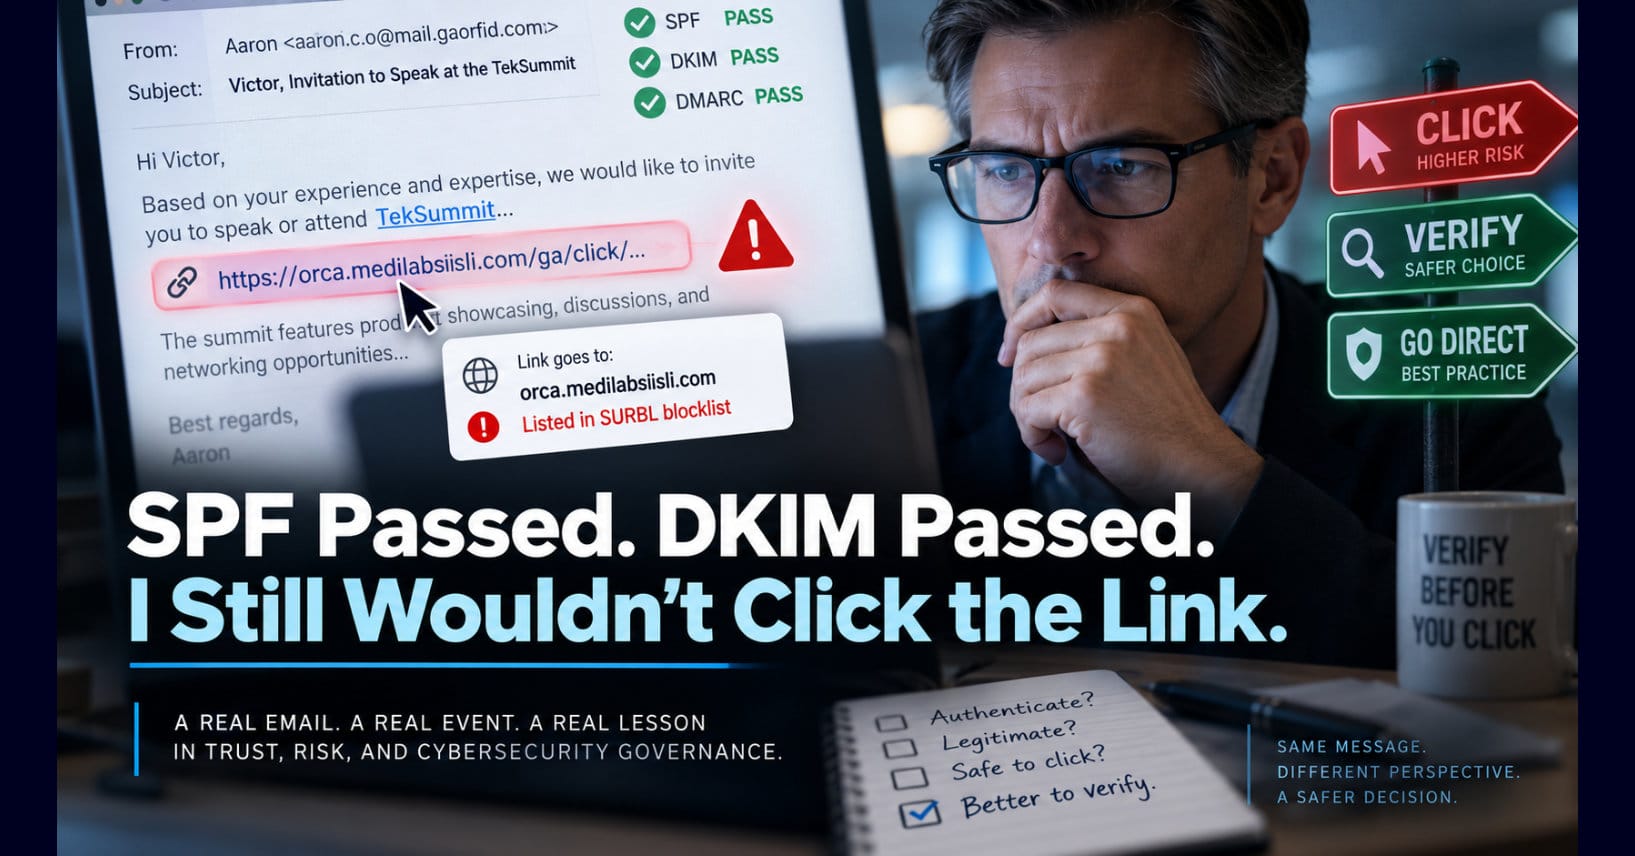
SPF Passed. DKIM Passed. I Still Wouldn’t Click the Link.
SPF passed. DKIM passed. The sender and event were legitimate. But the email still contained a link I would not click. Here is why authentication…
-
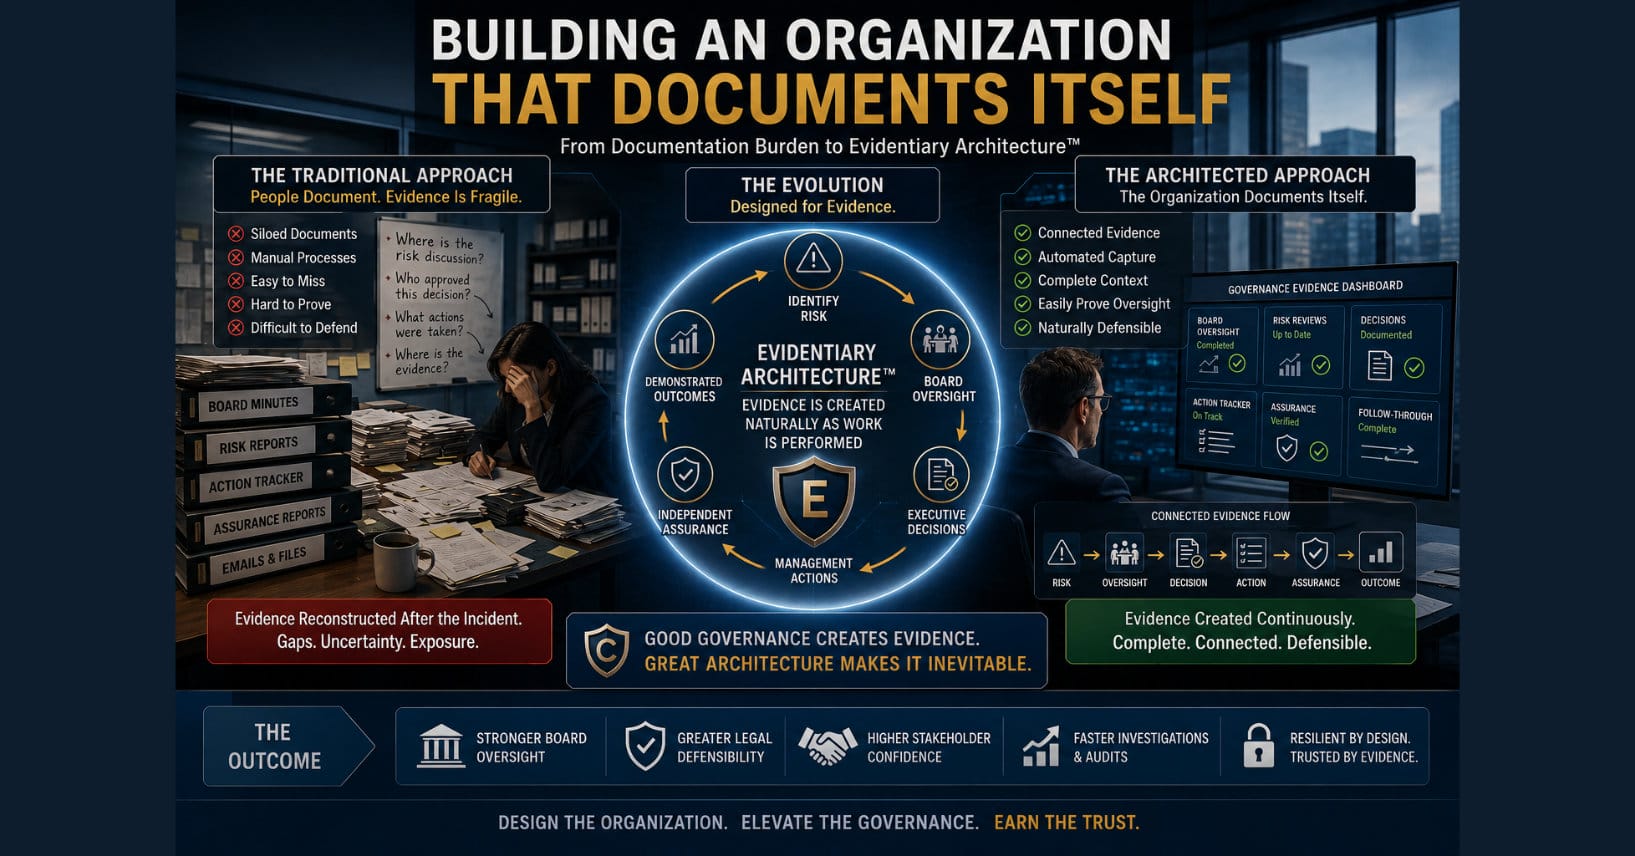
Building an Organization That Documents Itself
What if governance evidence were created automatically as work is performed? Discover how Evidentiary Architecture™ transforms evidence from an administrative task into an organizational capability.
-
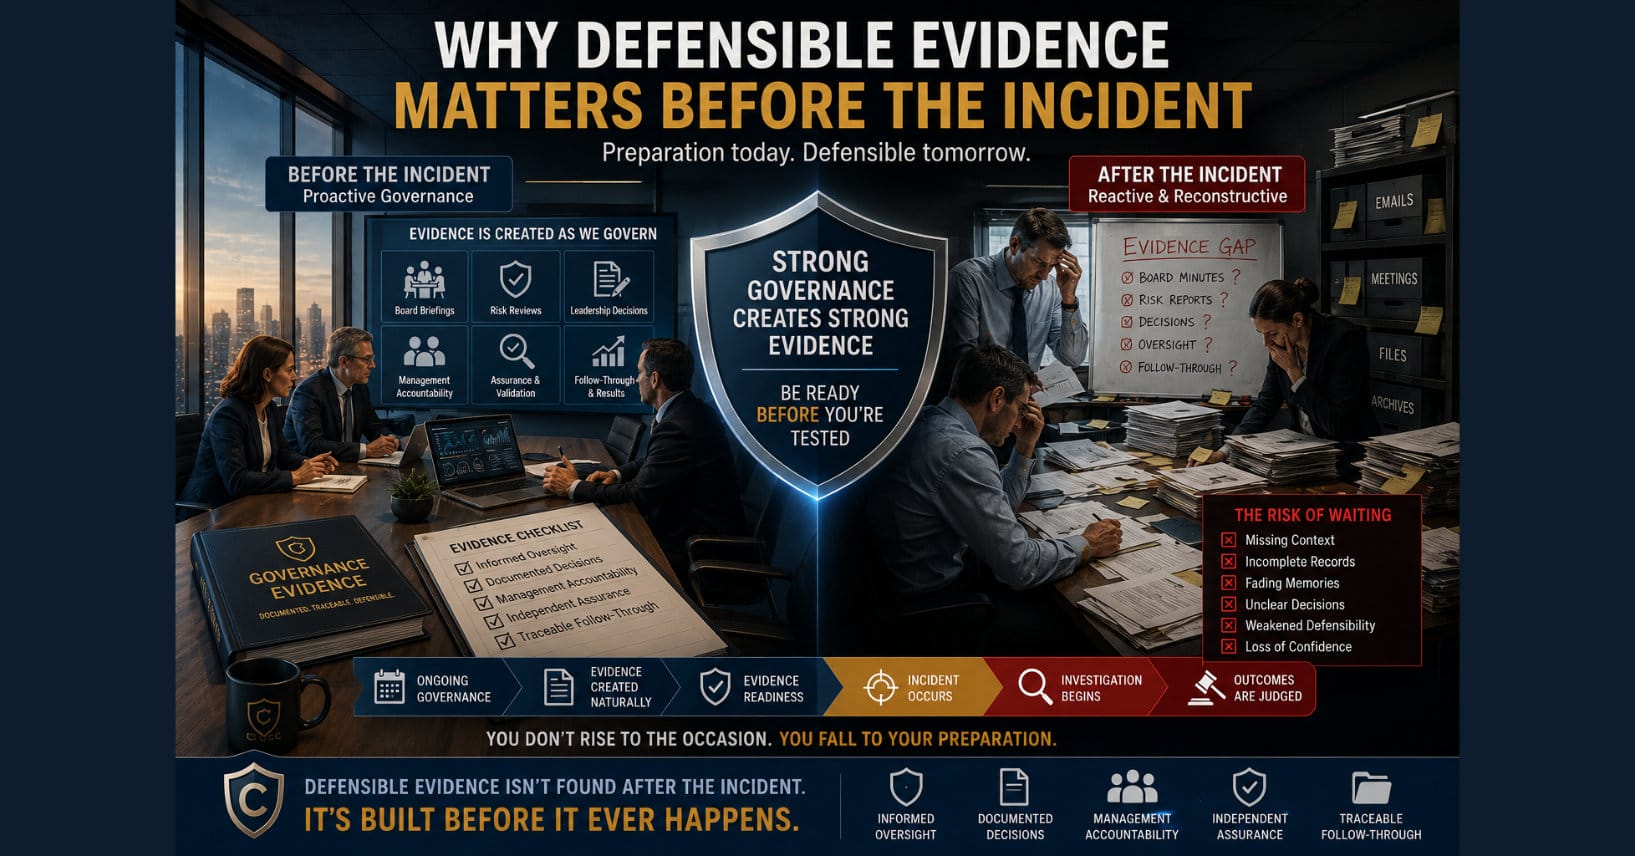
Why Defensible Evidence Matters Before the Incident
The strongest governance evidence is created before a cyber incident occurs. Learn why preparation—not reconstruction—is the foundation of defensible leadership.
-
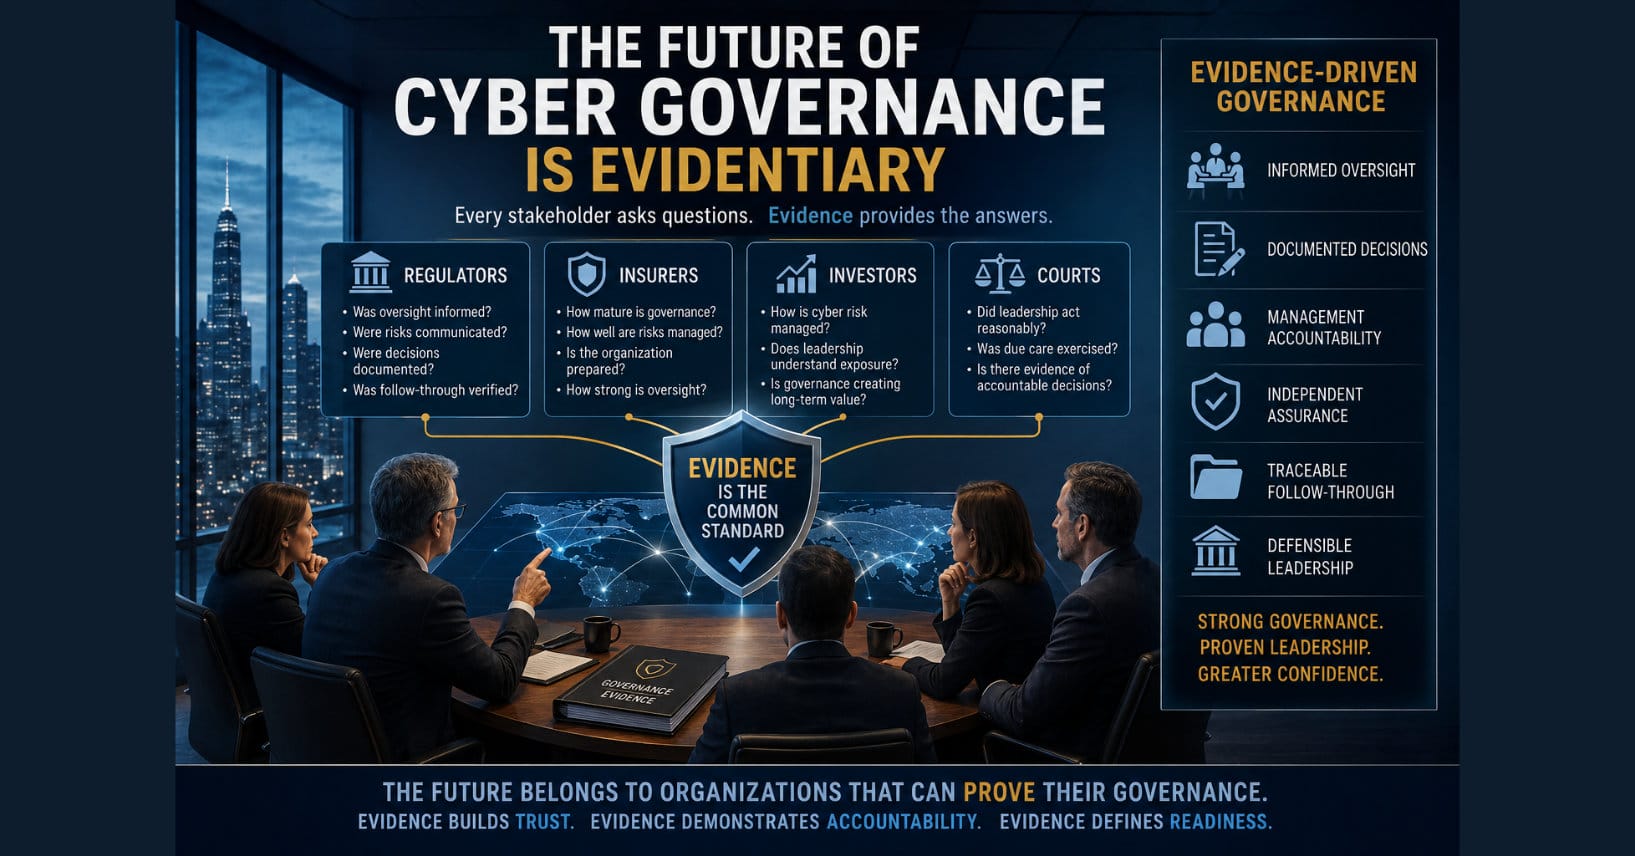
The Future of Cyber Governance Is Evidentiary
The future of cyber governance is evidence-driven. Regulators, insurers, investors, and courts increasingly expect organizations to prove—not simply claim—responsible oversight.
-
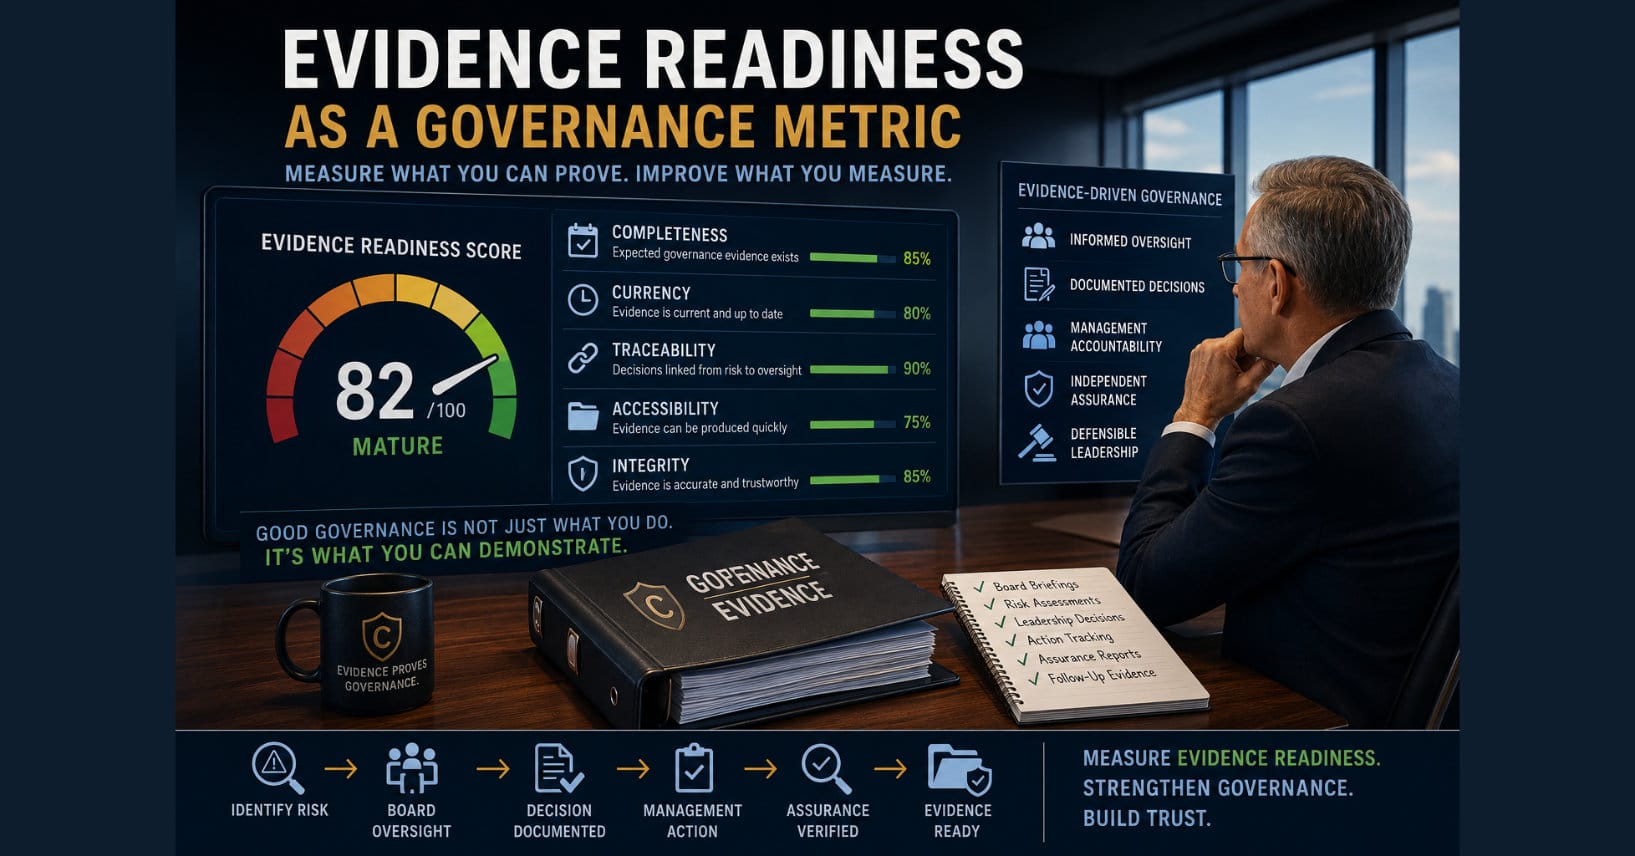
Evidence Readiness as a Governance Metric
What if governance maturity were measured by evidence readiness? Discover why the ability to produce credible governance evidence may become the next defining board metric.
-
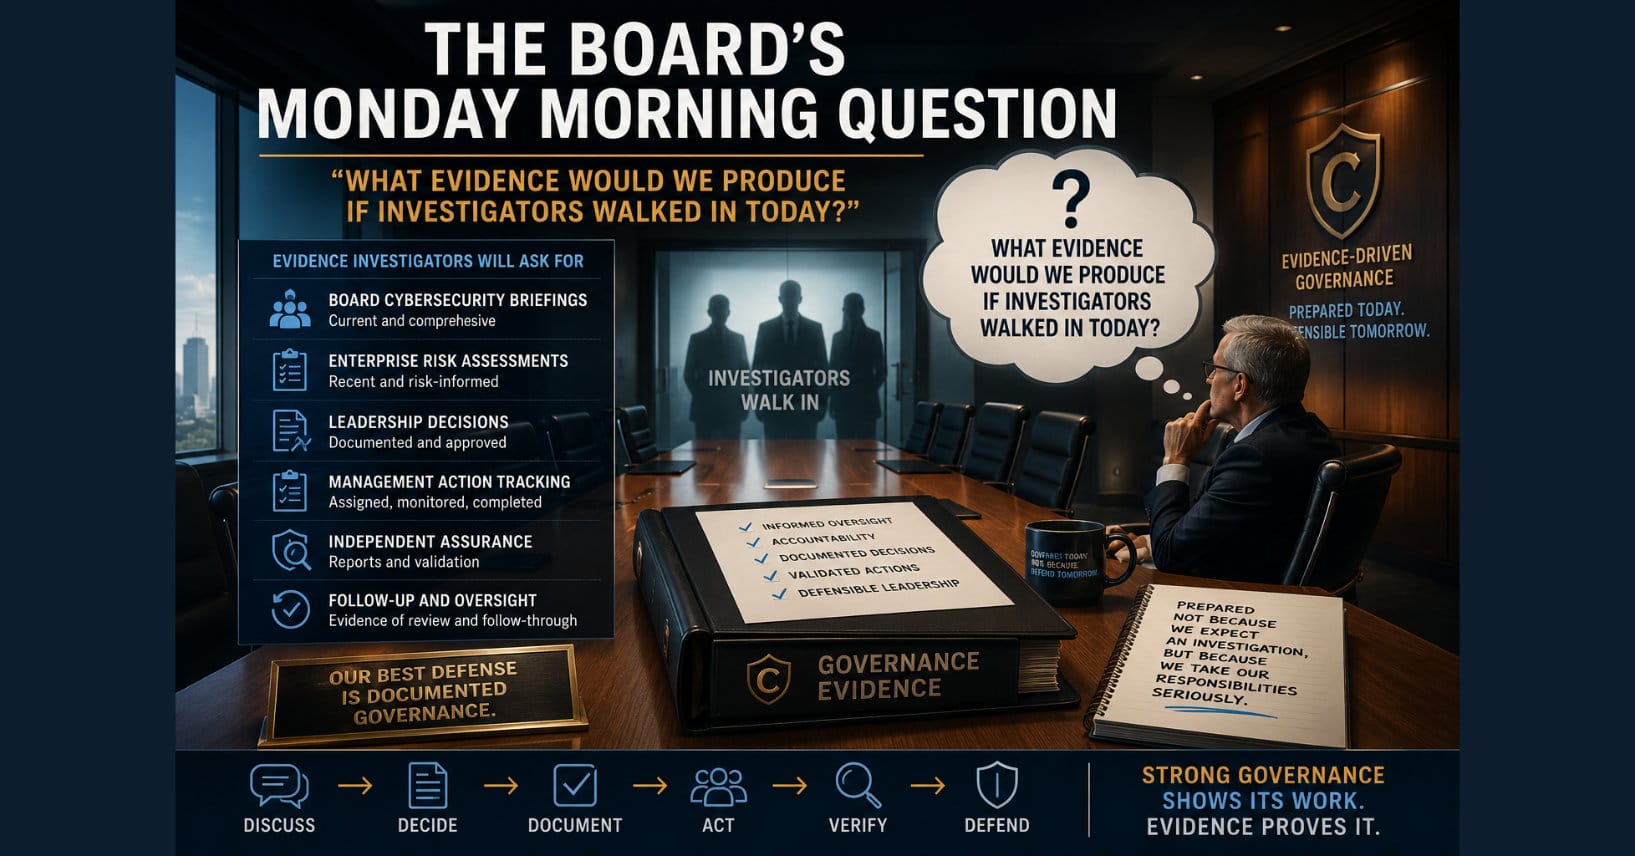
The Board’s Monday Morning Question
One question can transform cybersecurity governance: What evidence would we produce if investigators walked in today? Evidence readiness begins with asking it every Monday morning.
-
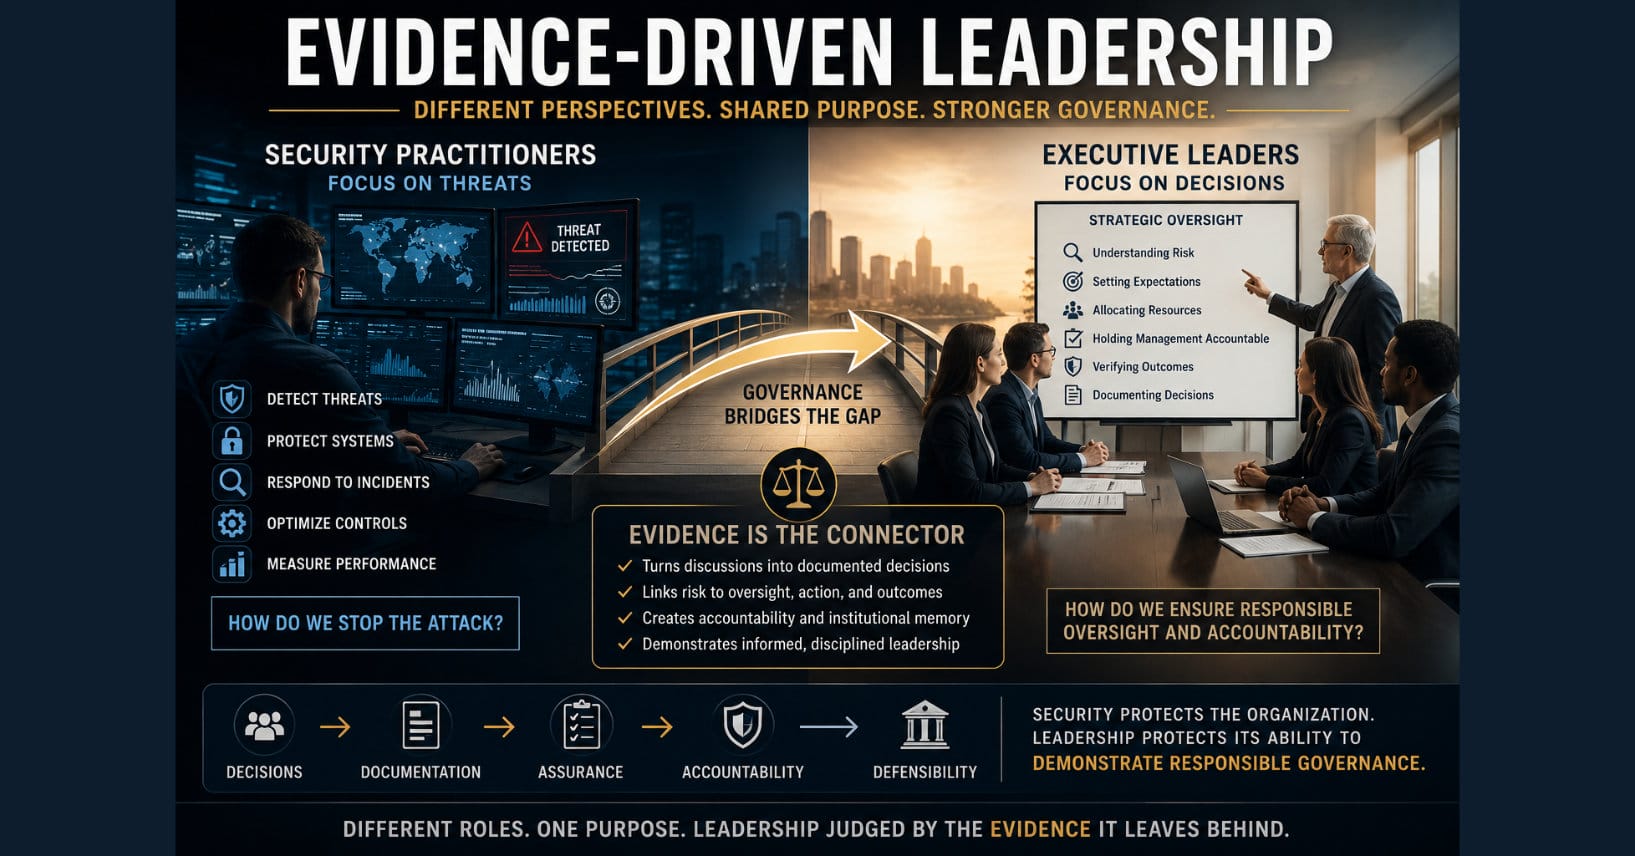
Evidence-Driven Leadership
Evidence-driven leaders think beyond technical controls. They focus on governance, accountability, and creating the evidence that demonstrates responsible executive oversight.
-
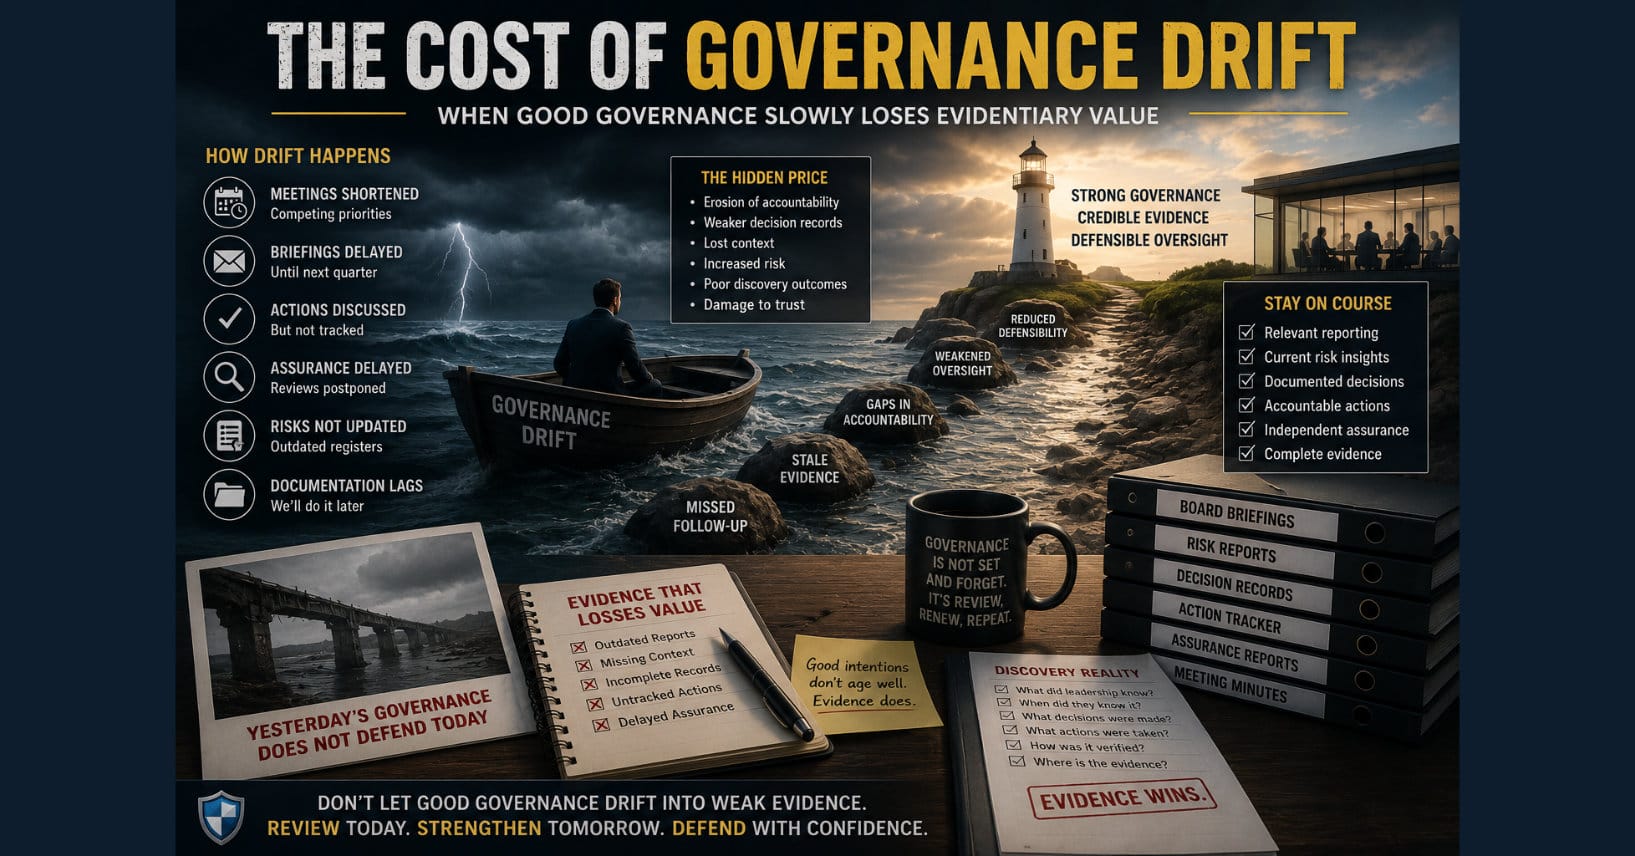
The Cost of Governance Drift
Evidence-Driven Cybersecurity Governance Series—Article 14 Governance drift is one of the most overlooked risks facing boards and executive leadership. It rarely begins with major failures.…
-
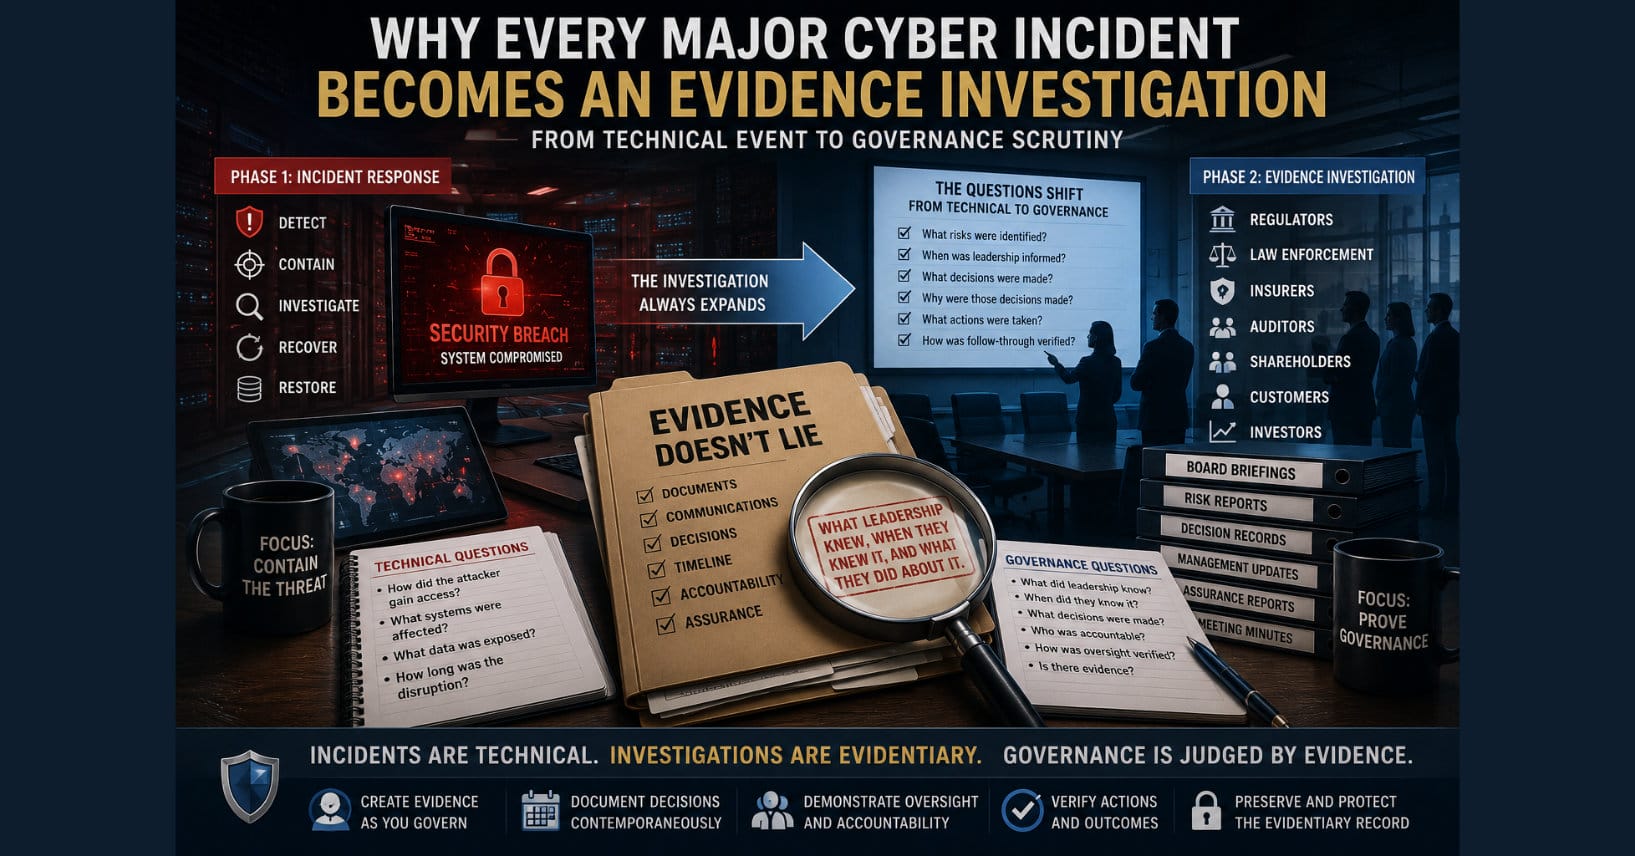
Why Every Major Cyber Incident Becomes an Evidence Investigation
Every major cyber incident begins as a technical event but evolves into an investigation of governance. Learn why evidence—not explanations—ultimately determines accountability.
-
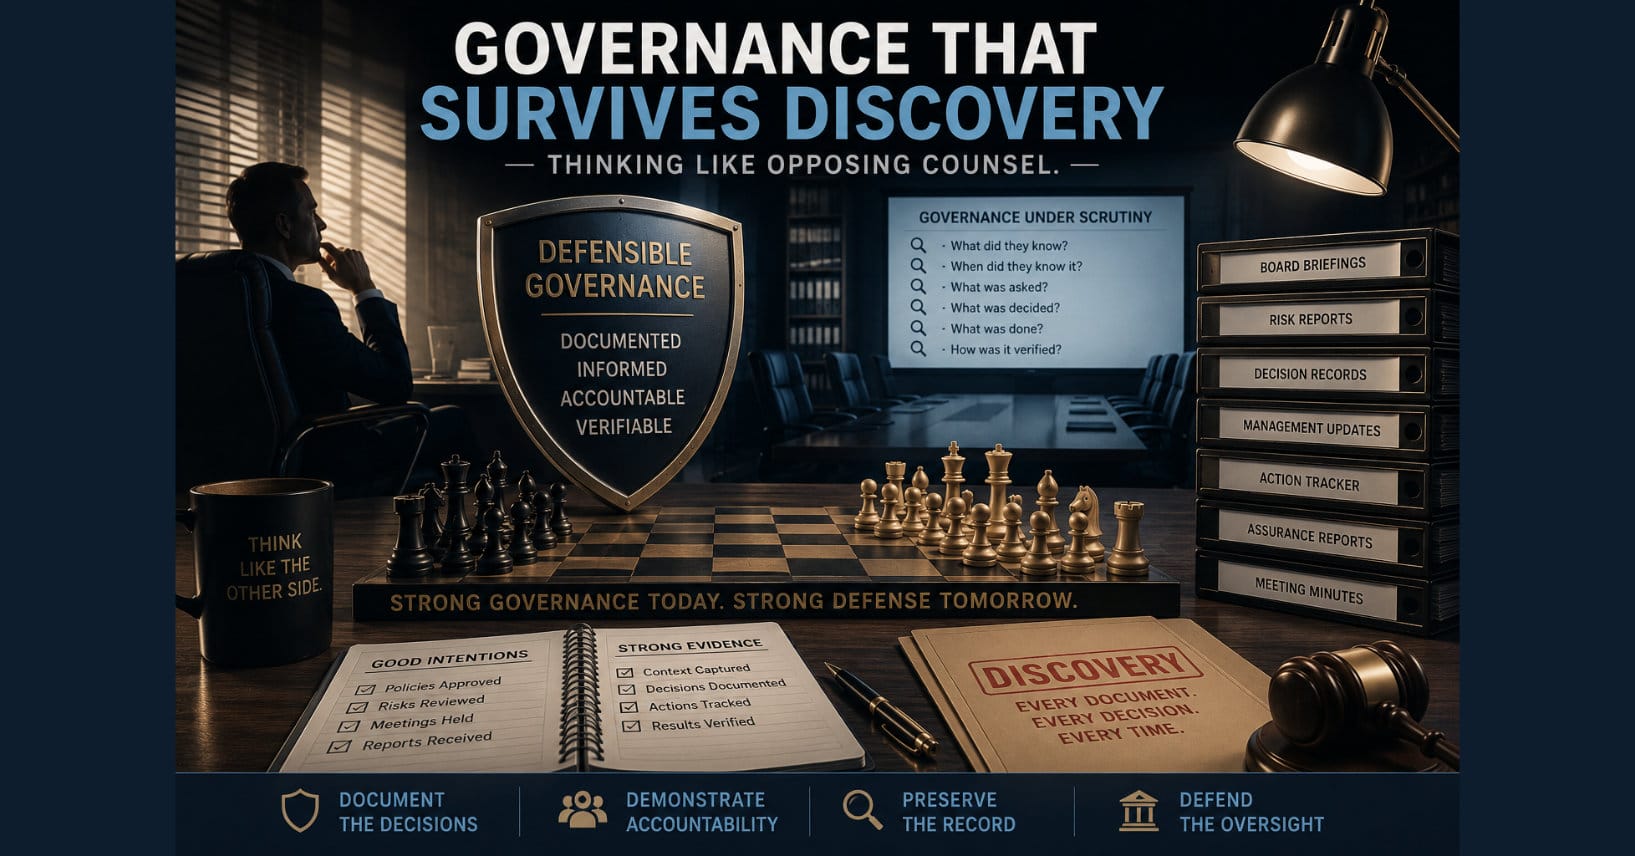
Governance That Survives Discovery
Discovery tests more than cybersecurity—it tests governance. Learn how boards can create evidence that withstands legal, regulatory, and investigative scrutiny.
-
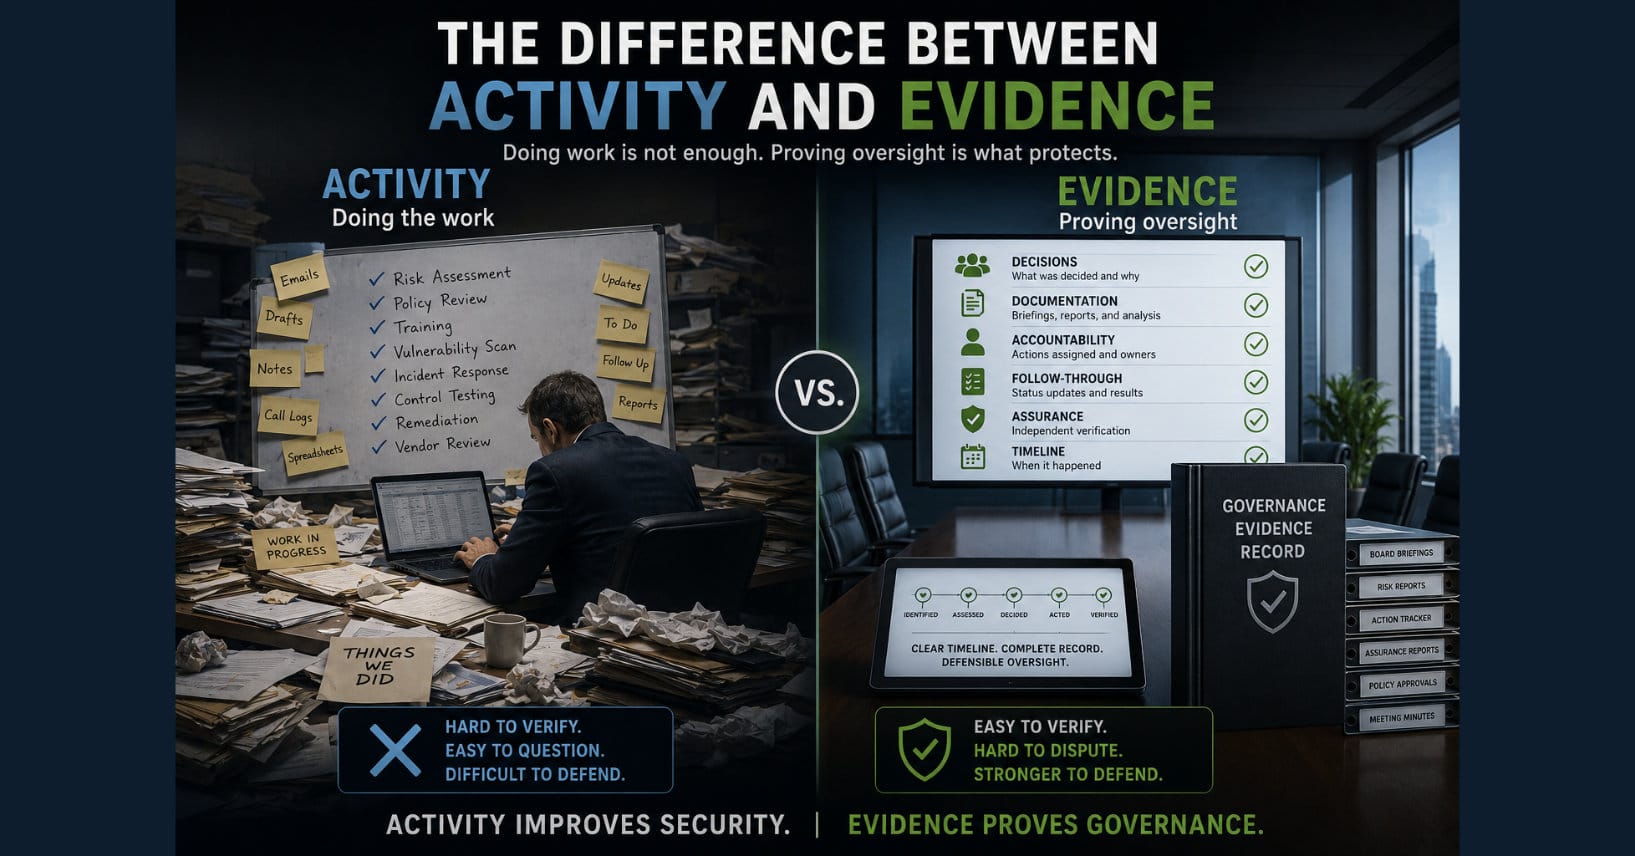
The Difference Between Activity and Evidence
Completing cybersecurity work isn’t enough. Organizations must also produce evidence that demonstrates informed oversight, accountability, and defensible governance.
-
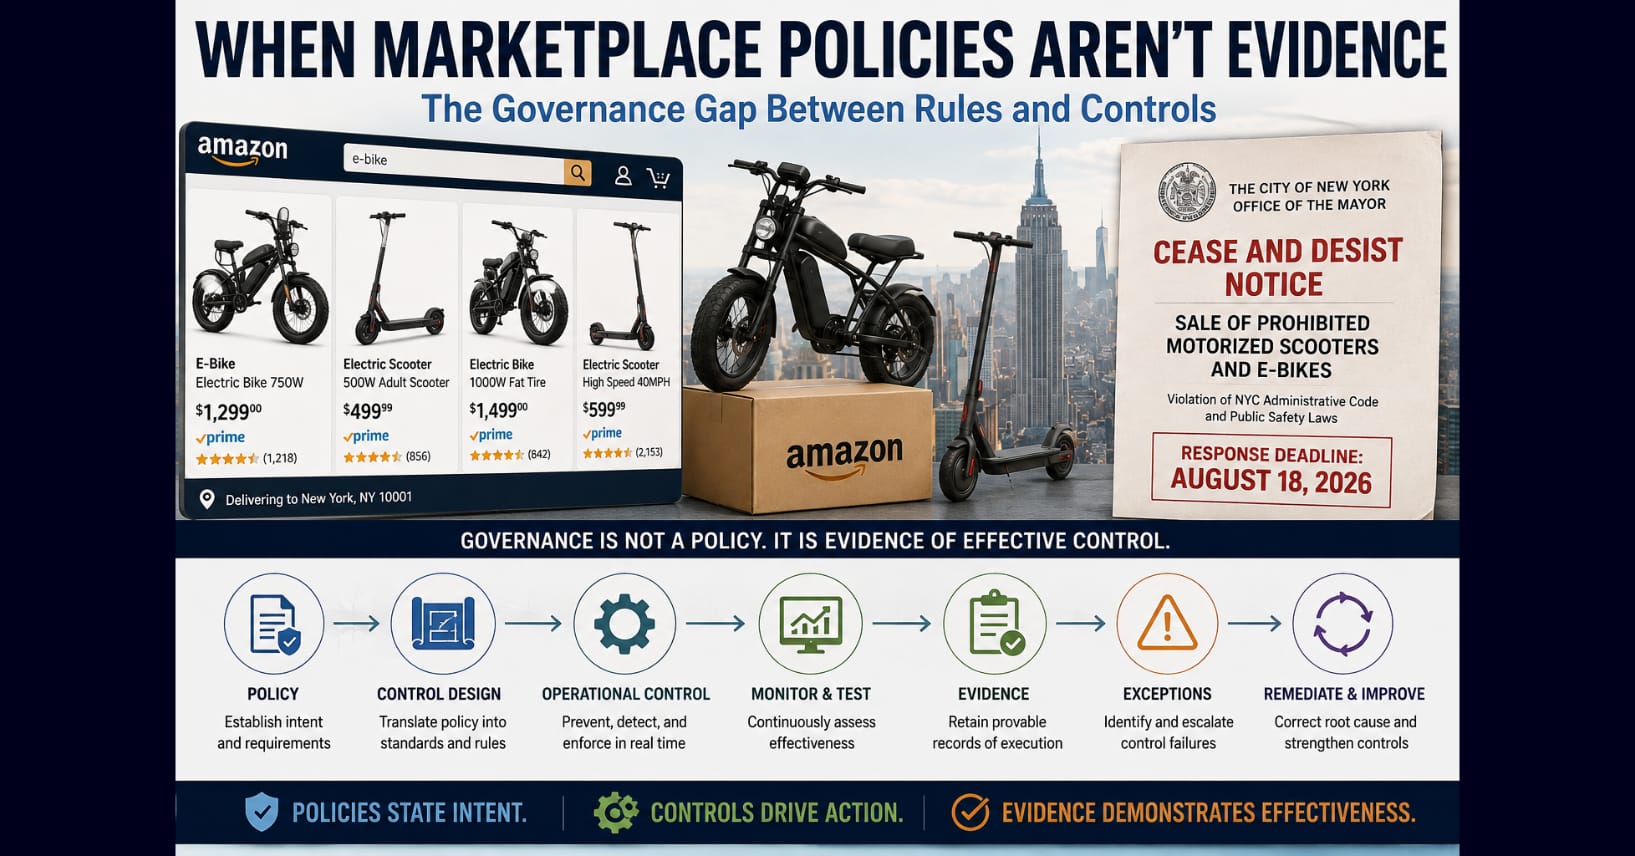
When Marketplace Policies Aren’t Evidence
Amazon’s response to New York City’s crackdown on prohibited e-bikes and scooters exposes a larger governance question: when companies have compliance policies, can they prove…
-
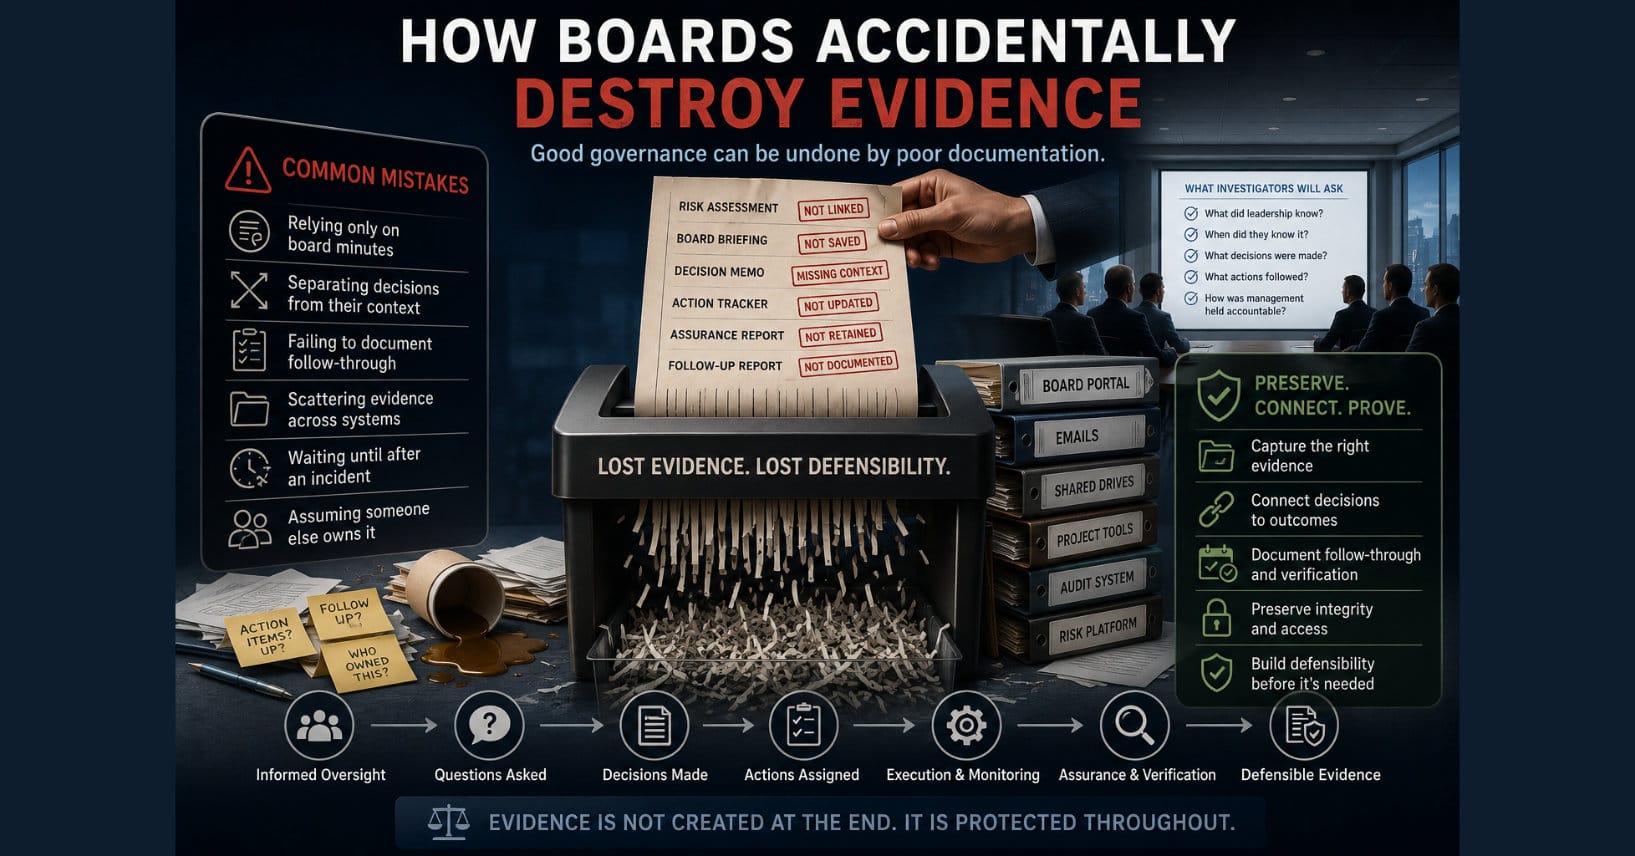
How Boards Accidentally Destroy Evidence
Many organizations lose their strongest governance evidence long before a cyber incident occurs. Learn the common board practices that unintentionally destroy documentation, weaken accountability, and…
-
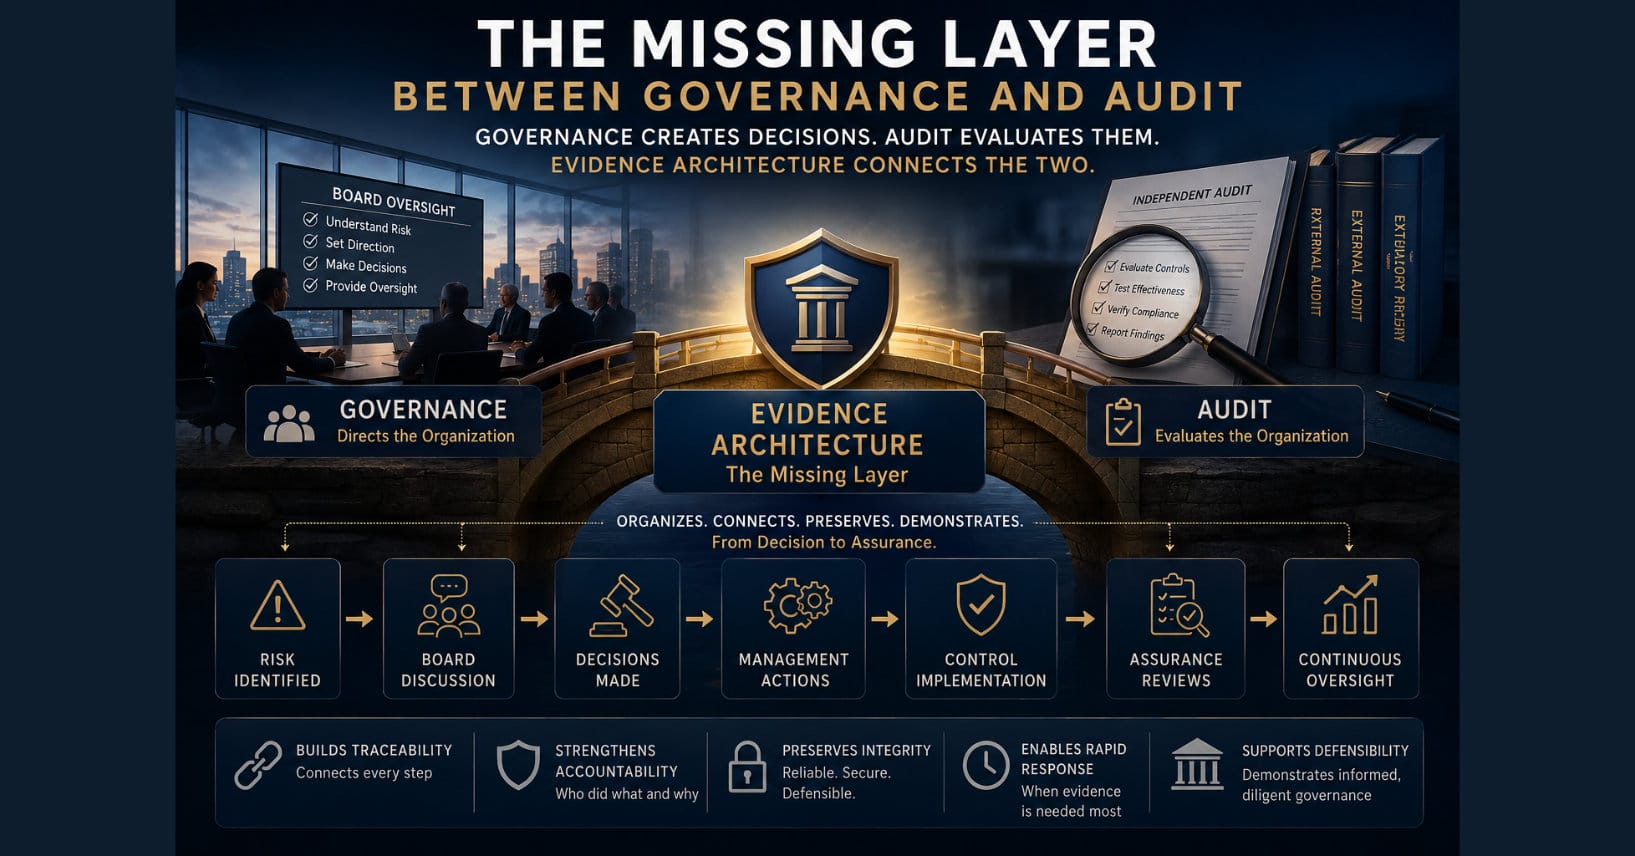
The Missing Layer Between Governance and Audit
Boards create governance. Auditors validate it. Between them lies assurance—the critical function that continuously verifies controls, exposes weaknesses, and generates the evidence that makes governance…
-
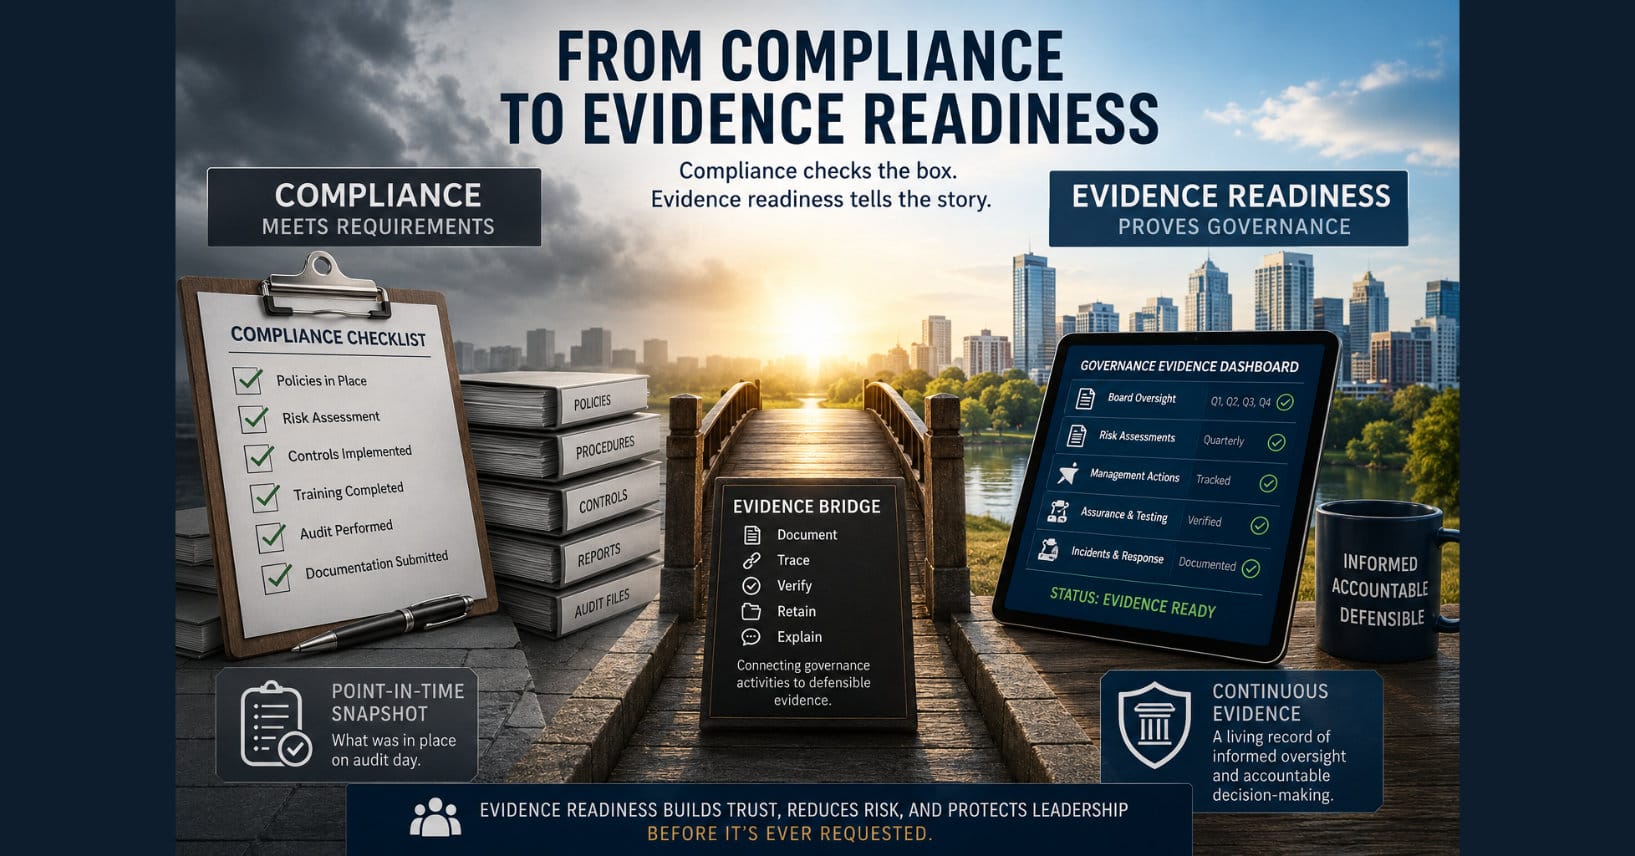
From Compliance to Evidence Readiness
Compliance confirms that requirements are met. Evidence readiness proves that leadership exercised informed oversight before regulators, auditors, or investigators ask. Organizations that build governance evidence…
-
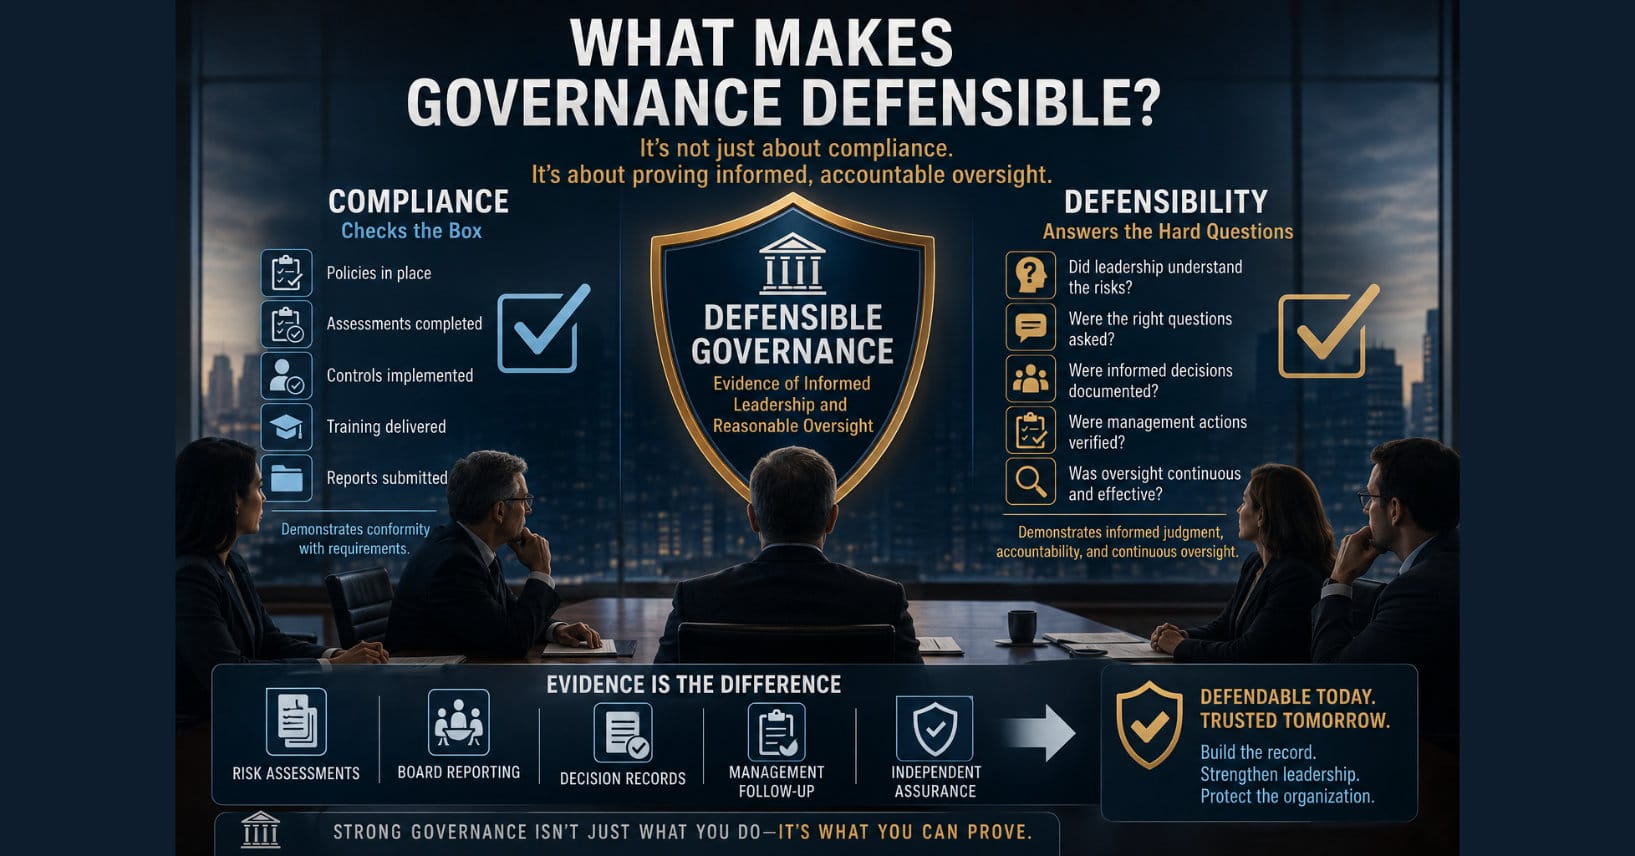
What Makes Governance Defensible?
What separates organizations that survive cyber scrutiny from those that don’t? Defensible governance is built on evidence, accountability, and disciplined oversight.
-
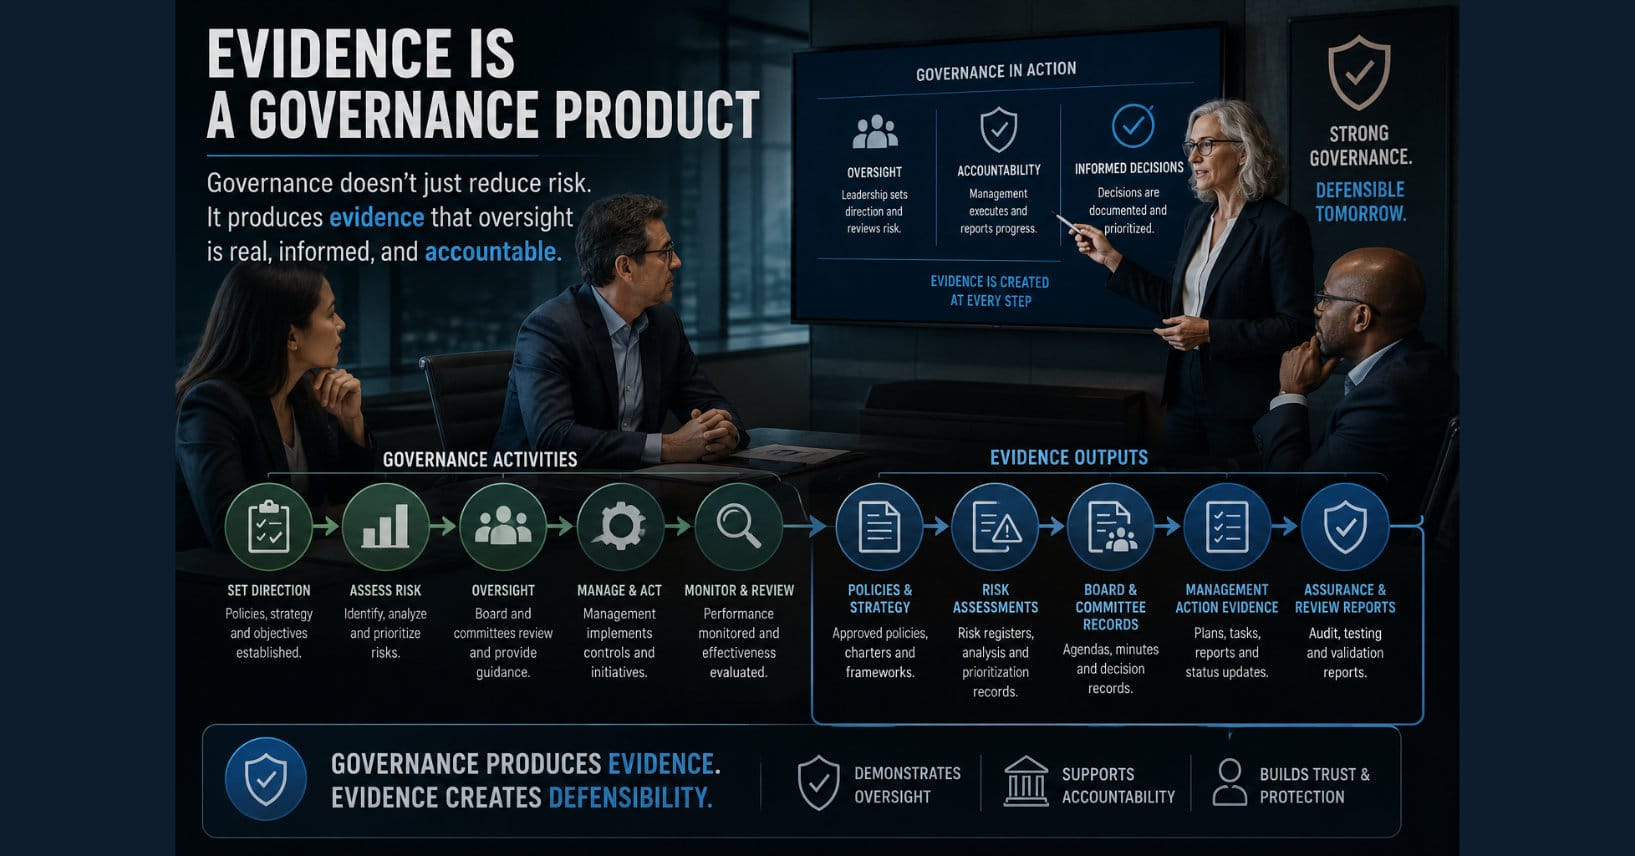
Evidence Is a Governance Product
Cybersecurity governance is often judged after an incident, but the strongest evidence is created long before a crisis occurs. This article explains why governance itself…