Summary
California’s cybersecurity audit regulations introduce significant new accountability requirements for businesses subject to the California Consumer Privacy Act (CCPA).
Effective January 1, 2026, the regulations establish annual cybersecurity audits for qualifying businesses whose processing of consumers’ personal information presents significant security risks. The largest covered businesses begin their initial audit period January 1, 2027, with their first certification deadline on April 1, 2028.
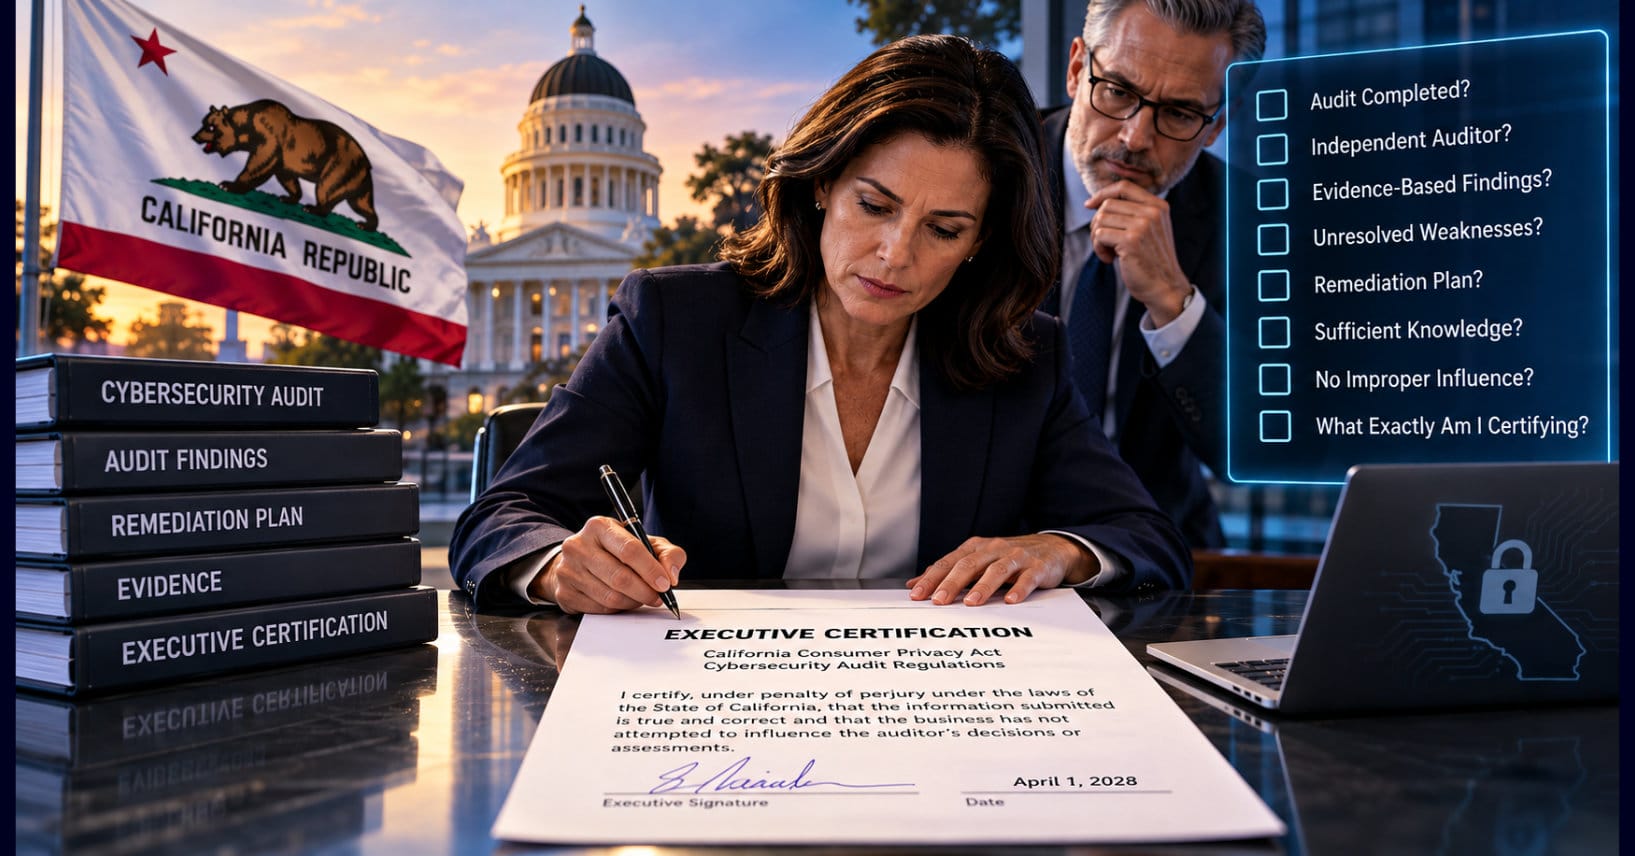
Under Section 7124, a qualifying member of executive management must certify that the required cybersecurity audit was completed. The certification includes an attestation under penalty of perjury concerning the accuracy of submitted information and the absence of improper influence over the auditor.
Importantly, this is not a certification that every cybersecurity control is effective or that all identified weaknesses have been remediated.
The article examines the distinction between audit completion, independent assessment, management accountability, and executive certification. It also addresses auditor independence, evidence-based findings, remediation planning, record retention, and the responsibilities of boards and executive management.
Using the Cyber Governance Center’s Defensible Evidence Framework™ and Evidentiary Architecture™, the article introduces a structured progression:
Regulatory Obligation → Applicability Decision → Audit Scope → Independent Assessment → Findings → Remediation Plan → Executive Review → Certification → Retained Evidence
The central governance lesson is that an executive signature must be supported by a reliable, independently examinable process.
A defensible certification is the conclusion of an evidence-based governance process—not a substitute for one.
A cybersecurity audit is completed.
The auditor documents the organization’s cybersecurity program, evaluates its controls, and identifies deficiencies.
Management receives the report.
Some findings have been remediated.
Others remain unresolved.
Several require substantial investment.
One involves a critical third-party service.
Another concerns a control that has repeatedly failed testing.
The organization prepares its required certification for submission to California regulators.
An executive is asked to sign.
What, exactly, is that executive certifying?
That the audit occurred?
That the audit was sufficiently thorough?
That the auditor was independent?
That management understands the findings?
That the cybersecurity program is effective?
Or that the organization has accepted responsibility for deficiencies that remain unresolved?
These questions are becoming increasingly consequential under California’s new cybersecurity audit regulations.
The California Privacy Protection Agency (CPPA), also known as CalPrivacy, has established annual cybersecurity audit requirements for certain businesses whose processing of consumers’ personal information presents significant risk to consumers’ security.
The regulations became effective January 1, 2026, with the first audit reporting and certification deadlines beginning April 1, 2028.
For the earliest group of covered businesses, however, the initial audit period begins January 1, 2027.
That is just over two months away.
And the certification requirement contains a provision that deserves particular attention.
The executive submitting the certification must attest, under penalty of perjury under California law, that the submitted information is true and correct and that the business has not attempted to influence the auditor’s decisions or assessments.
This is not a certification that the organization is free from cybersecurity weaknesses.
It is not a blanket guarantee that every control is effective.
It is a legally prescribed certification concerning completion of the required audit, the accuracy of the submitted information, and the absence of improper influence over the auditor.
That distinction matters.
But it does not eliminate the governance challenge.
How can an executive responsibly certify the completion of an audit without understanding whether the underlying audit process was complete, independent, and supported by reliable evidence?
California’s regulations are bringing that question into sharper focus.
California Has Already Adopted the Requirements
The first distinction is between a proposed regulatory obligation and an adopted one.
California’s cybersecurity audit requirements are not awaiting legislative approval.
The CPPA adopted the regulations in July 2025.
The California Office of Administrative Law approved them in September 2025.
They became effective January 1, 2026.
The implementation deadlines are phased, but the regulatory framework is established.
That distinction is important for executives developing their 2027 compliance plans.
For the first group of covered businesses, the relevant question is no longer whether California will impose an annual cybersecurity audit requirement.
It is whether the organization will be ready when its first audit period begins.
The regulations appear in Title 11 of the California Code of Regulations, Article 9, Sections 7120 through 7124.
They address applicability, timing, auditor independence, audit content, and certification of completion.
The certification requirement is found in Section 7124.
The audit requirement itself is broader than the certification.
And the executive’s signature is only one component of the organization’s obligations.
Who Must Conduct These Audits?
California’s requirement does not apply indiscriminately to every business.
Section 7120 applies to businesses covered by the California Consumer Privacy Act when their processing of consumers’ personal information presents significant risk to consumers’ security.
The regulation identifies two principal paths to that determination.
One concerns businesses meeting the CCPA’s applicable revenue threshold and processing specified volumes of personal information.
The other concerns businesses deriving at least 50 percent of their annual revenue from selling or sharing consumers’ personal information.
For the first path, the regulation identifies businesses that meet the applicable revenue threshold and, during the preceding calendar year, either:
- Processed personal information of at least 250,000 consumers or households; or
- Processed sensitive personal information of at least 50,000 consumers.
These are not alternative revenue thresholds.
A business must evaluate the applicable CCPA definition and the specific audit triggers.
An organization should not assume that a large revenue figure alone establishes an audit obligation.
Nor should it assume that operating outside California eliminates exposure to the CCPA.
Applicability depends on the statutory and regulatory definitions, including relevant California consumer data processing activities.
The correct first step is a documented applicability determination.
Before management can certify an audit, it must establish whether the organization was required to conduct that audit in the first place.
That determination should be legally reviewed, documented, and revisited when relevant business circumstances change.
The Compliance Clock Begins Before the First Certification
California has established phased deadlines based on revenue.
| Revenue category | Initial audit period | First audit report and certification deadline |
|---|---|---|
| More than $100 million in 2026 annual gross revenue | January 1, 2027–January 1, 2028 | April 1, 2028 |
| $50 million–$100 million in 2027 annual gross revenue | January 1, 2028–January 1, 2029 | April 1, 2029 |
| Less than $50 million in 2028 annual gross revenue | January 1, 2029–January 1, 2030 | April 1, 2030 |
These deadlines apply to businesses that otherwise satisfy the audit applicability criteria. The table summarizes the phased schedule; precise threshold wording and applicable CCPA definitions should be checked against Section 7121.
The crucial distinction is between the audit period and the reporting deadline.
A business in the first category does not begin preparing its cybersecurity program on April 1, 2028.
Its first audit evaluates the period beginning January 1, 2027.
That means the organization needs to establish the processes, controls, records, and governance mechanisms necessary to support an audit of that period.
Waiting until the certification deadline to organize the evidence would misunderstand the nature of the obligation.
April 1, 2028, is the first reporting deadline for the largest covered businesses. January 1, 2027, is the beginning of the period they must be prepared to substantiate.
What the Executive Actually Certifies
Section 7124 provides the most important answer to the question posed in this article’s title.
The business must submit an annual written certification that it completed the required cybersecurity audit.
The certification must be completed by a member of the executive management team who meets three conditions.
The individual must be directly responsible for the business’s cybersecurity audit compliance.
The individual must possess sufficient knowledge of the audit to provide accurate information.
And the individual must have authority to submit the certification to the CPPA.
The submission must identify the business and a contact person.
It must state that the cybersecurity audit was completed.
It must identify the period covered.
It must identify the executive submitting the certification.
And it must include an electronically signed attestation under penalty of perjury.
The attestation addresses the truth and correctness of the submitted information and confirms that the business has not attempted to influence the auditor’s decisions or assessments.
This is a carefully defined obligation.
The executive is not expressly certifying that every cybersecurity control is effective.
The executive is not guaranteeing that the business will experience no cybersecurity incidents.
The executive is not personally warranting that every audit finding has been remediated.
But the executive is making a formal representation about completion of a legally required audit.
The certification is therefore more consequential than an informal management acknowledgment.
It must be supported by sufficient knowledge and reliable information.
A signature based solely on an unsupported assurance that the audit was completed would create an obvious governance concern.
The regulation requires an executive with sufficient knowledge to certify the audit’s completion. It does not permit an organization to substitute executive rank for actual knowledge.
The Auditor’s Independence Is Part of the Governance Problem
The regulations require the cybersecurity audit to be conducted by a qualified, objective, independent professional.
That professional may be internal or external, subject to the applicable independence requirements.
The regulation addresses the auditor’s qualifications and objectivity.
It also establishes requirements concerning the relationship between the auditor and the business.
The underlying principle is straightforward.
An audit intended to evaluate the effectiveness of an organization’s cybersecurity program cannot provide meaningful assurance if the auditor’s judgments are improperly controlled by the people whose activities are being evaluated.
This creates a distinction between legitimate management involvement and improper influence.
Management may provide evidence.
It may explain business processes.
It may identify relevant systems and controls.
It may challenge factual inaccuracies.
It may supply additional information.
But management cannot appropriately pressure the auditor to suppress unfavorable findings or alter professional conclusions merely to produce a more favorable report.
That distinction becomes especially important because the executive certification expressly addresses attempts to influence the auditor’s decisions or assessments.
An organization should therefore establish safeguards around audit independence before the audit begins.
Those safeguards should address auditor selection, reporting relationships, conflicts of interest, access to evidence, disagreements over findings, and escalation of suspected interference.
The objective is not to eliminate legitimate dialogue between management and the auditor.
It is to preserve the auditor’s independent professional judgment.
An audit’s credibility depends not only on what the auditor examined, but also on whether the auditor was free to report what the evidence established.
The Audit Must Examine More Than Written Policies
One of the most consequential features of California’s regulations is the required audit scope.
Section 7123 does not merely ask whether a business possesses cybersecurity policies.
It requires an assessment of the cybersecurity program’s establishment, implementation, maintenance, and enforcement.
The auditor must evaluate how the program protects personal information against unauthorized access, destruction, use, modification, or disclosure, as well as unauthorized activity resulting in loss of availability.
The regulation identifies numerous cybersecurity program components for assessment when applicable.
These include authentication, encryption, access controls, vulnerability management, security testing, logging, incident response, and business continuity and disaster recovery.
The distinction between policy existence and operational effectiveness is fundamental.
An organization may have a written policy requiring multifactor authentication.
That does not establish whether the requirement is consistently enforced.
It may have a vulnerability management policy.
That does not demonstrate whether consequential vulnerabilities are remediated within established timeframes.
It may have an incident response plan.
That does not prove the organization’s response capabilities have been tested.
It may have third-party security requirements.
That does not establish whether relevant vendor controls are functioning.
California’s framework directs attention toward the relationship between documented cybersecurity requirements and their actual implementation.
The audit must examine whether cybersecurity governance operates—not merely whether cybersecurity policies exist.
Management Assertions Are Not Enough
Section 7122 contains a requirement that deserves considerably more attention than it has received.
Cybersecurity audit findings cannot rely primarily on management assertions or attestations.
Instead, findings must rely primarily on specific evidence the auditor considers appropriate.
That evidence may include documents, sampling, testing, and interviews.
This requirement addresses a persistent weakness in organizational assurance.
Management may believe a control is operating effectively.
The responsible team may report that the control is functioning.
A dashboard may display a favorable status.
A policy owner may confirm that procedures are being followed.
But none of those statements independently establishes that the control actually works.
Consider a business that reports that privileged access is reviewed quarterly.
The auditor asks for evidence.
Management produces the access review policy.
The policy states that quarterly reviews are mandatory.
But the organization cannot produce completed review records for two quarters.
The policy demonstrates an obligation.
It does not demonstrate execution.
Now consider a company that reports successful vulnerability remediation.
The remediation system contains closed tickets.
But subsequent testing shows that several weaknesses remain exploitable.
The tickets demonstrate administrative closure.
They do not establish that the underlying exposure was eliminated.
This distinction is central to the Cyber Governance Center’s Defensible Evidence Framework™.
An assertion is not evidence merely because an authorized executive makes it.
And a control is not effective merely because a dashboard reports that it exists.
California’s audit requirements reinforce the importance of examining actual control operation.
The Audit Report Must Document Weaknesses and Remediation Plans
The regulations also specify what the cybersecurity audit report must contain.
Section 7123 requires the report to describe the information system, identify the assessed policies and practices, explain the audit criteria, and identify the evidence examined.
The report must address the effectiveness of applicable cybersecurity program components.
It must also identify and describe relevant gaps or weaknesses that increase risks to consumers’ personal information.
Importantly, the report must document the business’s plan to address identified gaps and weaknesses, including the timeframe for resolving them.
This creates a meaningful connection between assurance and management responsibility.
The auditor identifies weaknesses.
The business establishes how those weaknesses will be addressed.
The report preserves the relationship between the findings and the proposed corrective actions.
Consider a critical deficiency involving a third-party identity platform.
The auditor determines that a configuration weakness could expose consumers’ personal information.
Management acknowledges the finding.
The vendor estimates that corrective action will require four months.
The business must determine how it will manage the exposure during that period.
Will it implement compensating controls?
Will it restrict affected functionality?
Will it accelerate vendor remediation?
Will it accept the residual risk temporarily?
The audit report’s remediation-plan requirement does not, by itself, prescribe which business decision must be made.
But it does require documentation of the planned response and its timeframe.
That is an important governance distinction.
The audit identifies the weakness. Management remains accountable for determining and executing an appropriate response.
The Executive Certification Is Not an Audit Opinion
Organizations must distinguish three different forms of assurance.
The first is the auditor’s professional assessment.
The auditor evaluates the cybersecurity program, examines evidence, identifies weaknesses, and documents findings.
The second is management’s responsibility for the cybersecurity program.
Management establishes controls, allocates resources, addresses deficiencies, and makes authorized risk decisions.
The third is the executive certification submitted to California.
That certification confirms completion of the required audit and contains the prescribed attestation.
These responsibilities are related.
They are not interchangeable.
The auditor does not assume management’s responsibility for cybersecurity risk.
Management does not become an independent auditor by signing the certification.
And the executive’s certification does not transform the audit report into a guarantee of cybersecurity effectiveness.
There is another important distinction.
The regulation requires the executive certification to be submitted to the CPPA. It does not establish a general requirement to submit the complete audit report with that annual certification.
The report must nevertheless be completed and maintained in accordance with the regulations, and the business must comply with applicable regulatory requests and obligations.
Section 7122 also requires the business and auditor to retain relevant audit documents for at least five years following completion.
This reinforces the importance of preserving the underlying evidence.
An organization cannot treat the certification as the end of its assurance responsibilities.
It must be capable of supporting the certification with a defensible record.
What Should an Executive Review Before Signing?
California specifies the certification’s contents and the qualifications of the executive who submits it.
It does not prescribe a universal internal certification checklist.
Nevertheless, organizations should establish a formal review process that enables the responsible executive to develop sufficient knowledge of the audit.
That process should answer several questions.
Was the audit required?
The organization should possess a documented applicability determination supported by relevant business and data-processing information.
Was the audit completed for the correct period?
The executive should be able to identify the audit period and establish that the required report was completed.
Was the auditor qualified and independent?
The organization should document auditor qualifications, independence safeguards, and any identified conflicts.
Was the required scope addressed?
Management should understand how the audit covered applicable cybersecurity program components and whether any scope limitations require attention.
Was the audit supported by appropriate evidence?
The executive should have a reasonable basis for understanding that the audit was evidence-based rather than dependent primarily on unsupported management assertions.
Were significant findings communicated?
The executive should understand the existence of consequential weaknesses, even though the certification does not require attesting that every weakness has been corrected.
Are remediation plans documented?
The organization should establish ownership, proposed corrective action, and timeframes for identified deficiencies.
Were disagreements with the auditor handled appropriately?
The executive should understand whether disputes occurred and whether the auditor’s independent judgment was preserved.
Is the certification itself accurate?
The business name, contact information, audit period, completion statement, executive qualifications, and other required information must be correct.
These are recommended governance safeguards, not additional certification elements imposed by Section 7124.
Their purpose is to establish a defensible basis for the executive’s signature.
The Board’s Role Is Oversight, Not Automatic Certification
An important detail in California’s final regulations concerns the board of directors.
Earlier regulatory proposals contemplated a certification signed by a board member, governing-body member, or senior executive.
The final regulations took a different approach.
Section 7124 requires certification by a qualifying member of executive management.
The CPPA’s final rulemaking explanation also documents changes removing certain proposed requirements involving board reporting and board-level certification.
This distinction matters.
It would be inaccurate to tell directors that California’s final cybersecurity audit regulations require them personally to sign the annual certification.
They do not.
But that does not eliminate the board’s broader oversight responsibilities.
Directors should understand whether the organization is subject to the requirements.
They should expect management to establish an appropriate audit process.
They should understand whether significant findings create enterprise risk.
And they should expect assurance that the responsible executive possesses the information and authority necessary to submit an accurate certification.
The board should not attempt to substitute its judgment for the independent auditor’s findings.
Nor should it assume responsibility for operational remediation decisions properly assigned to management.
Its role is to oversee whether the governance structure functions.
California places the certification obligation on qualifying executive management. Effective board oversight remains essential to ensuring the organization can support that certification.
Existing Audits May Help, but They Are Not Automatic Substitutes
Many organizations already undergo cybersecurity assessments.
SOC 2 examinations.
ISO/IEC 27001 audits.
NIST Cybersecurity Framework assessments.
Industry-specific security reviews.
Customer-requested assurance engagements.
These activities may provide valuable evidence.
California’s regulations permit businesses to use audits, assessments, or evaluations prepared for another purpose when they satisfy all applicable requirements of Article 9, either independently or through supplementation.
This is a practical accommodation.
It does not mean every existing cybersecurity assessment automatically satisfies California’s requirements.
The organization must evaluate the scope, audit period, independence, evidence, reporting content, and other applicable provisions.
For example, an existing SOC 2 examination may provide substantial evidence concerning access controls, monitoring, change management, and security operations.
But its reporting period or scope may differ from the California requirements.
An ISO/IEC 27001 certification may demonstrate that an information security management system has been evaluated.
It does not necessarily establish that every California-specific audit reporting requirement has been satisfied.
A NIST-based assessment may provide a strong foundation.
But the organization must still establish whether the assessment meets the regulation’s complete requirements.
The governance principle is straightforward.
An existing audit is reusable evidence only to the extent that it satisfies the obligation for which it is being reused.
The existence of an assurance report is not the same as proof that the report meets every relevant regulatory requirement.
The Defensible Evidence Framework™: From Obligation to Certification
California’s requirements illustrate why cybersecurity governance needs an evidentiary structure that connects regulatory obligations to operational execution.
The Cyber Governance Center’s Defensible Evidence Framework™ addresses the need to establish whether governance decisions, control activities, and assurance conclusions can be independently reconstructed.
For California’s cybersecurity audit certification, the progression can be expressed as:
Regulatory Obligation → Applicability Decision → Audit Scope → Independent Assessment → Findings → Remediation Plan → Executive Review → Certification → Retained Evidence
Each stage creates a distinct evidentiary requirement.
The regulatory obligation establishes what the organization must do.
The applicability decision establishes why the requirement applies.
The audit scope defines what must be examined.
The independent assessment evaluates the relevant cybersecurity program.
The findings identify weaknesses and control effectiveness.
The remediation plan documents management’s intended response.
The executive review establishes the basis for the certifying individual’s knowledge.
The certification communicates the prescribed representations to the regulator.
The retained evidence supports subsequent examination of the process.
A break in this progression can create governance uncertainty.
An audit may be completed without a defensible applicability determination.
A report may exist without sufficient evidence of auditor independence.
A remediation plan may identify corrective actions without accountable owners.
An executive may sign without receiving sufficient information about the audit.
Or the organization may submit an accurate certification but fail to preserve the records necessary to substantiate the underlying process.
The objective is not simply to produce more documentation.
It is to preserve the relationship between obligation, execution, decision, and evidence.
The Evidentiary Architecture™ of Executive Accountability
The Cyber Governance Center’s Evidentiary Architecture™ extends this principle by connecting the audit process to the organization’s governance structure.
An effective architecture should make several relationships visible.
Which regulatory obligation required the audit?
Who determined applicability?
Who approved the audit scope?
How was auditor independence established?
What evidence supported the findings?
Which weaknesses required corrective action?
Who possesses authority to accept residual risk?
Who approved remediation priorities and timeframes?
Who reviewed the completed audit?
Who submitted the certification?
And where is the supporting evidence retained?
These questions are particularly important when responsibility spans multiple organizational functions.
Legal may interpret applicability.
Privacy may identify relevant processing activities.
Cybersecurity may operate the controls.
Internal audit or an external professional may perform the assessment.
Business owners may authorize remediation priorities.
Executive management may certify completion.
The board may oversee the overall risk governance process.
No single function necessarily controls every stage.
Without an integrated evidentiary architecture, the organization may struggle to demonstrate how the pieces fit together.
That fragmentation becomes consequential when a regulator asks the organization to explain its compliance.
Executive accountability requires more than identifying the person who signs. It requires establishing the governance process that makes the signature defensible.
The Real Test Comes When the Audit Identifies a Serious Weakness
Consider a hypothetical covered business preparing its first California cybersecurity audit.
The independent auditor identifies a significant access-control deficiency.
The weakness affects systems containing sensitive personal information.
Management acknowledges the finding.
The technical team proposes corrective action.
The business owner determines that immediate remediation would disrupt a critical service.
The organization adopts a phased remediation plan.
The auditor documents the deficiency and the plan.
The audit is completed.
The responsible executive prepares to certify completion.
Can the executive sign?
The presence of an unresolved finding does not automatically prohibit certification.
The regulation does not require every deficiency to be corrected before the completion certification can be submitted.
But the organization must distinguish the accuracy of the certification from the acceptability of the underlying cybersecurity risk.
The executive must have a sufficient basis to establish that the required audit was completed and that the certification’s representations are accurate.
Separately, management must determine how the identified exposure will be addressed.
The responsible risk owner should understand the business consequences.
The remediation plan should identify appropriate actions and timeframes.
Any decision to continue operating with the exposure should be authorized through the organization’s established risk governance process.
And the organization should preserve evidence of subsequent remediation and validation.
The distinction is critical.
An executive may accurately certify that an audit was completed while the organization still has unresolved cybersecurity risks.
But an accurate completion certification does not excuse inadequate management of those risks.
The audit and the risk decision are separate governance obligations.
Both require defensible evidence.
California Is Moving the Discussion From Compliance Activity to Evidentiary Accountability
The significance of California’s requirements extends beyond the certification form.
The regulations establish an audit process that emphasizes independence, defined scope, evidence-based findings, documented weaknesses, and remediation planning.
They require a qualifying executive to make a formal submission under penalty of perjury.
And they establish record-retention obligations that support subsequent examination.
These requirements create a stronger relationship between cybersecurity assurance and organizational accountability.
They also expose the limitations of treating audits as isolated compliance exercises.
A business cannot reasonably approach the process as merely obtaining a report and collecting a signature.
It must establish that the audit was conducted appropriately.
It must understand what the findings mean.
It must document plans for addressing identified deficiencies.
It must preserve the evidence.
And it must ensure that the responsible executive can accurately certify the required facts.
The broader governance lesson is not confined to California.
Organizations increasingly face expectations that cybersecurity representations be supported by demonstrable evidence.
That trend makes the distinction between management assertion and verified control effectiveness more important.
It also raises the standard for executive understanding of assurance processes.
The executive does not need to personally perform every technical test.
But the executive should be able to explain the basis for the certification.
A defensible certification is the conclusion of an evidence-based governance process—not a substitute for one.
The Question Every Board Should Ask
California’s first cybersecurity audit certification deadline remains more than a year away.
For the largest covered businesses, however, the first audit period begins January 1, 2027.
Organizations should use the remaining preparation period to establish applicability, confirm audit scope, evaluate auditor independence, identify evidence requirements, and define executive certification responsibilities.
Boards should ask management a simple question:
If the responsible executive had to certify our cybersecurity audit today, could we demonstrate exactly what the certification means, what evidence supports it, and who is accountable for unresolved findings?
A confident answer should not depend on assurances that the cybersecurity team is doing its job.
It should depend on a documented, independently supportable process.
The executive’s signature is the visible endpoint.
The underlying governance architecture determines whether that signature is defensible.
The Cyber Governance Center Perspective
California’s cybersecurity audit regulations illustrate an important development in enterprise governance.
Regulatory accountability increasingly depends on the quality of the evidence connecting organizational obligations to operational execution.
The executive certification required by Section 7124 is narrowly defined.
It confirms completion of the required audit and includes prescribed representations concerning accuracy and auditor independence.
It does not certify that the organization is free from cybersecurity risk.
But the surrounding regulatory framework requires much more than a signed form.
It requires qualified independent assessment, evidence-based findings, documentation of weaknesses, remediation planning, and retention of relevant records.
The Cyber Governance Center’s Defensible Evidence Framework™ and Evidentiary Architecture™ provide a way to organize those responsibilities into a reconstructable governance process.
The objective is not to turn executives into cybersecurity auditors.
It is to ensure that executives possess the knowledge, authority, and reliable evidence necessary to make consequential representations.
California is about to require qualifying executives to certify cybersecurity audit completion. The real governance challenge is ensuring they can demonstrate why that certification is accurate.
Clarity. Accountability. Defensibility.
Sources and Further Reading
California Privacy Protection Agency — September 23, 2025
California Finalizes Regulations to Strengthen Consumers’ Privacy.
Official announcement confirming adoption, effective dates, and phased cybersecurity audit certification deadlines.
California Privacy Protection Agency — Regulations Effective January 1, 2026
California Consumer Privacy Act Regulations, Article 9: Cybersecurity Audits.
Primary regulatory text, including Sections 7120–7124 governing applicability, timing, auditor independence, audit scope, and executive certification.
Read the official regulations (PDF)
California Code of Regulations — Title 11, Section 7124
Certification of Completion.
The controlling provision specifying executive qualifications, certification contents, submission requirements, and the attestation under penalty of perjury.
California Code of Regulations — Title 11, Section 7121
Timing Requirements for Cybersecurity Audits and Audit Reports.
The phased audit periods and reporting deadlines for covered businesses.
California Privacy Protection Agency — Final Statement of Reasons
CCPA Updates, Cybersecurity Audits, Risk Assessments, Automated Decisionmaking Technology, and Insurance Regulations.
Official explanation of regulatory changes, including revisions concerning auditor independence, executive reporting, and certification responsibilities.
Read the Final Statement of Reasons (PDF)
National Institute of Standards and Technology — February 2024
The NIST Cybersecurity Framework 2.0.
A voluntary framework for organizing cybersecurity governance, risk management, and operational security outcomes.