Evidence-Driven Cybersecurity Governance Series—Article 17
Organizations have long measured cybersecurity governance through operational metrics such as vulnerabilities, patching rates, audit findings, compliance status, and risk registers. While these indicators remain important, they reveal little about whether leadership can actually demonstrate informed oversight. This article introduces evidence readiness as a new governance metric—one that measures an organization’s ability to produce complete, current, traceable, accessible, and trustworthy governance evidence when it is needed.
Readers will learn why evidence readiness complements traditional governance metrics by focusing on demonstrability rather than activity alone. The article explains how boards can evaluate the quality of governance through measurable characteristics such as evidence completeness, currency, traceability, accessibility, and integrity. As expectations from regulators, insurers, investors, and courts continue to rise, organizations that measure governance through evidence readiness will be better positioned to demonstrate accountability, strengthen leadership confidence, and build more defensible cybersecurity governance.
Introducing the idea of measuring governance through evidence.
Organizations have long measured what governance does. The next generation of governance will measure what governance can prove.
Every organization measures something.
Operational performance.
Financial results.
Risk exposure.
Control effectiveness.
Compliance status.
These measurements help leaders understand how the organization is performing.
Cybersecurity governance is no different.
Boards receive dashboards.
Executives review scorecards.
Committees monitor trends.
Metrics drive decisions.
Yet one important measurement is usually missing.
How evidence-ready is our governance?
That question may become one of the defining measures of governance maturity.
Traditional Governance Metrics
Boards have become accustomed to reviewing familiar indicators.
Number of critical vulnerabilities.
Patch compliance.
Phishing susceptibility.
Incident response times.
Risk register status.
Audit findings.
Policy completion.
These metrics are valuable.
They describe operational health.
They describe security performance.
They do not necessarily describe governance maturity.
More importantly, they do not measure whether governance can be demonstrated.
Measuring Demonstrability
Evidence readiness measures something fundamentally different.
Not whether governance occurred.
Whether governance can be proven.
Can leadership demonstrate:
- Continuous board oversight?
- Timely risk communication?
- Well-documented decisions?
- Management accountability?
- Independent assurance?
- Traceable follow-through?
These questions move governance beyond activity.
They measure demonstrability.
Evidence Readiness Is Measurable
Like every mature discipline, governance should have measurable outcomes.
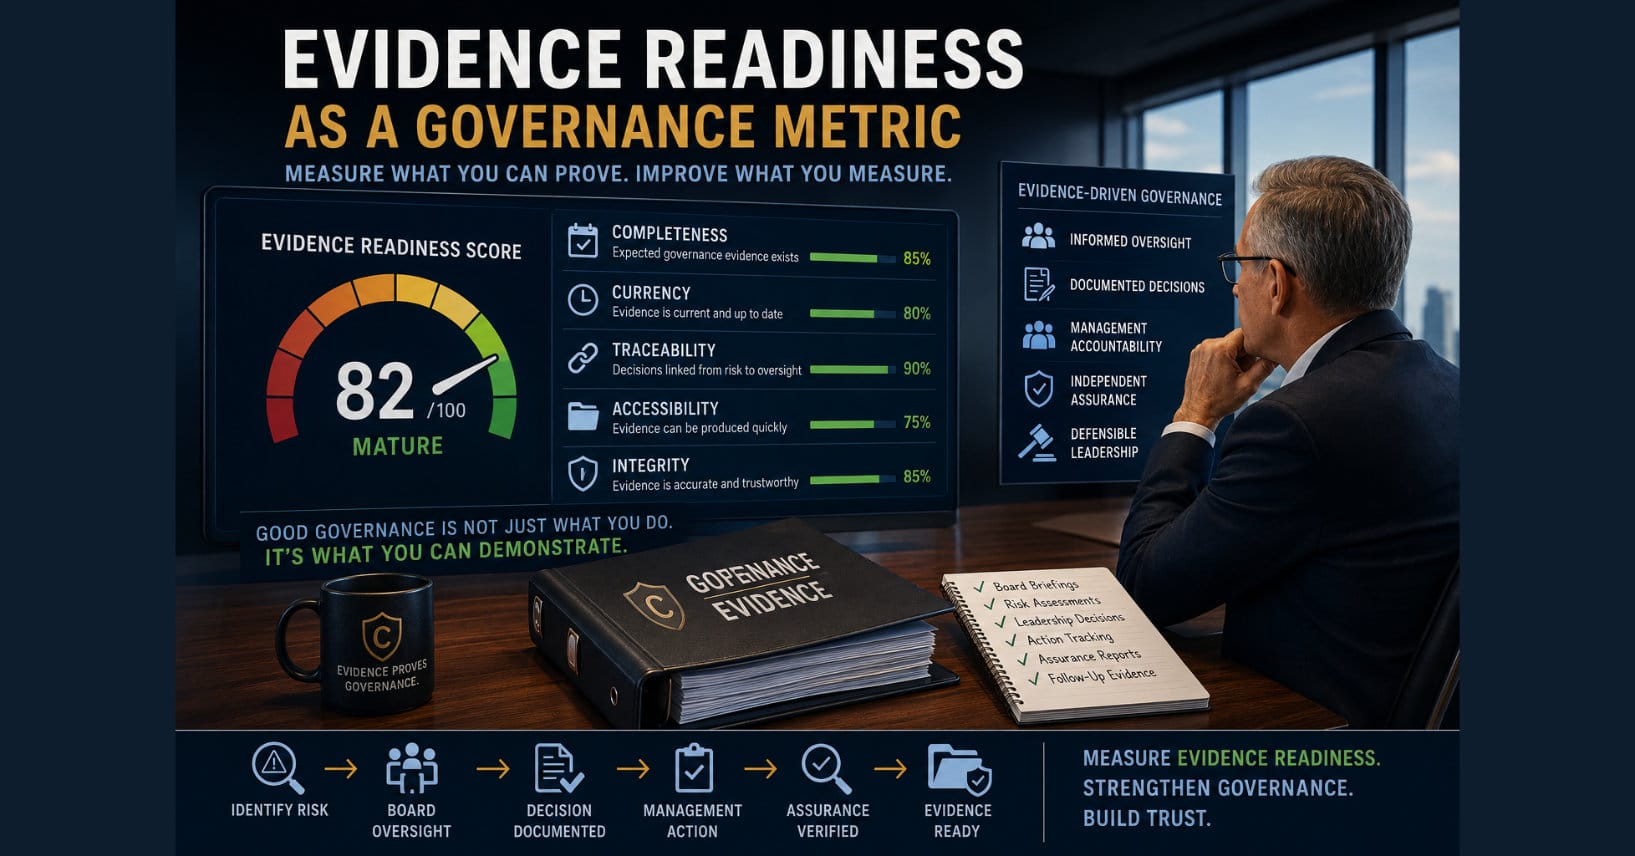
Evidence readiness can be evaluated across several dimensions.
Completeness.
Does the expected governance evidence exist?
Currency.
Does the evidence reflect today’s governance rather than last year’s?
Traceability.
Can governance decisions be followed from identified risk through board oversight, management action, and assurance?
Accessibility.
Can evidence be produced quickly when requested?
Integrity.
Can leadership demonstrate that governance records are accurate, authentic, and trustworthy?
These characteristics describe governance quality—not merely documentation quality.
A Different Kind of Dashboard
Imagine presenting a governance dashboard to the board that includes questions such as:
How current is our governance evidence?
How many board decisions have documented follow-through?
What percentage of material cyber risks have complete evidentiary chains?
How quickly can governance evidence be assembled for regulatory review?
Which governance activities consistently fail to produce supporting evidence?
These metrics reveal something traditional dashboards cannot.
The maturity of governance itself.
Better Metrics Create Better Behavior
Organizations improve what they measure.
When evidence readiness becomes visible, governance changes.
Decision records improve.
Action tracking becomes more disciplined.
Board reporting gains clarity.
Assurance activities become more meaningful.
Evidence repositories remain current.
The metric itself encourages better governance.
Evidence Readiness Complements Compliance
Evidence readiness is not another compliance framework.
It strengthens existing ones.
Organizations still need effective controls.
Strong risk management.
Independent audit.
Regulatory compliance.
Evidence readiness complements these disciplines by asking a simple question:
Can we demonstrate that leadership governed them responsibly?
Compliance answers whether requirements were met.
Evidence readiness answers whether governance can be proven.
A Governance Metric for the Future
Boards increasingly face expectations from regulators…
Questions from insurers…
Scrutiny from investors…
And accountability before courts.
Each expects more than verbal assurance.
Each expects evidence.
Organizations that measure evidence readiness today will be better prepared for those expectations tomorrow.
Not because they documented more.
Because they governed more intentionally.
Measuring What Matters Most
For years, cybersecurity metrics focused on technology.
Today’s governance metrics focus on oversight.
Tomorrow’s governance metrics will focus on evidence.
Because evidence is where governance becomes visible.
It is where accountability becomes measurable.
It is where defensibility becomes demonstrable.
Organizations that embrace evidence readiness as a governance metric will discover something important.
The act of measuring governance through evidence does more than improve reporting.
It improves governance itself.
From the Framework
This article is adapted from The Defensible Evidence Framework™ White Paper, which explores how organizations can create defensible governance evidence naturally through disciplined oversight rather than attempting to reconstruct it after a crisis.
The complete white paper is available for download here.
Coming Next
Article 18: The Future of Cyber Governance Is Evidentiary
Cybersecurity governance is entering a new era. Regulators are demanding greater accountability. Insurers are rewarding demonstrable oversight. Investors increasingly evaluate governance maturity alongside financial performance, and courts continue to examine leadership decisions through the lens of evidence. In the final article of this series, we’ll bring these trends together and explore why the future of cyber governance will be defined not merely by compliance or technical excellence, but by an organization’s ability to produce credible, connected, and defensible governance evidence.