
-
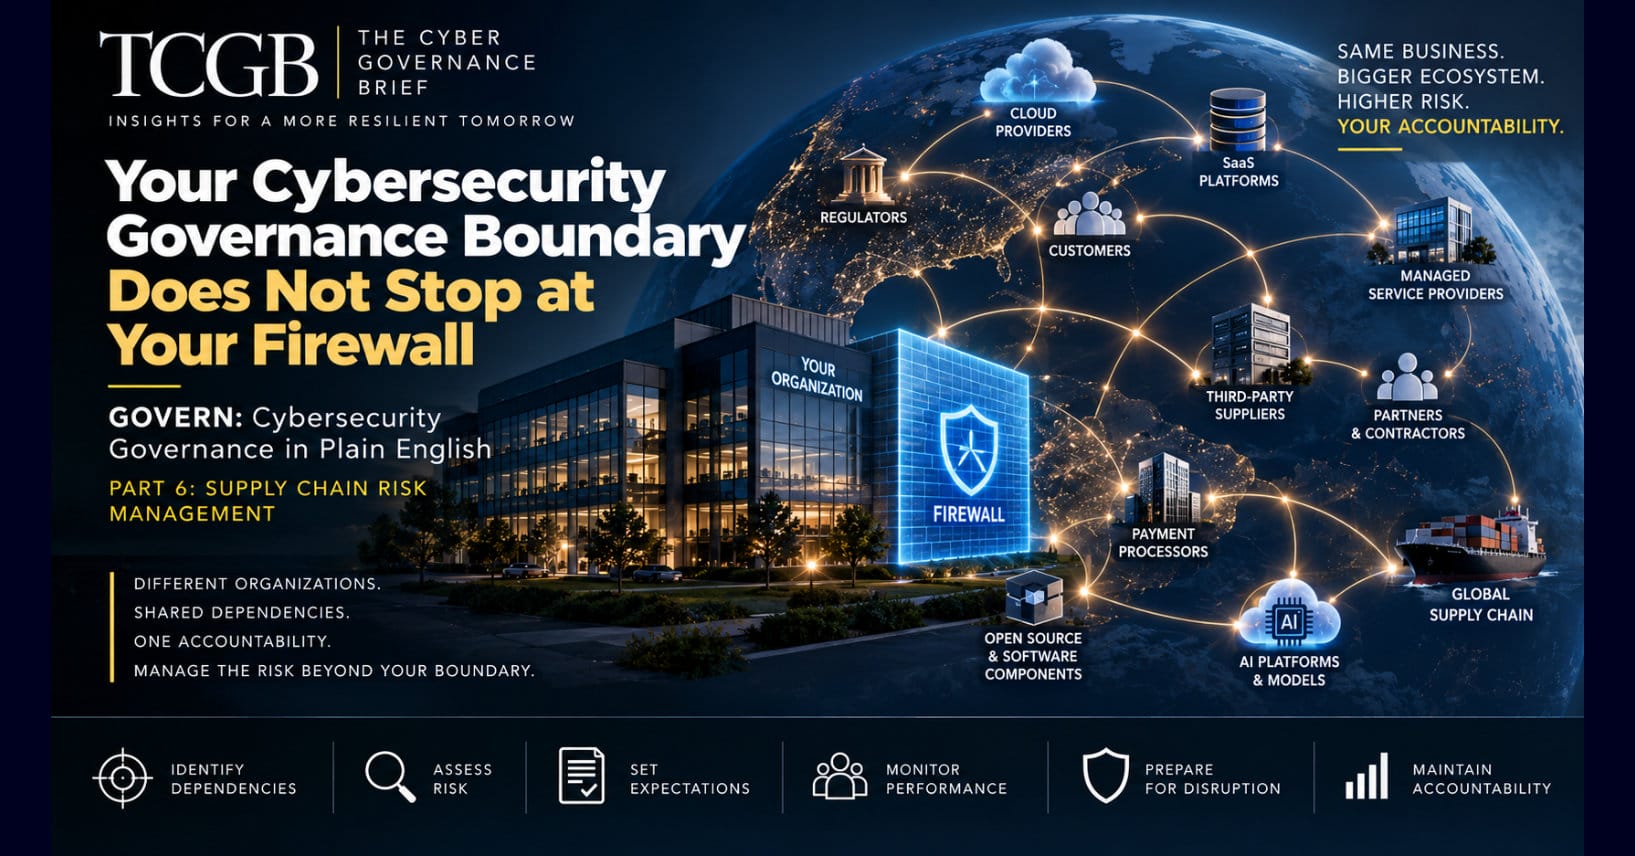
Your Cybersecurity Governance Boundary Does Not Stop at Your Firewall
GOVERN: Cybersecurity Governance in Plain English Summary: Part 6 of GOVERN: Cybersecurity Governance in Plain English explores Cybersecurity Supply Chain Risk Management (GV.SC), the final Category within NIST…
-
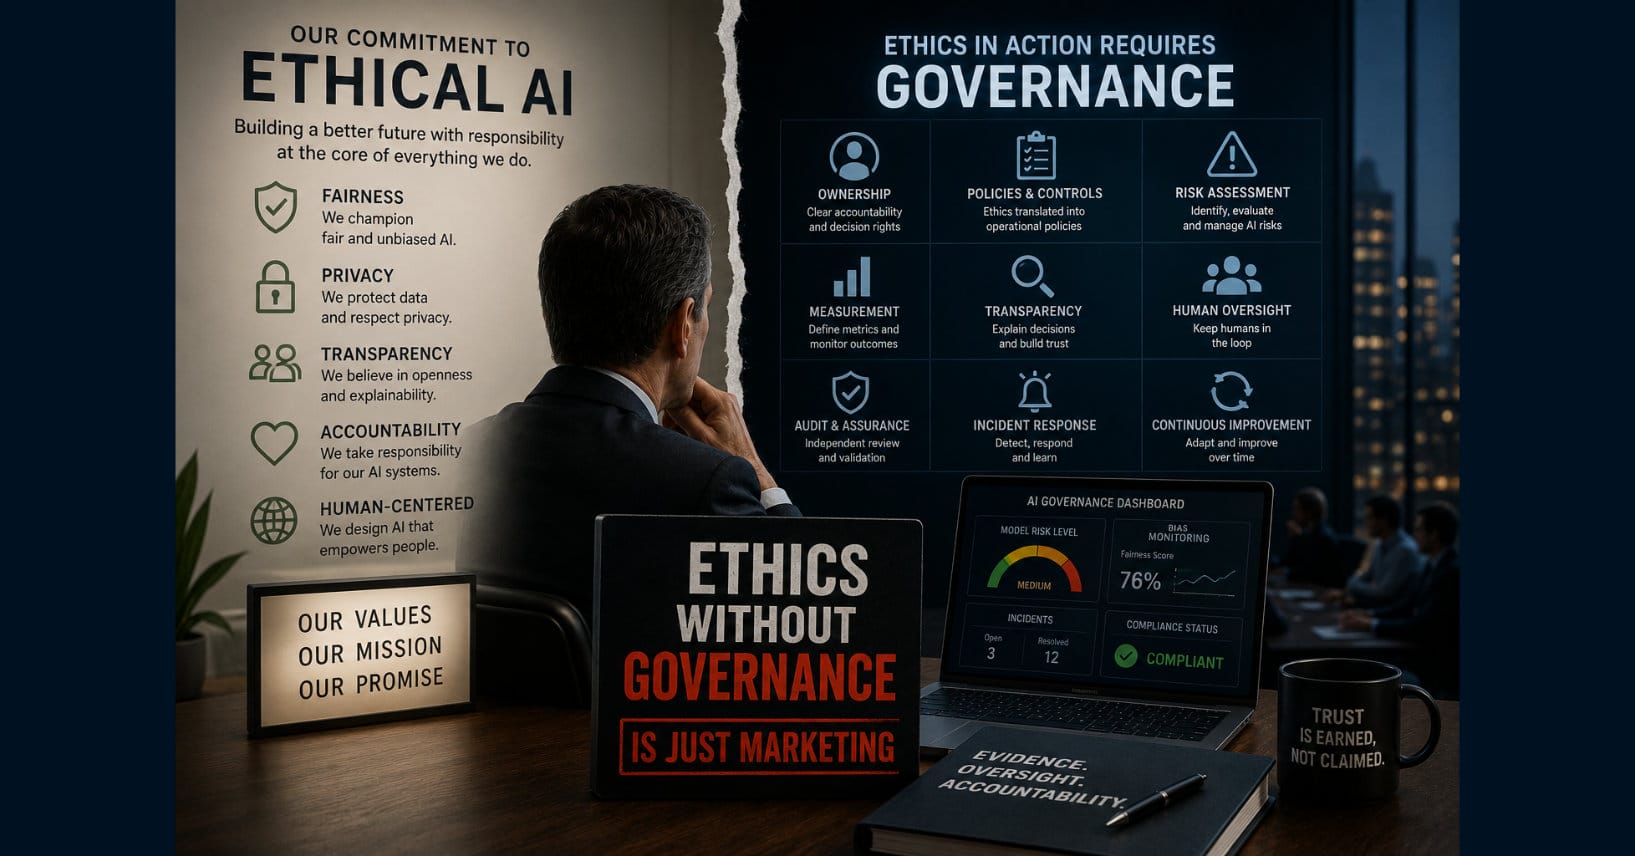
Ethics Without Governance Is Just Marketing
Write the WordPress excerpt, summary, tags, and SEO for article 15. Ethics Without Governance Is Just Marketing
-
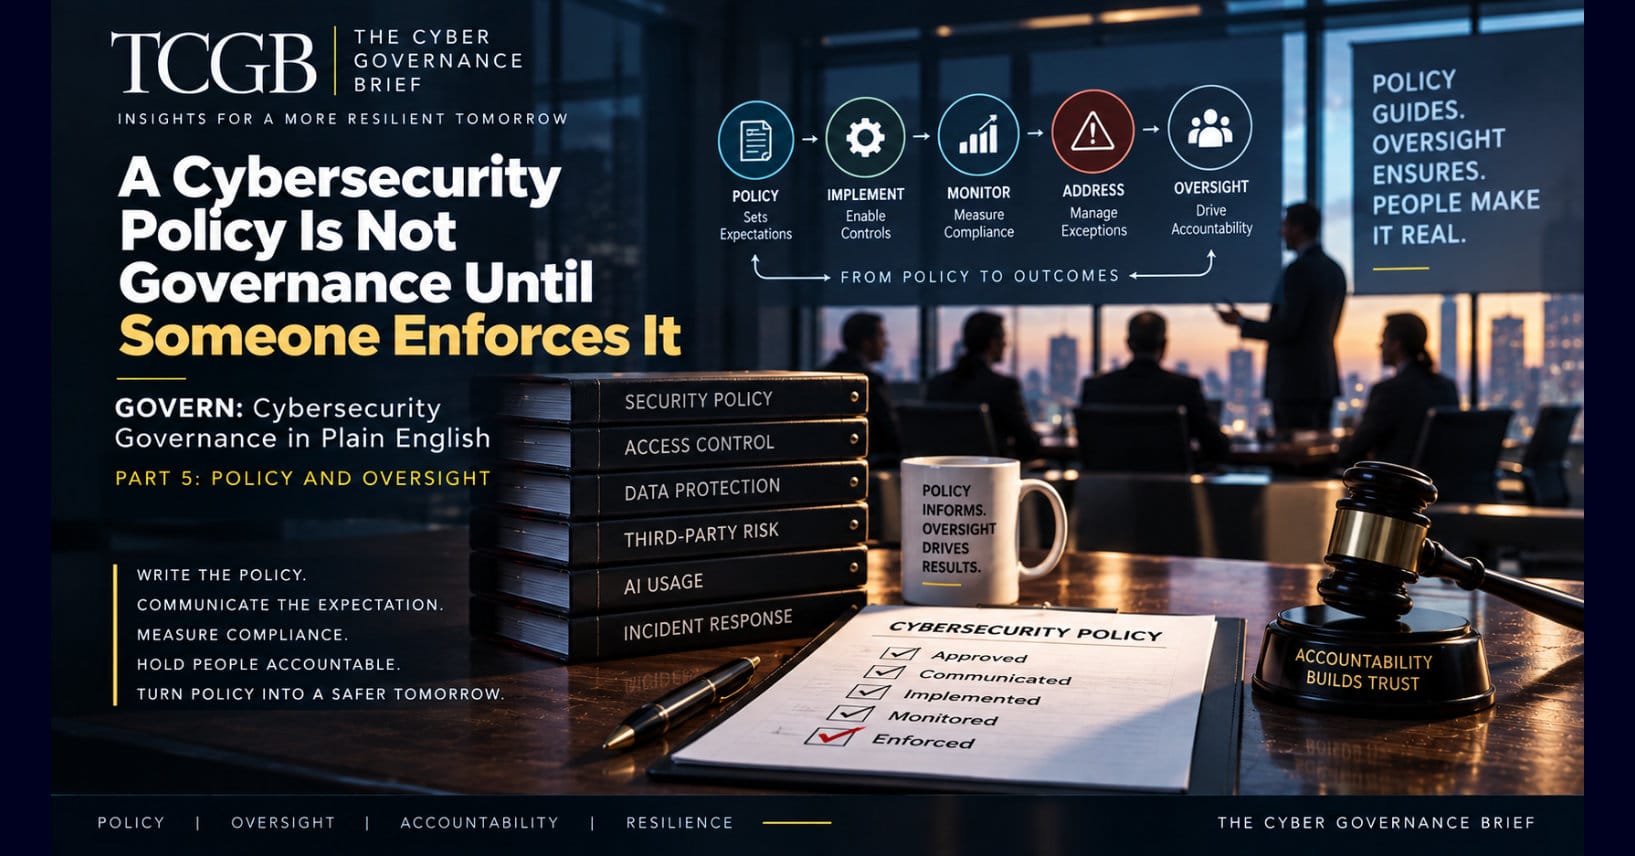
A Cybersecurity Policy Is Not Governance Until Someone Enforces It
A cybersecurity policy is only an expectation until it shapes behavior. Governance connects policy to implementation, evidence, exceptions, enforcement, and leadership oversight.
-
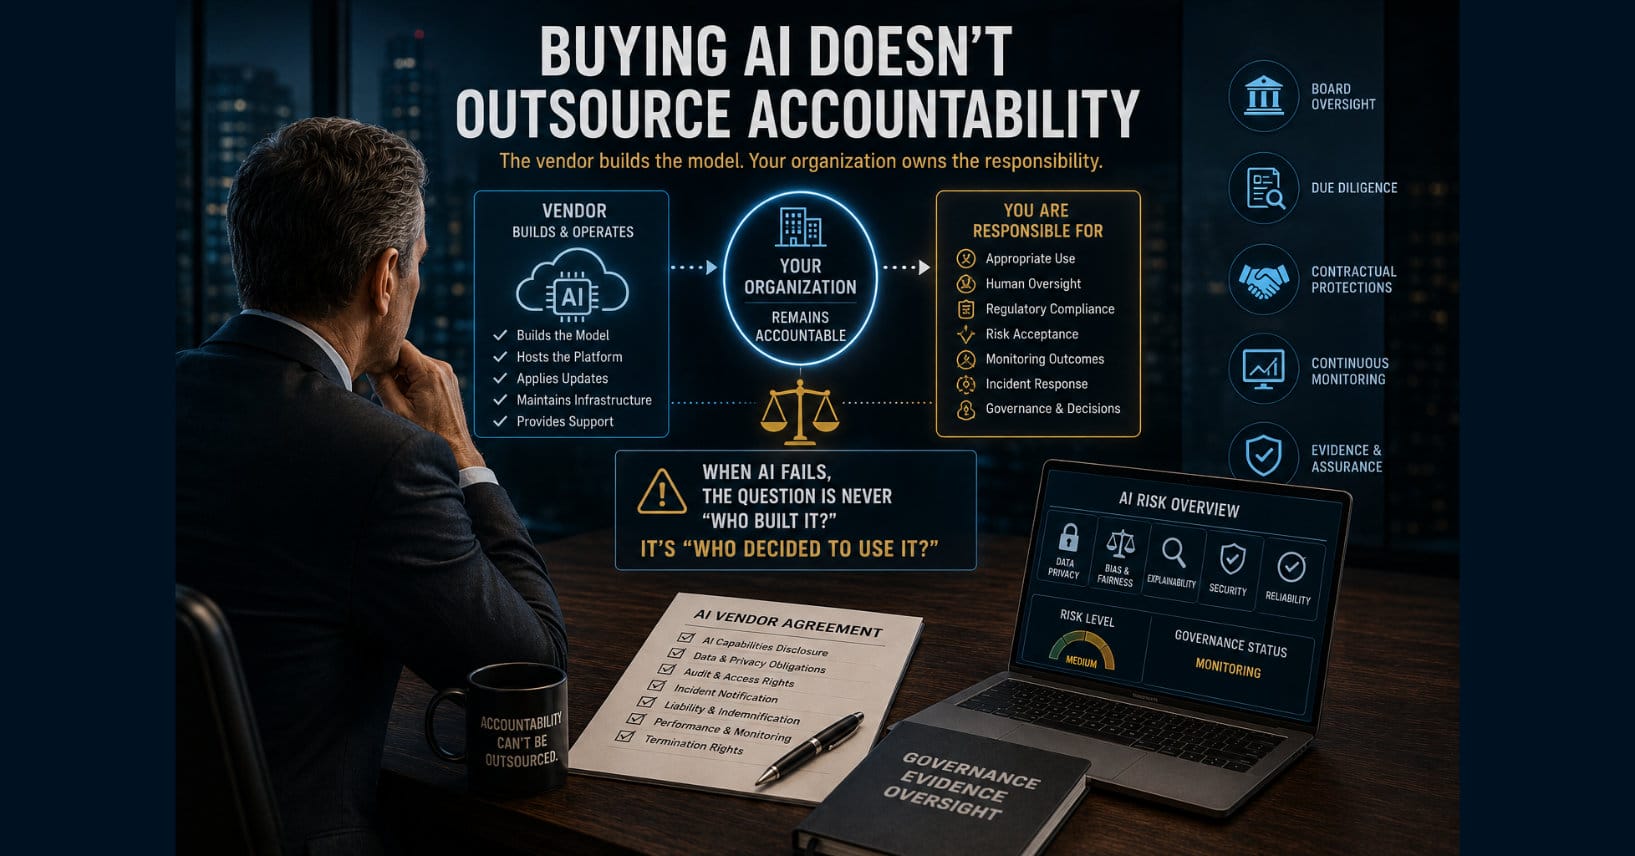
Buying AI Doesn’t Outsource Accountability
Buying AI doesn’t transfer accountability. Organizations remain responsible for governing vendor AI, managing risk, and demonstrating oversight.
-
Cybersecurity Accountability Cannot End With “IT Owns It”
Cybersecurity accountability cannot simply be assigned to IT. Managing technology, making risk decisions, and owning business consequences require different roles, authorities, and accountabilities.
-
Your Greatest AI Risk May Be Someone Else’s Model
The greatest AI risk may already exist inside your vendors’ software. Third-party AI requires governance, oversight, and evidence—not assumptions.
-
Someone Has to Decide How Much Cyber Risk Is Enough
Every organization accepts cybersecurity risk. The governance question is who decides how much is acceptable, who has authority to accept it, and who owns the residual…
-
Every AI Failure Becomes a Governance Test
Every AI failure becomes a governance test. Crisis leadership, accountability, and evidence determine how organizations are judged.
-
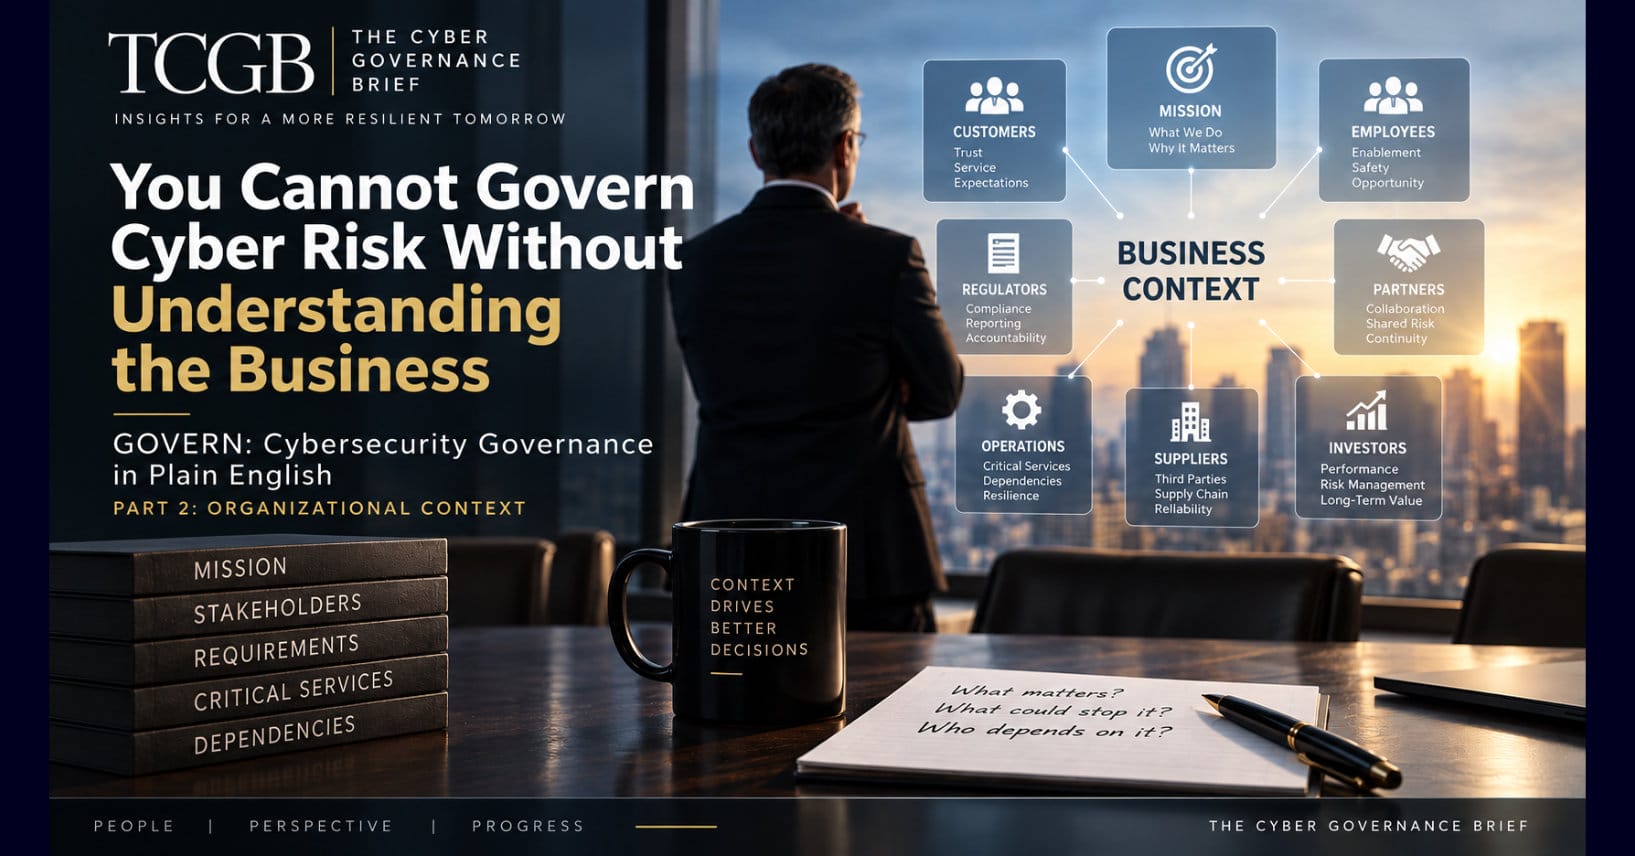
You Cannot Govern Cyber Risk Without Understanding the Business
You cannot govern cybersecurity risk without knowing what matters to the business. NIST CSF 2.0’s Organizational Context connects cyber risk to mission, stakeholders, obligations, critical services,…
-
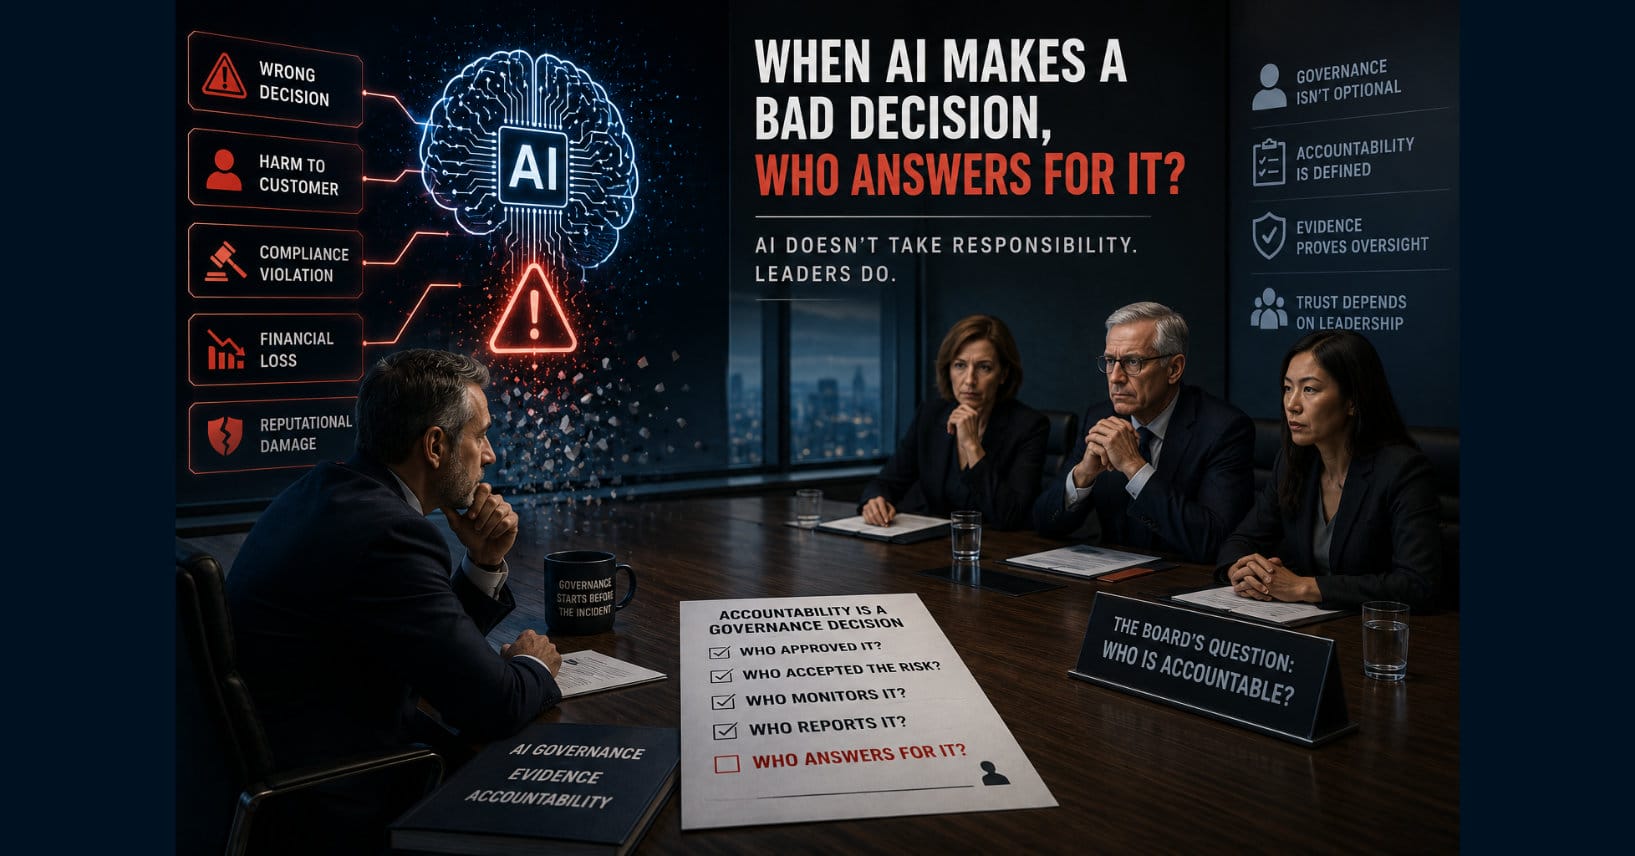
When AI Makes a Bad Decision, Who Answers for It?
Write the WordPress excerpt, summary, tags, and SEO for article 11. When AI Makes a Bad Decision, Who Answers for It?
Insights
Cyber Governance Articles
Analysis and practical guidance for boards, executives, and governance leaders building measurable, defensible cybersecurity oversight.