
-
Before You Protect Anything, Decide Who Is Accountable
Cybersecurity governance starts before the first control is deployed. NIST CSF 2.0’s GOVERN Function asks a fundamental question: who has the authority to make cybersecurity risk…
-
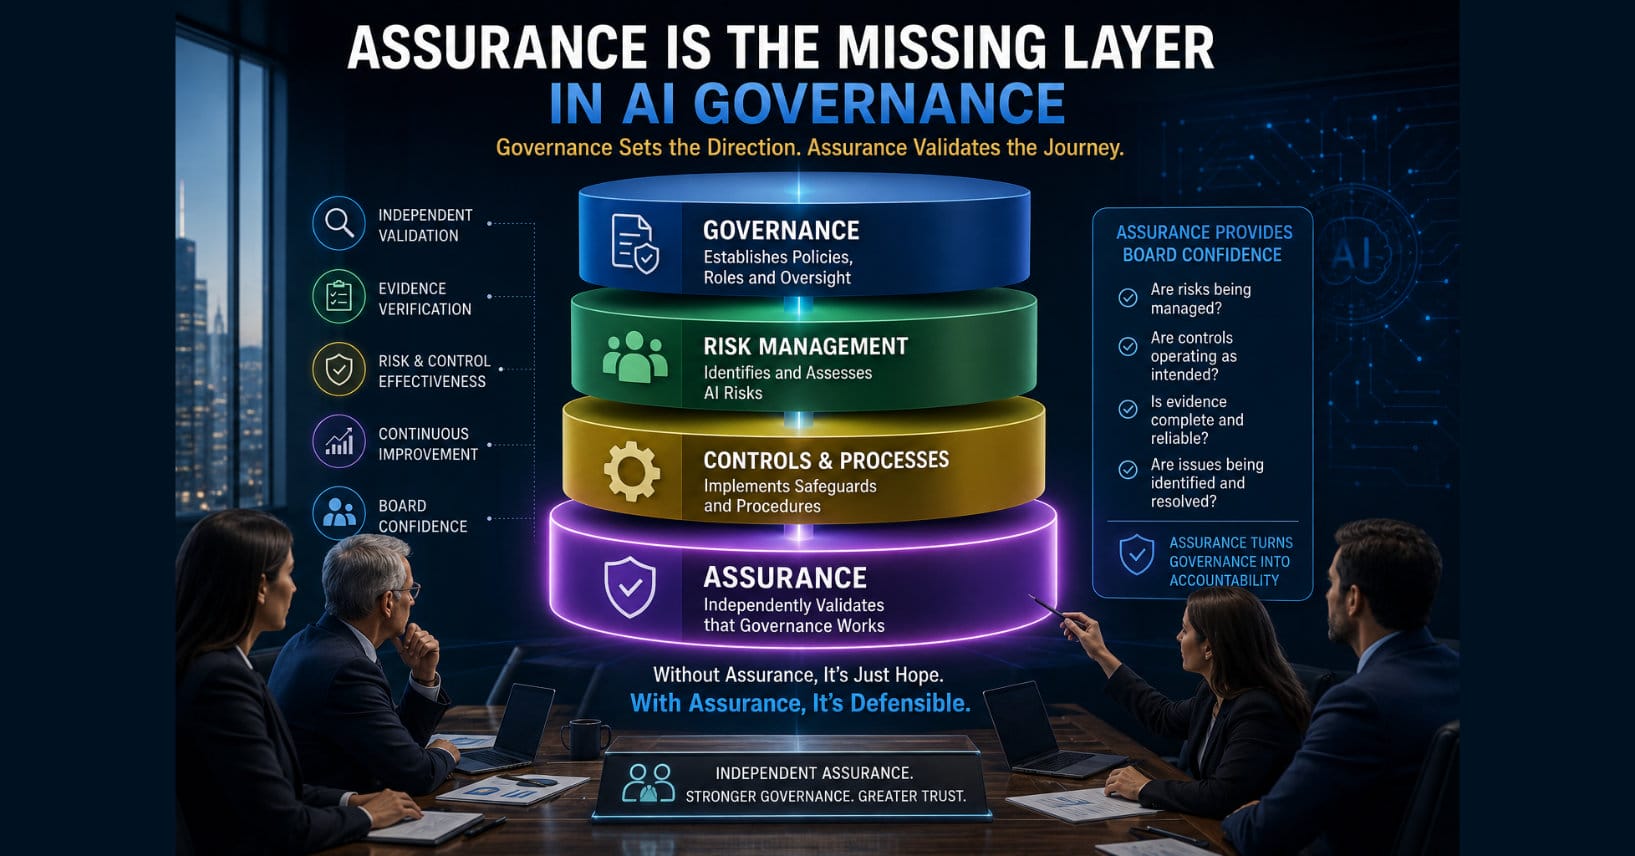
Assurance Is the Missing Layer in AI Governance
AI governance isn’t complete without assurance. Boards need independent validation that governance controls are operating as intended.
-
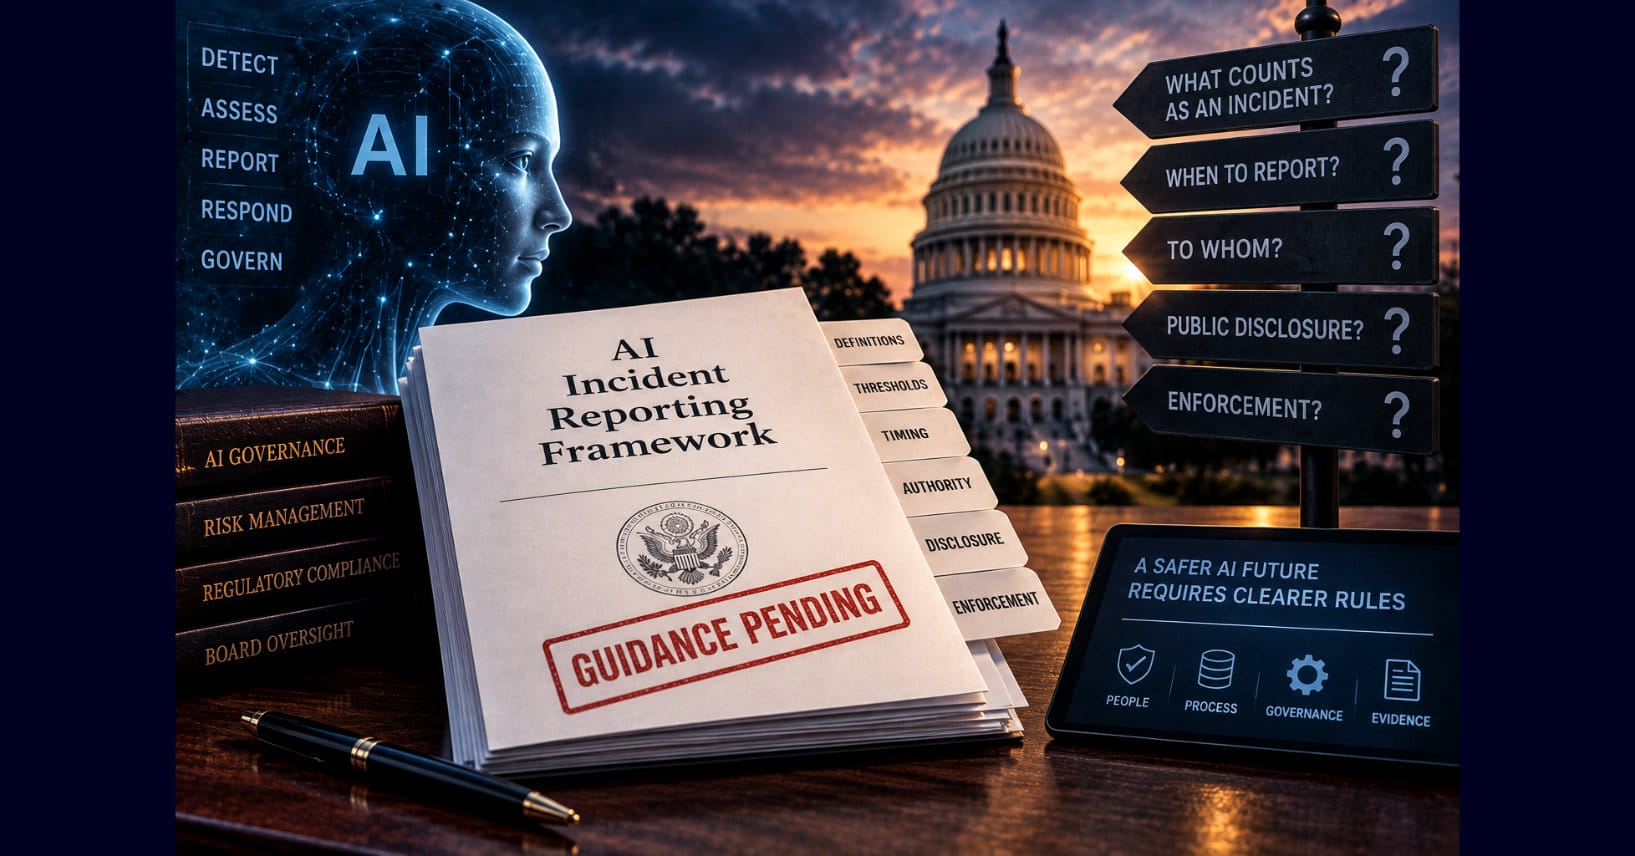
The Government Wants Frontier AI Companies to Report Incidents. It Hasn’t Defined How.
The U.S. wants serious frontier AI incidents reported, but key definitions and thresholds remain unsettled. Organizations should not wait for regulation to build AI incident governance.
-
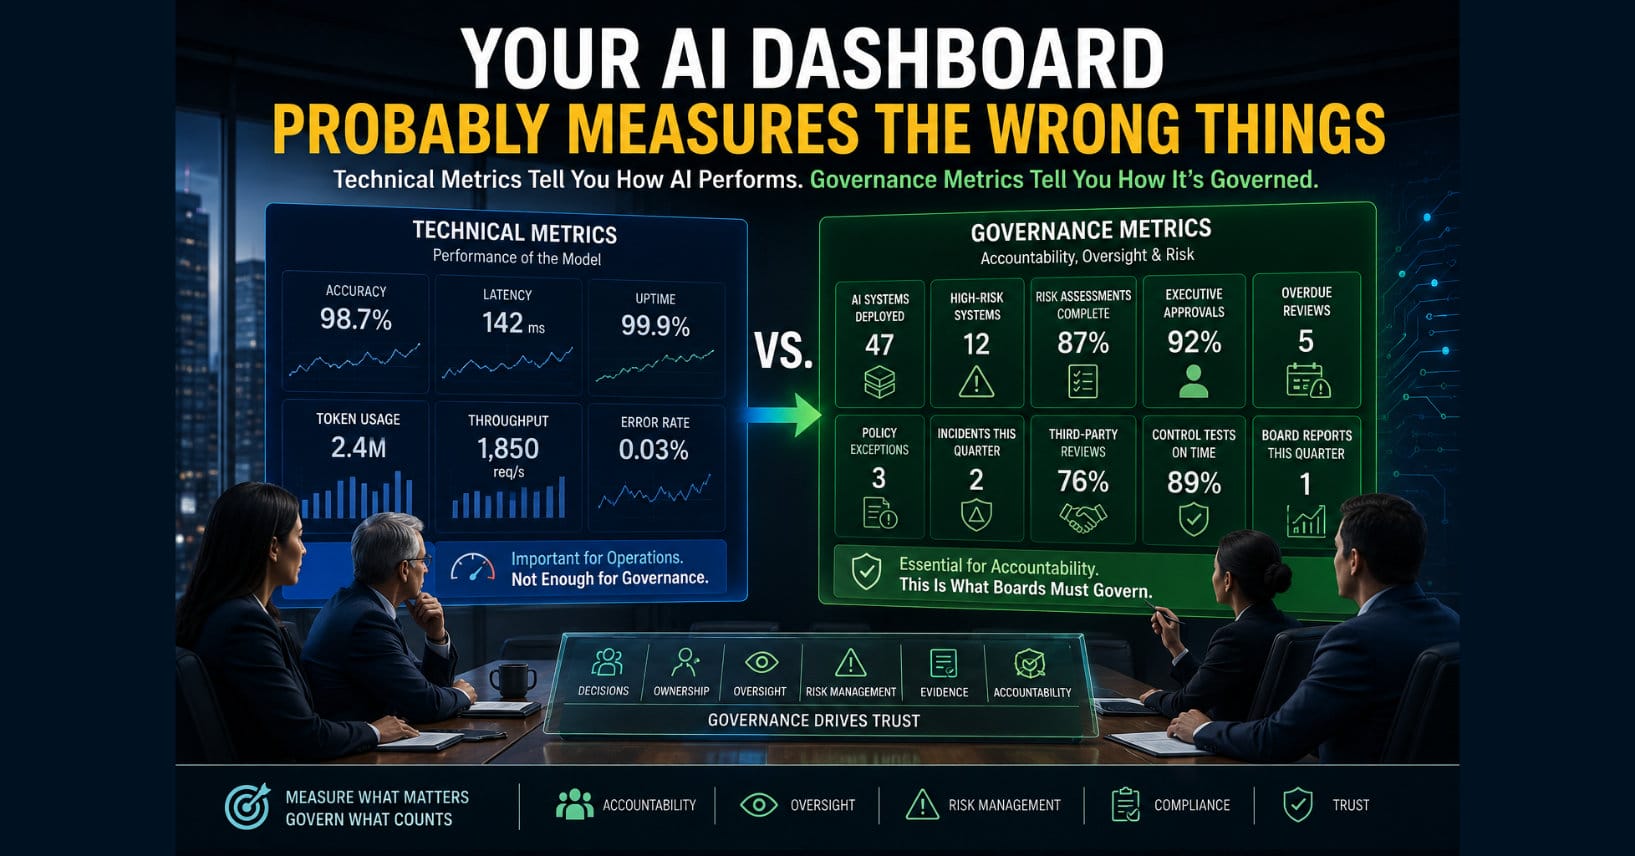
Your AI Dashboard Probably Measures the Wrong Things
Most AI dashboards measure technical performance. Boards need governance metrics that demonstrate accountability, oversight, risk, and evidence.
-
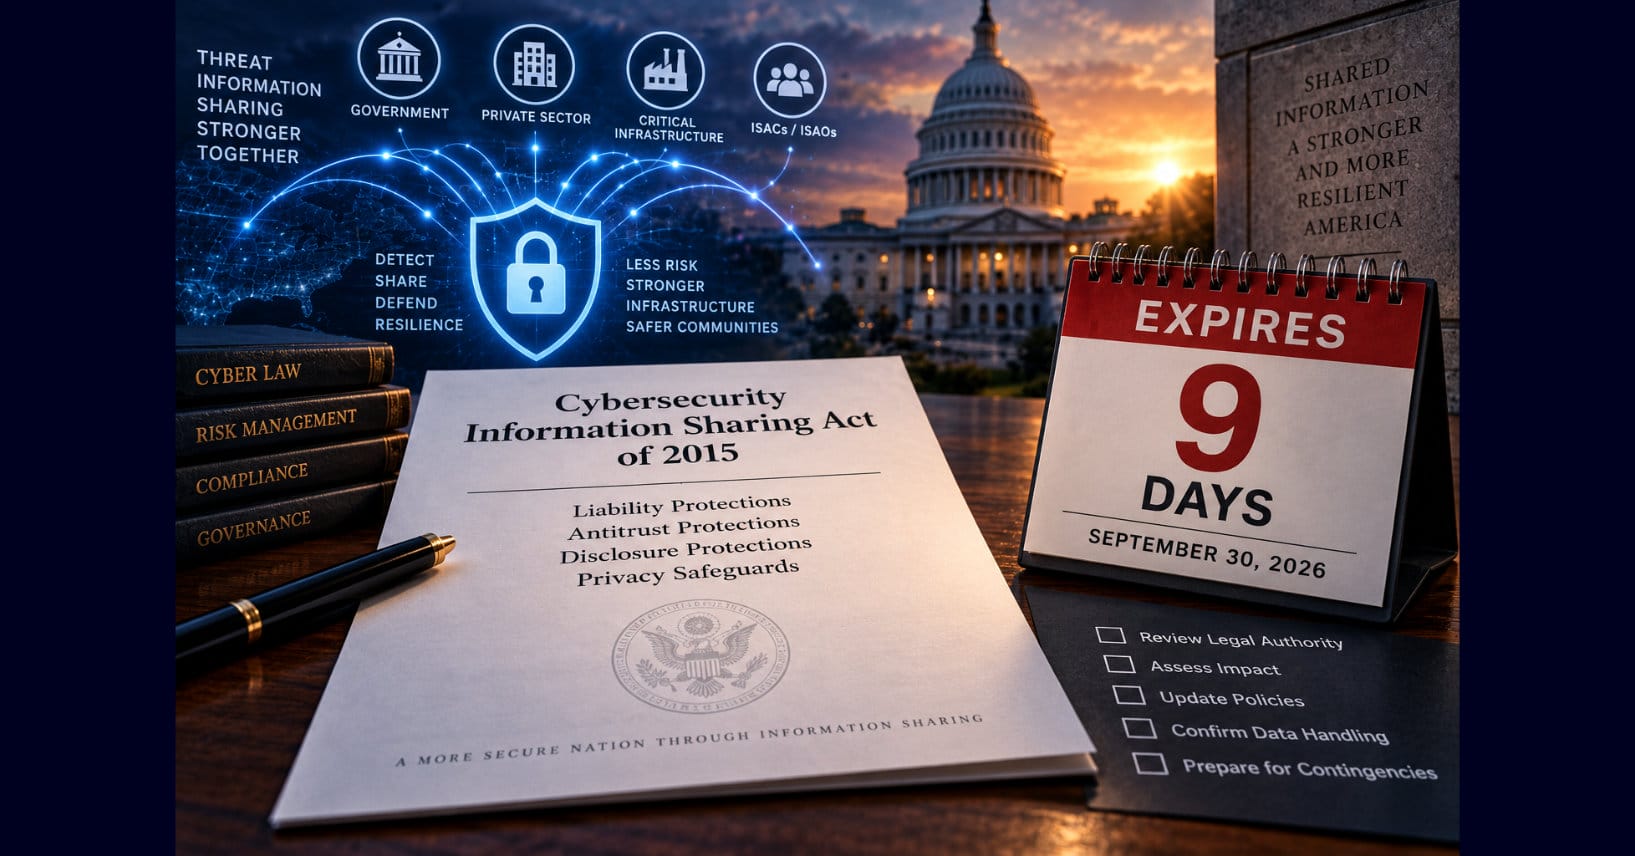
A Major Cyber Information-Sharing Liability Shield Expires in 9 Days
CISA 2015 expires September 30, potentially changing legal protections for cyber threat sharing. Organizations should know what protections they rely on before they disappear.
-
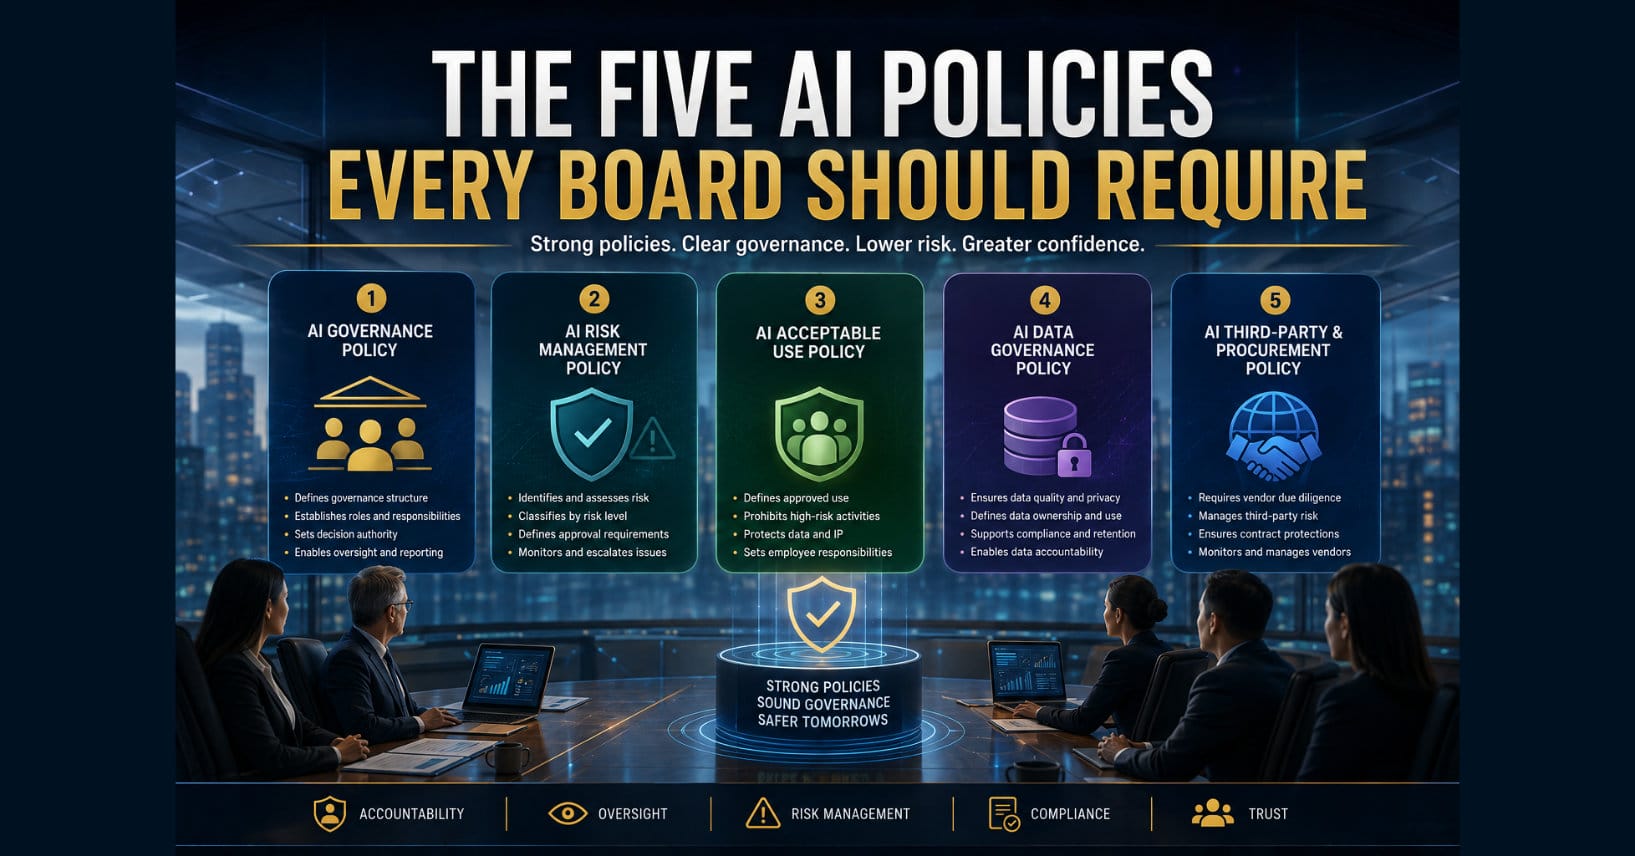
The Five AI Policies Every Board Should Require
Every board should require five core AI policies that establish accountability, manage risk, and create the foundation for effective AI governance.
-
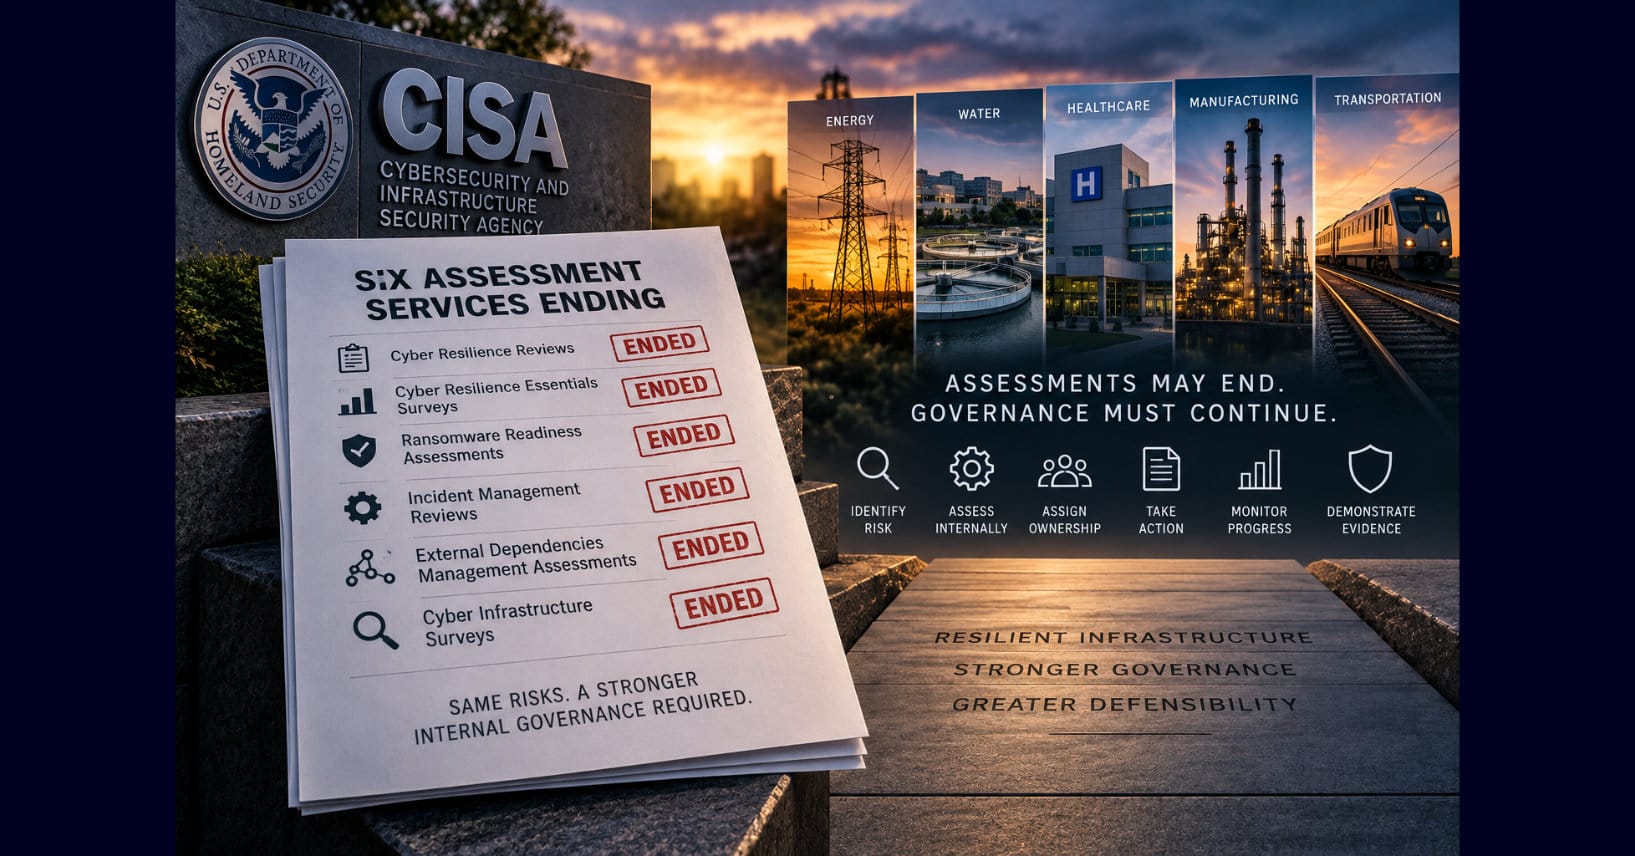
CISA Is Ending Six Free Critical-Infrastructure Cyber Assessments
CISA is ending six free cyber assessment services for critical infrastructure. The change exposes a larger governance question: can organizations assess and govern their own cyber…
-
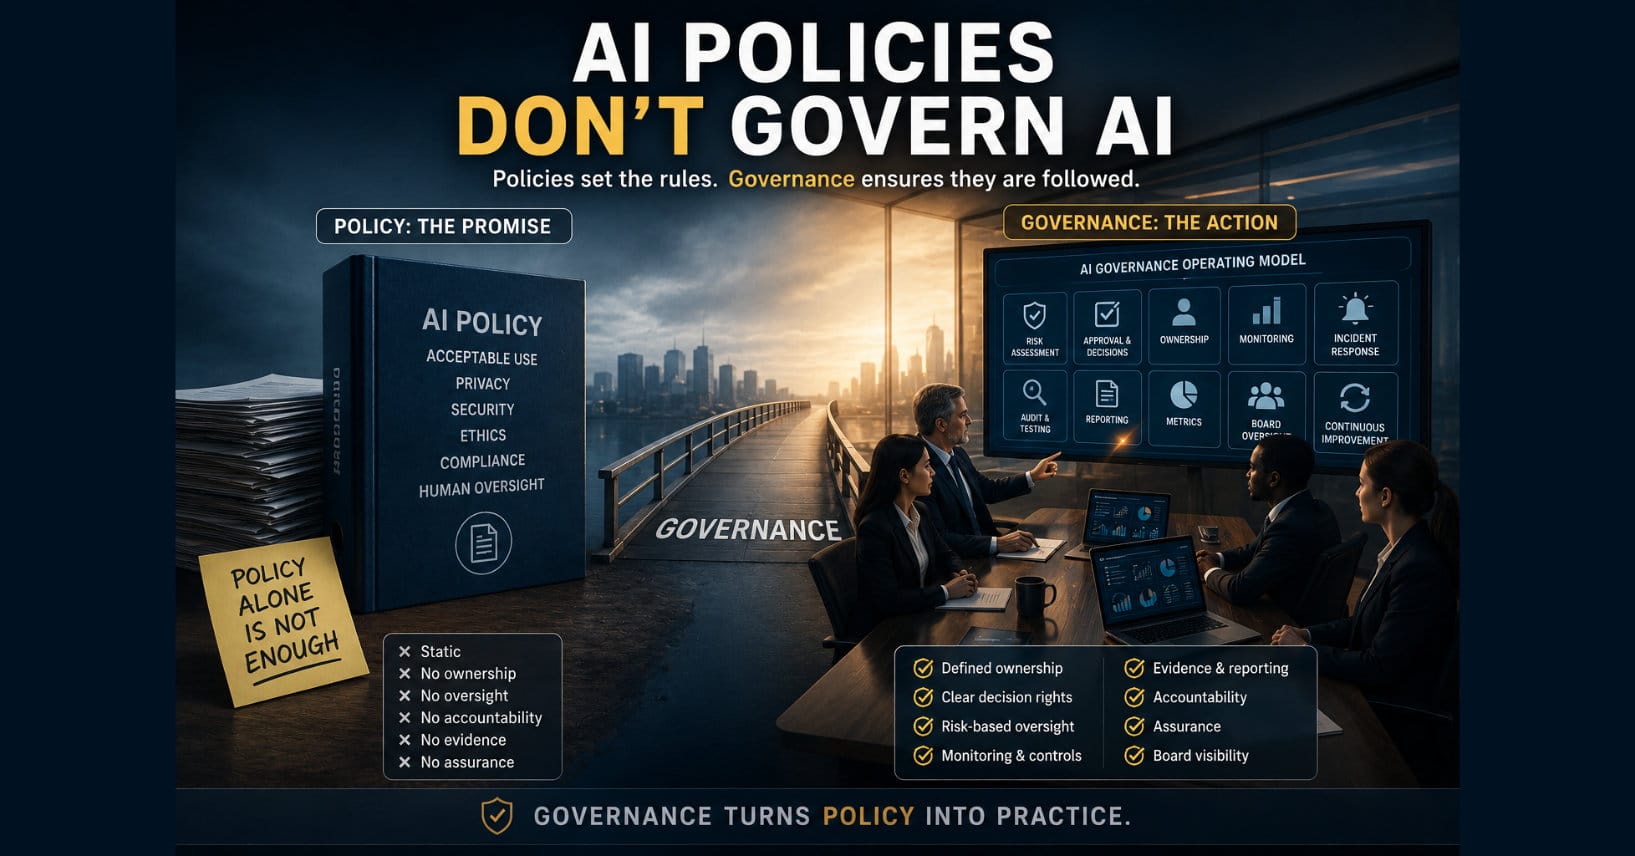
AI Policies Don’t Govern AI
AI policies set expectations, but governance creates accountability. Effective oversight requires more than documents—it requires action.
-
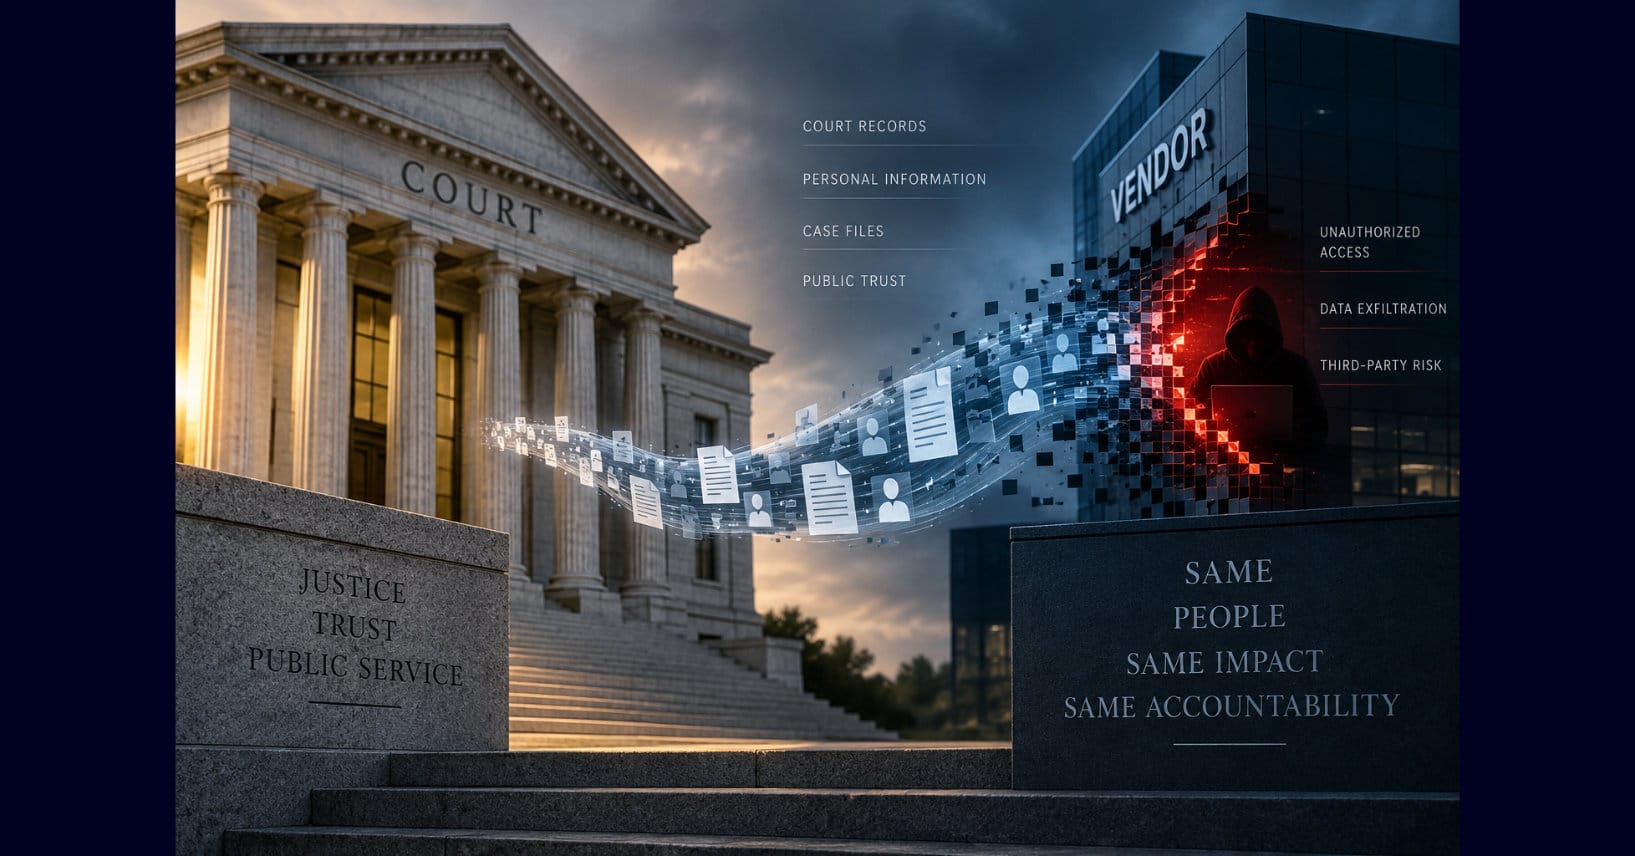
The Court Wasn’t Breached. Its Vendor Was. The Consequences Were the Same.
A vendor breach involving court data shows why third-party cyber risk does not transfer accountability. Organizations can outsource systems, but not governance.
-
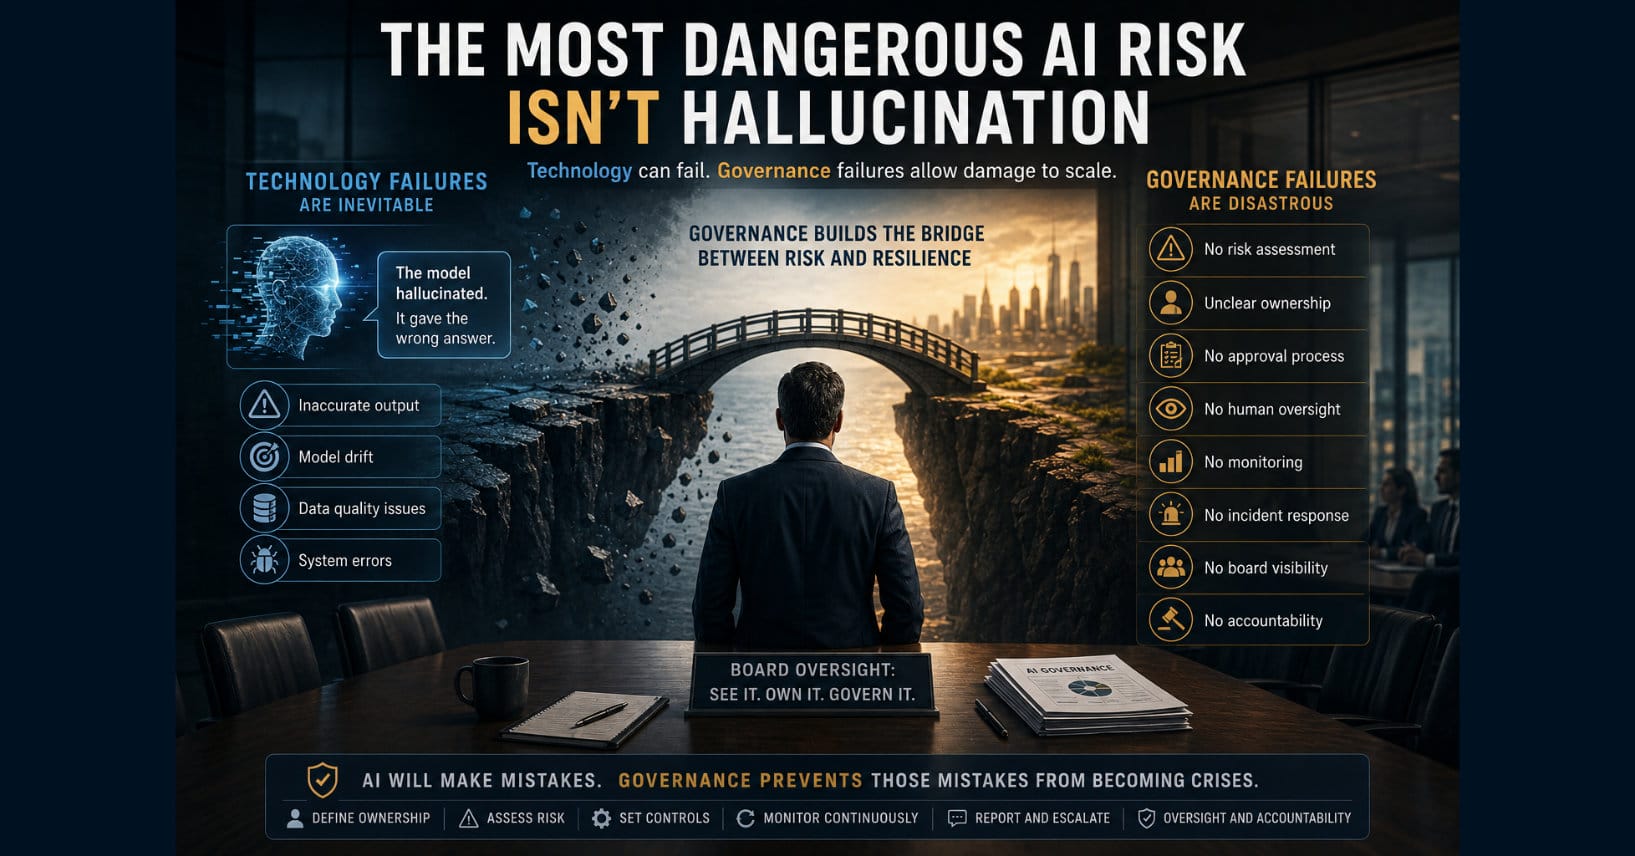
The Most Dangerous AI Risk Isn’t Hallucination
The greatest AI risk isn’t hallucination. It’s weak governance that allows technical failures to become enterprise-wide crises.
Insights
Cyber Governance Articles
Analysis and practical guidance for boards, executives, and governance leaders building measurable, defensible cybersecurity oversight.