-
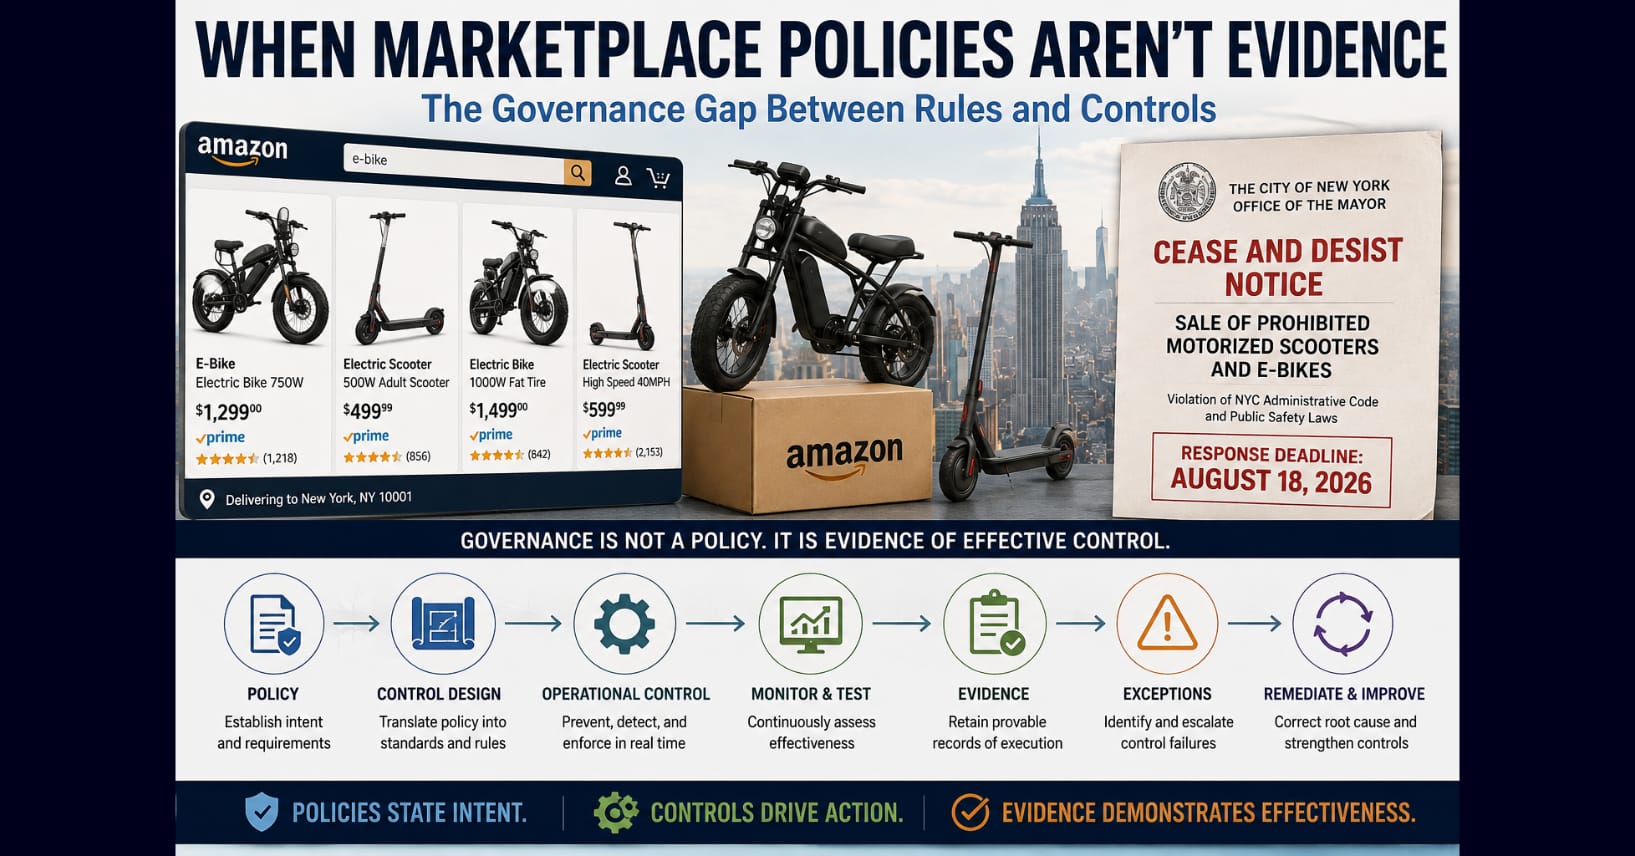
When Marketplace Policies Aren’t Evidence
Amazon’s response to New York City’s crackdown on prohibited e-bikes and scooters exposes a larger governance question: when companies have compliance policies, can they prove…
-
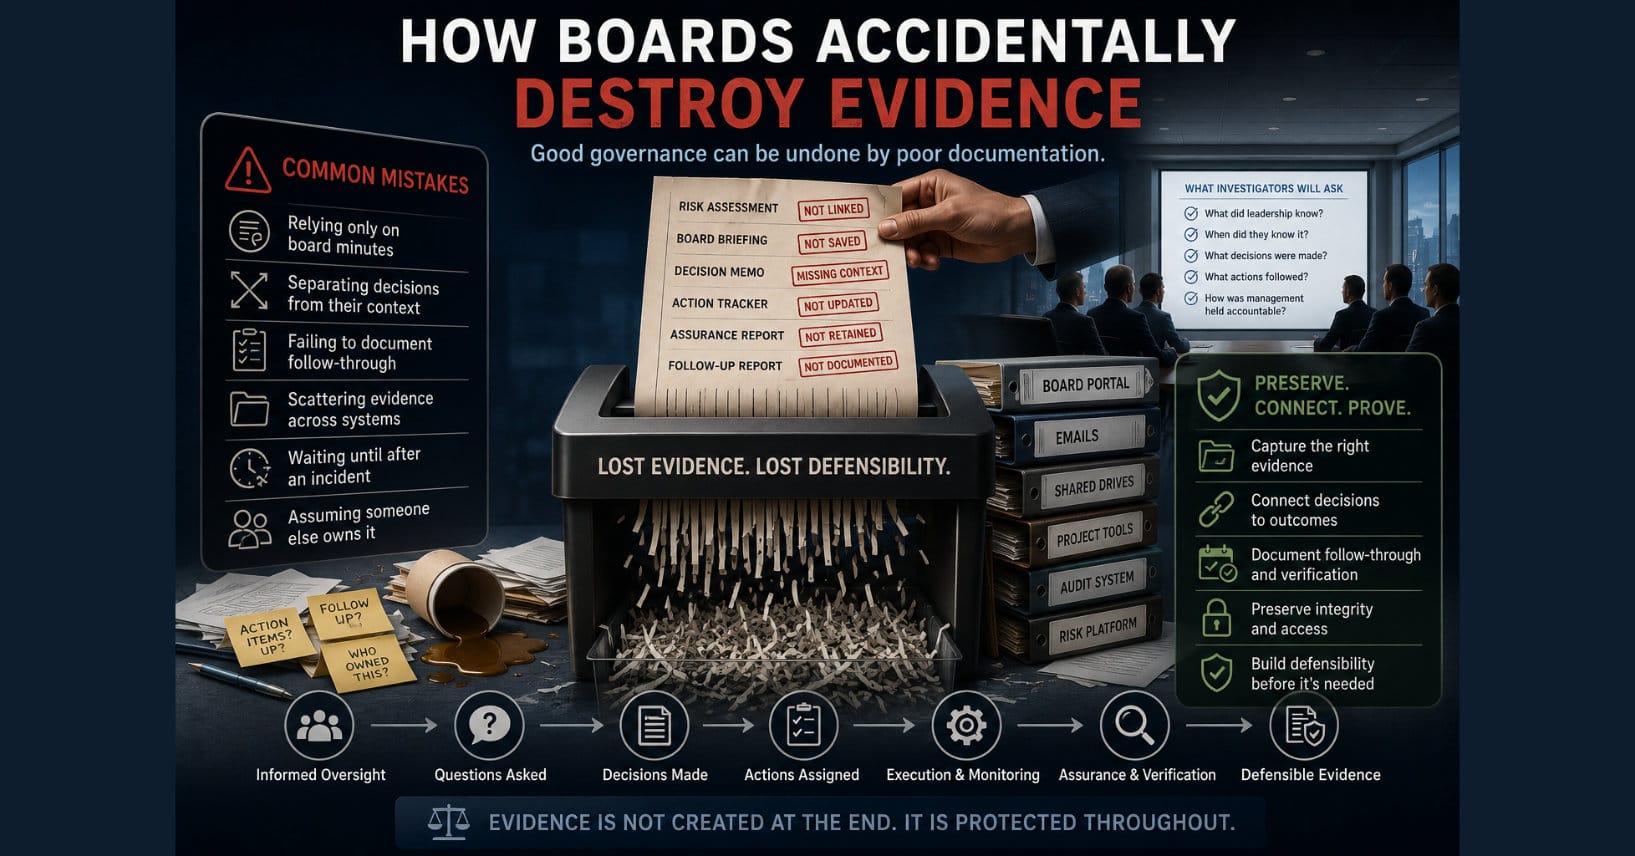
How Boards Accidentally Destroy Evidence
Many organizations lose their strongest governance evidence long before a cyber incident occurs. Learn the common board practices that unintentionally destroy documentation, weaken accountability, and…
-
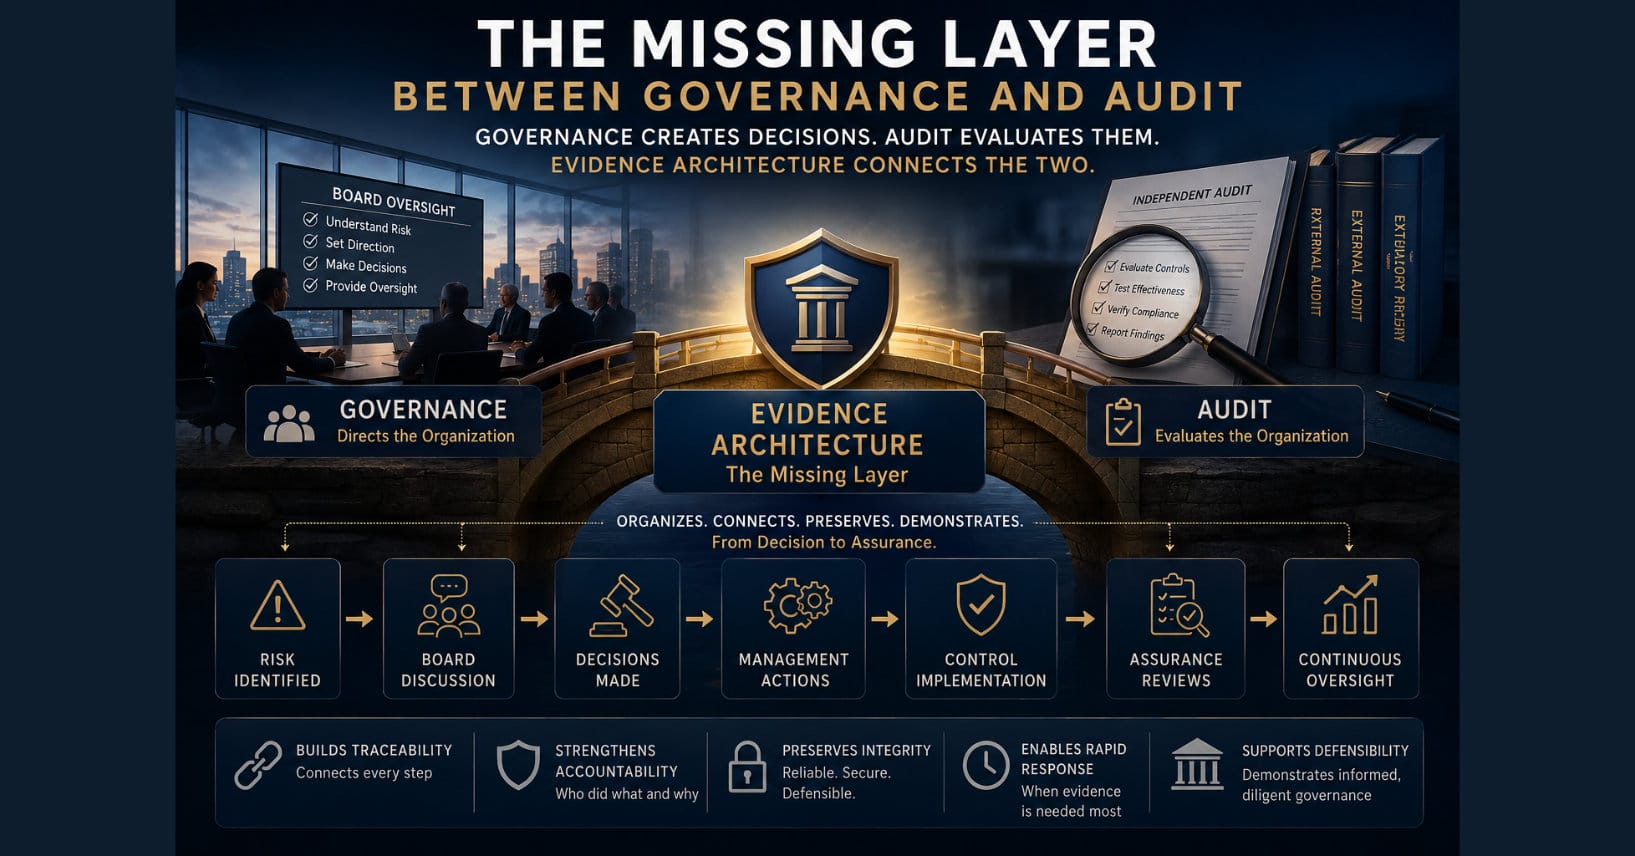
The Missing Layer Between Governance and Audit
Boards create governance. Auditors validate it. Between them lies assurance—the critical function that continuously verifies controls, exposes weaknesses, and generates the evidence that makes governance…
-
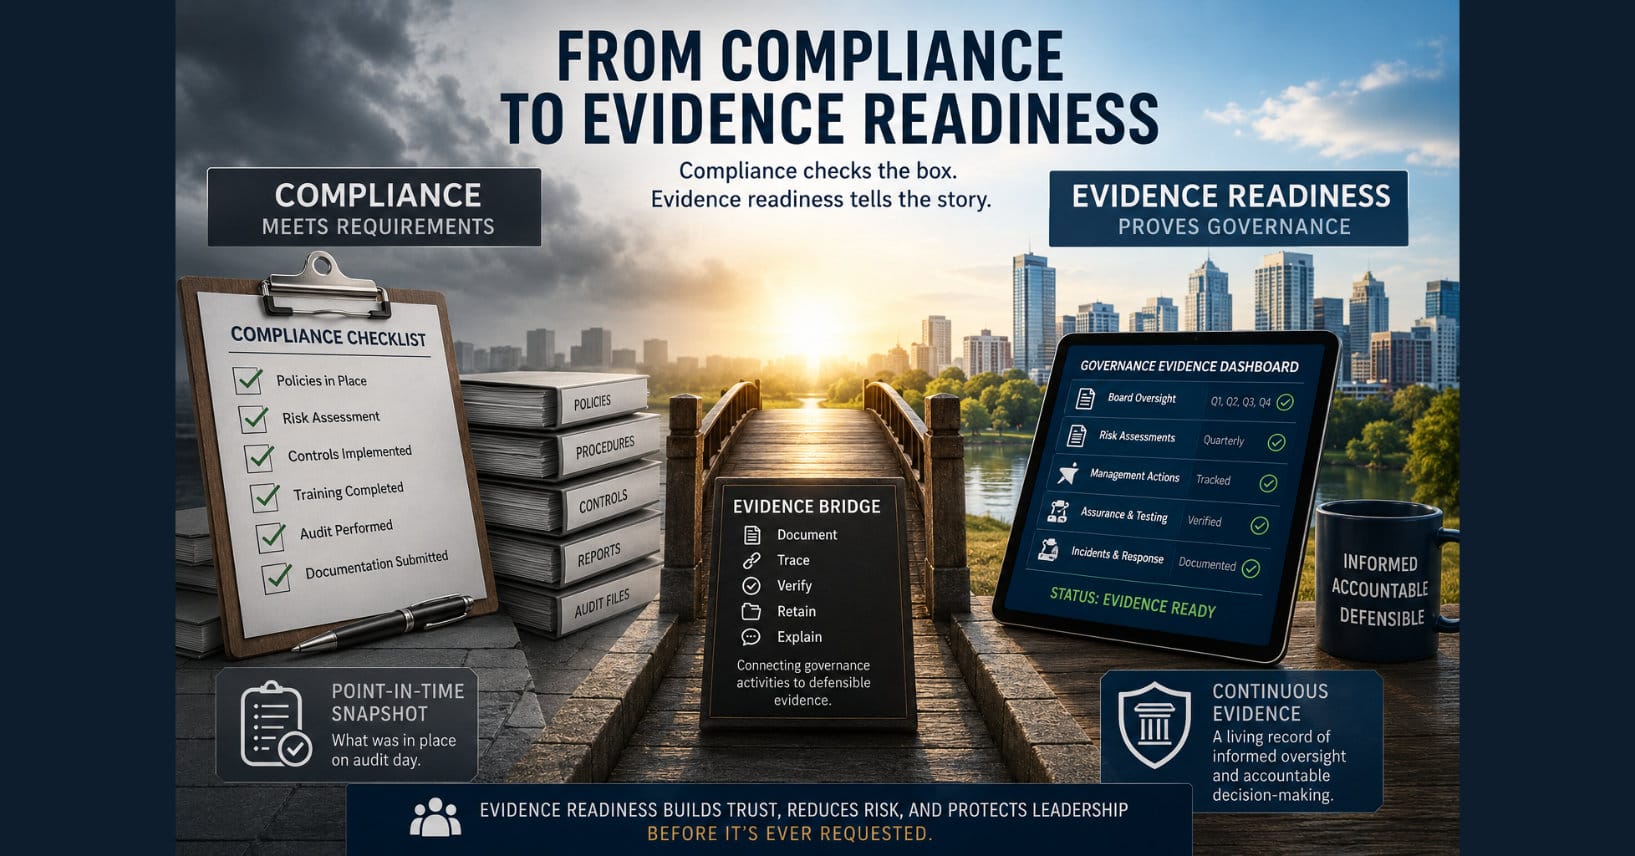
From Compliance to Evidence Readiness
Compliance confirms that requirements are met. Evidence readiness proves that leadership exercised informed oversight before regulators, auditors, or investigators ask. Organizations that build governance evidence…
-
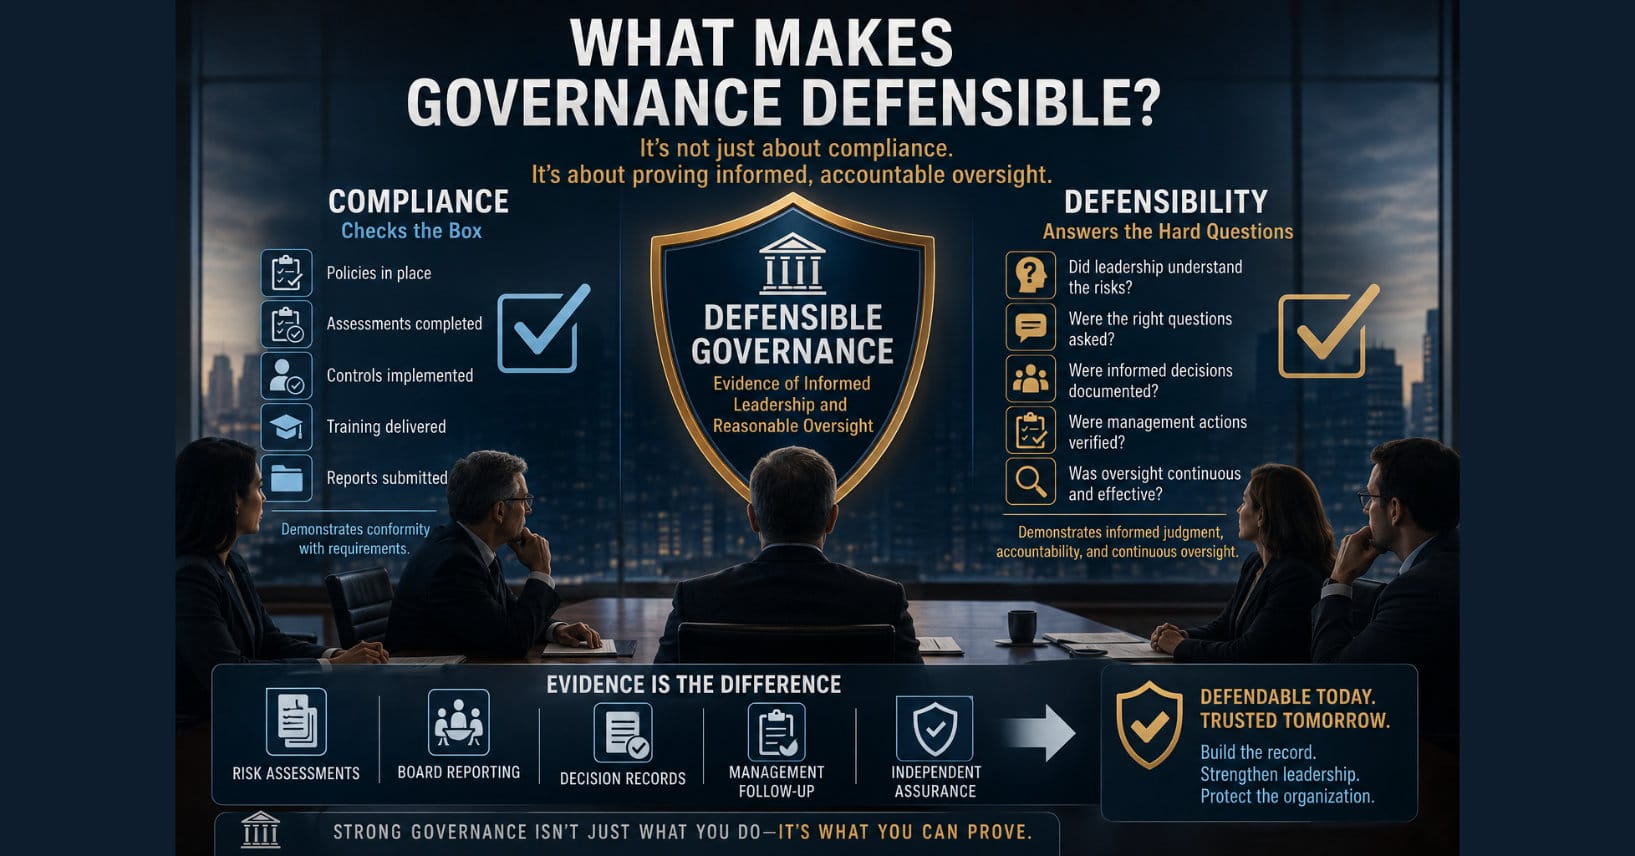
What Makes Governance Defensible?
What separates organizations that survive cyber scrutiny from those that don’t? Defensible governance is built on evidence, accountability, and disciplined oversight.
-
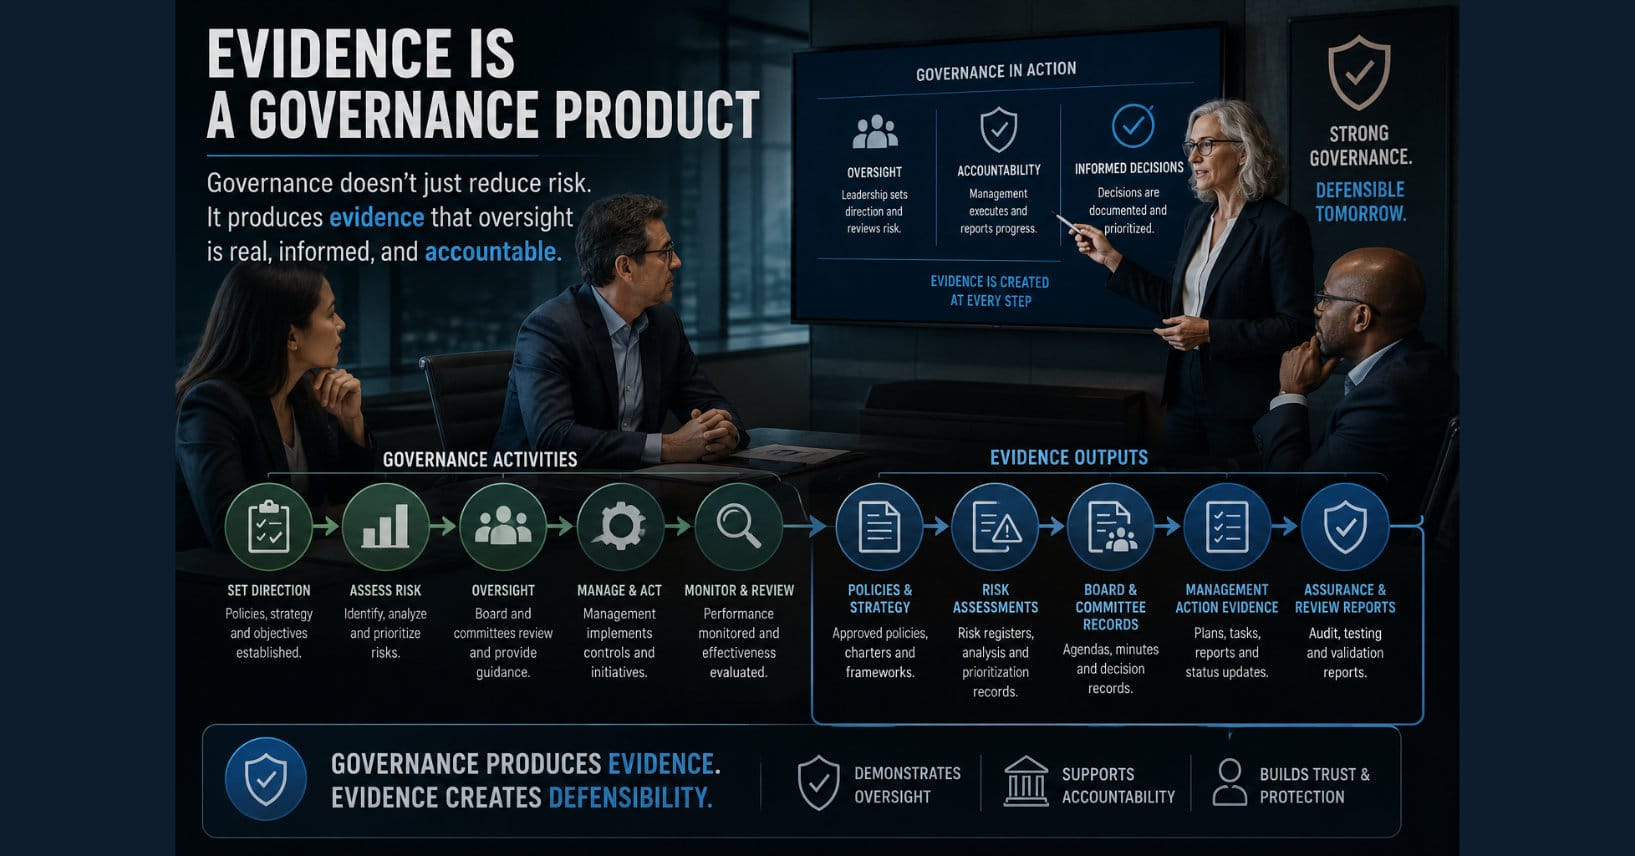
Evidence Is a Governance Product
Cybersecurity governance is often judged after an incident, but the strongest evidence is created long before a crisis occurs. This article explains why governance itself…
-
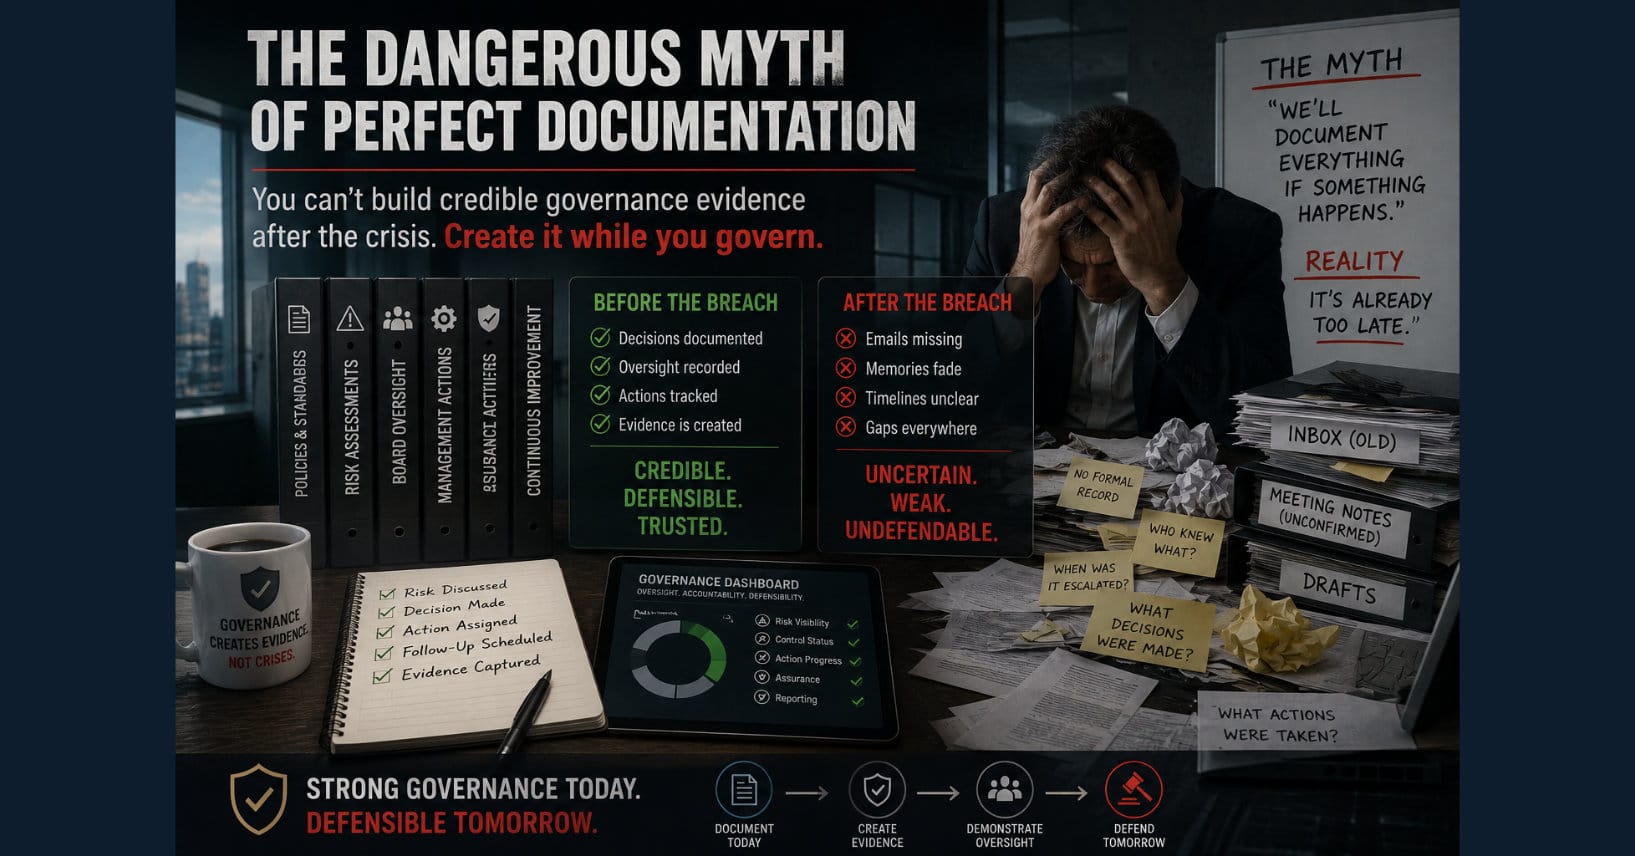
The Dangerous Myth of Perfect Documentation
Many organizations believe they can reconstruct governance evidence after a cyber incident. They can’t. Discover why contemporaneous documentation is far more credible than records assembled…
-
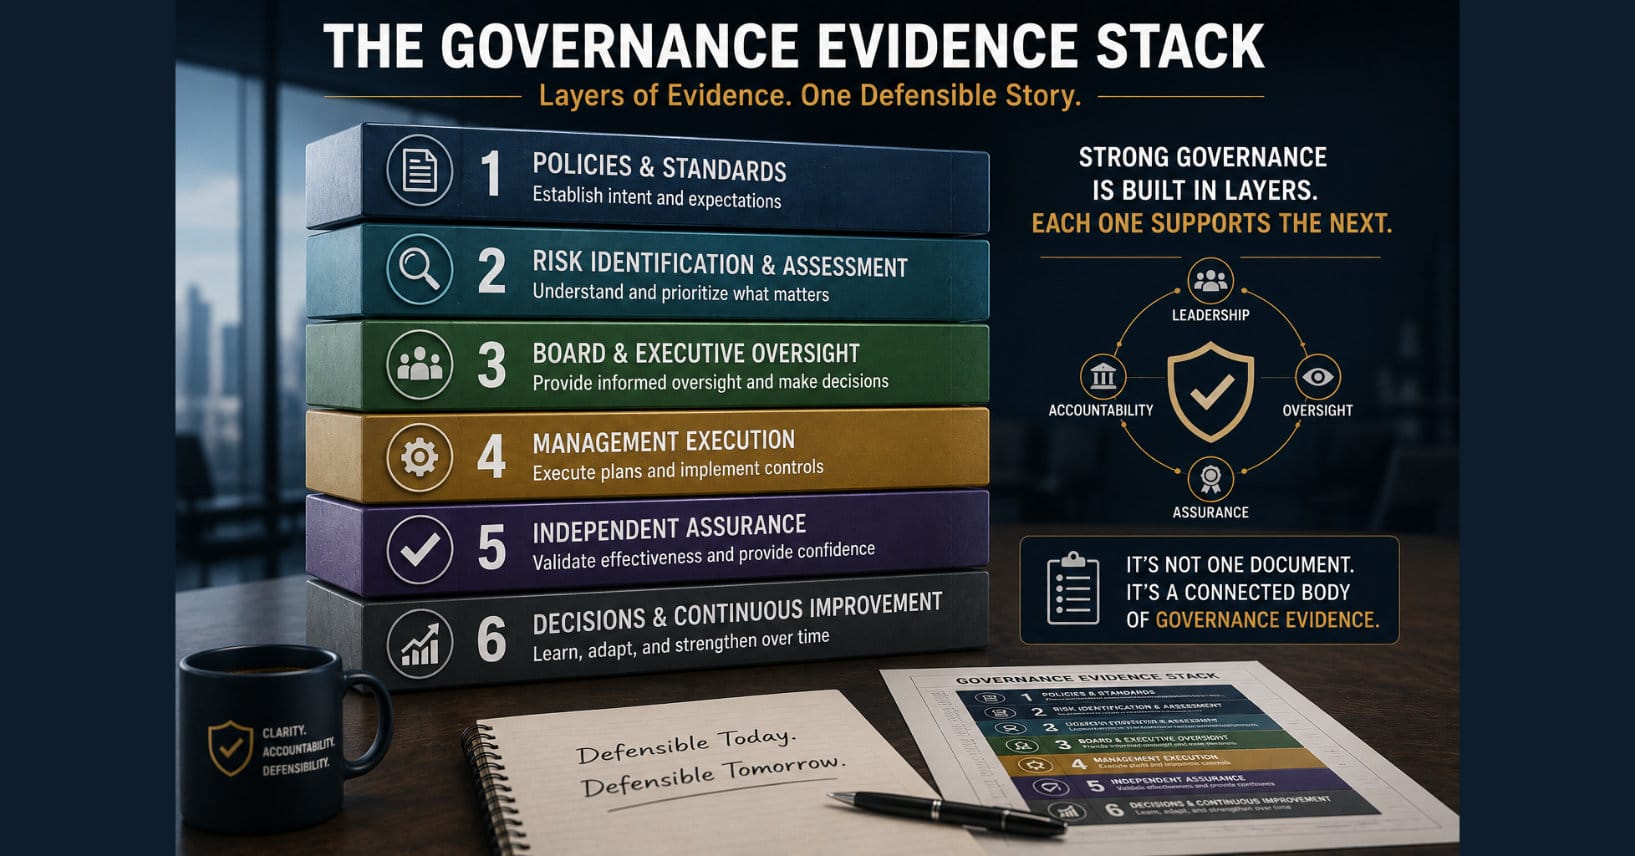
The Governance Evidence Stack
Good governance is not proven by a single document. It is demonstrated through a connected body of evidence spanning policy, risk, oversight, execution, assurance, and…
-
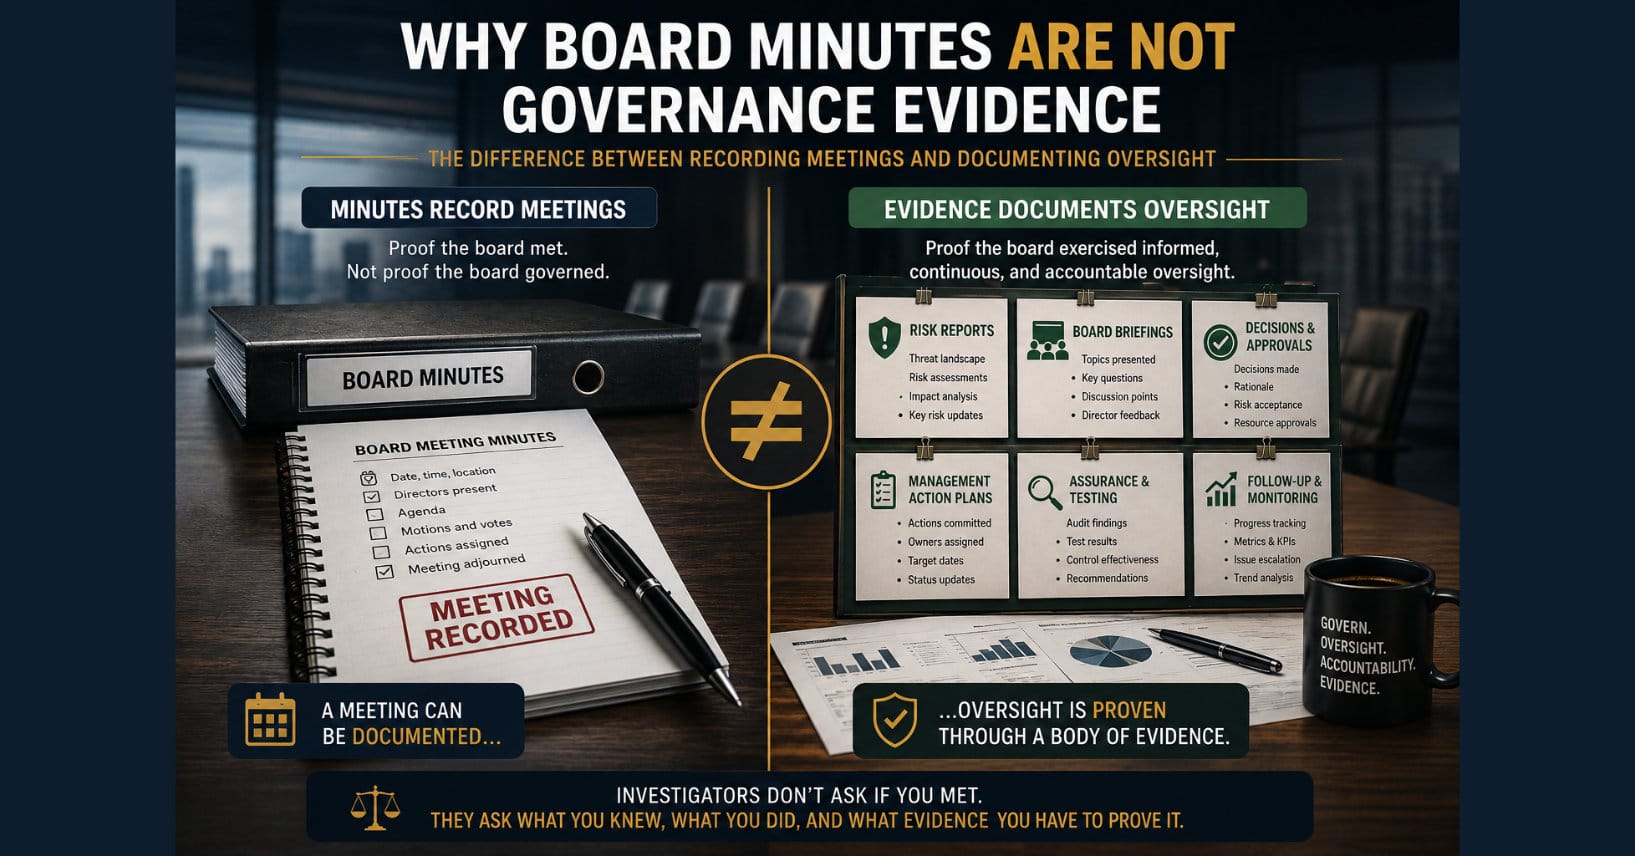
Why Board Minutes Are Not Governance Evidence
Board minutes document discussions, but they rarely prove effective oversight. Learn why defensible governance requires evidence beyond meeting records.
-
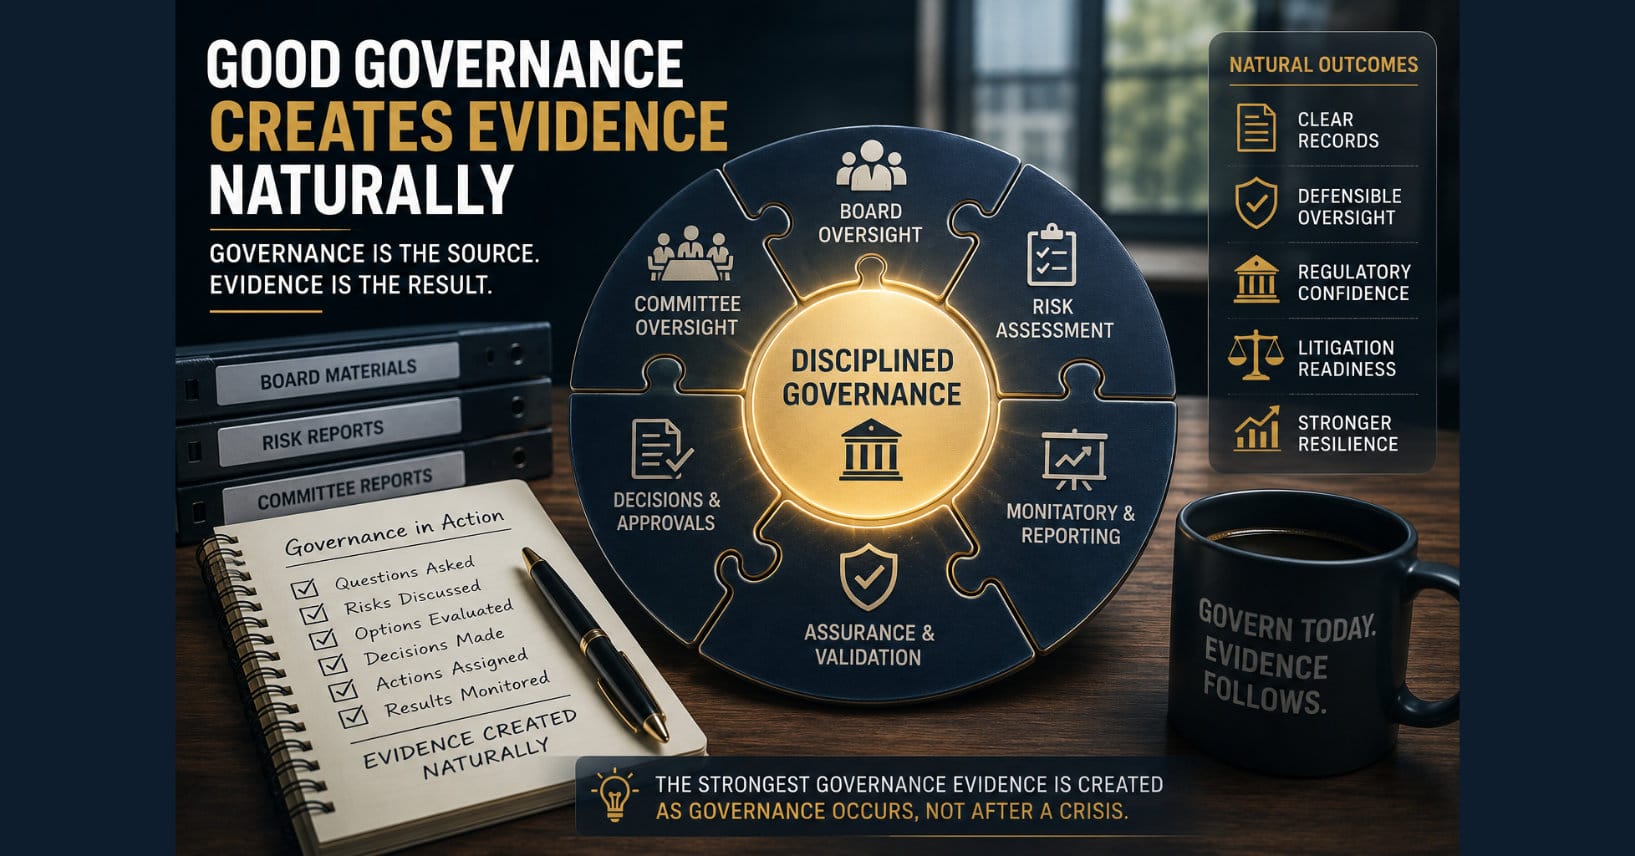
Good Governance Creates Evidence Naturally
The strongest governance evidence isn’t assembled after a cyber incident—it is created as governance occurs. Discover the central principle behind the Defensible Evidence Framework™ and…
-
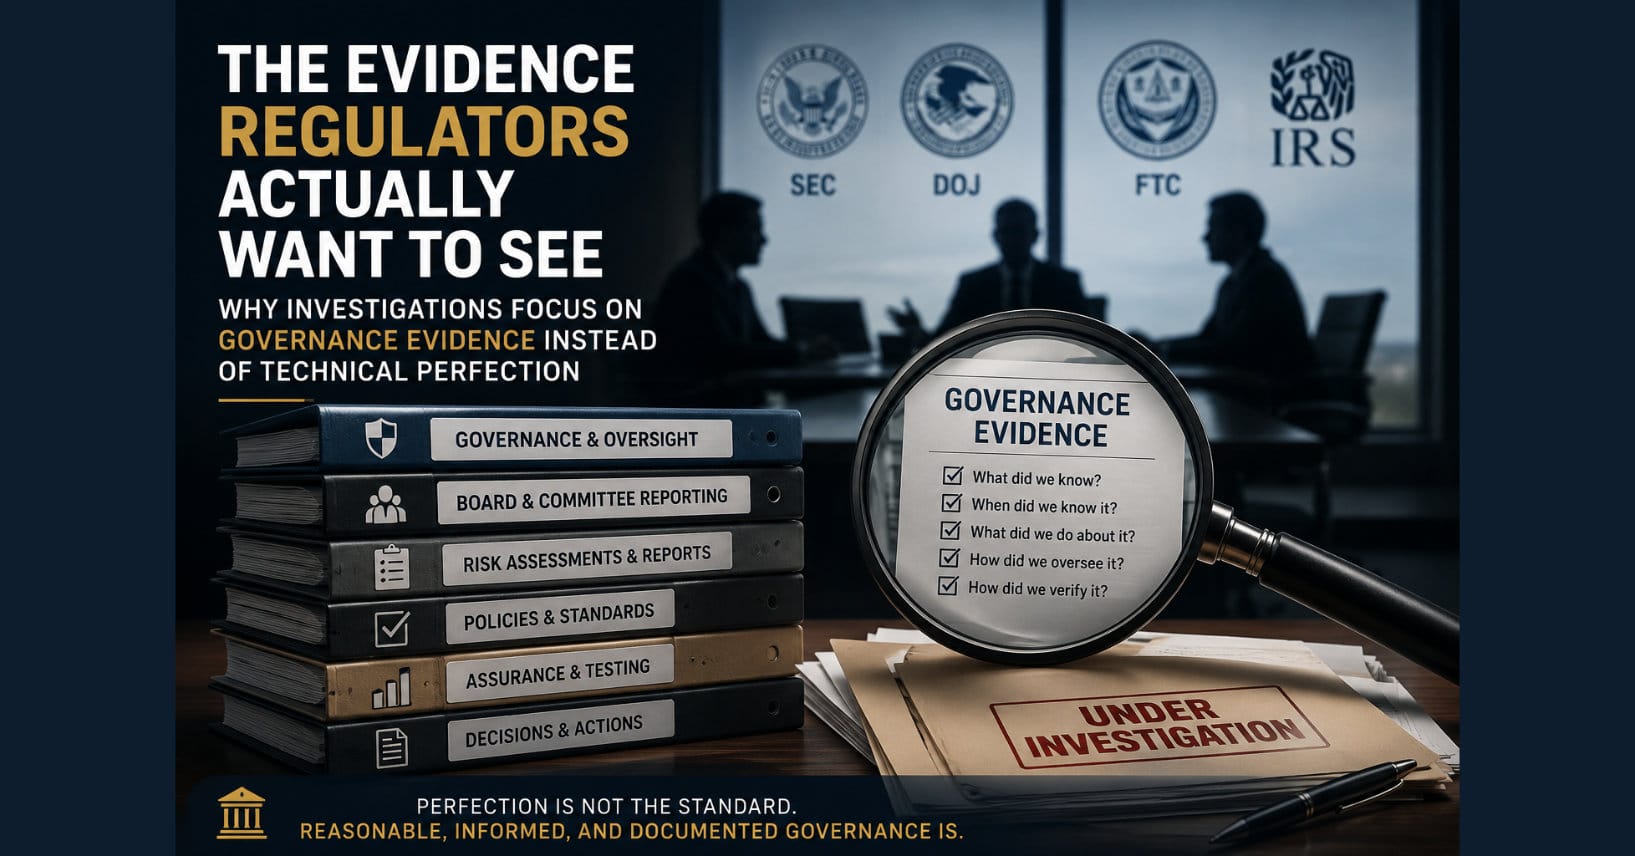
The Evidence Regulators Actually Want to See
After a cyber incident, investigators rarely begin by asking what security tools an organization deployed. They ask what leadership knew, when they knew it, and…